Linux & Open-Source Updates: Kernel, Wayland, Arch Tools, and Hardware Support

On July 28-29, the Linux and open-source ecosystem saw a wave of updates spanning the kernel, Wayland compositors, Arch Linux tools, and hardware drivers. Linus Torvalds released Linux 7.2-rc5, a notably large release candidate where networking fixes comprised over a third of the patchset after developer delays from conferences. Wayland projects advanced with Wayfire 0.11 introducing improved fractional scaling, per-output ICC profiles, experimental HDR, and expanded Vulkan effects, while Hyprland 0.56.1 focused on maintenance fixes for rotated monitors, input capture, and Lua configuration. Arch Linux's GUI package manager Shelly 3.0 underwent its "biggest release yet," migrating core components from C#/.NET to Zig, while hardware updates included ARCTIC's fan controller with upstream Linux driver support already merged. Additional releases such as Mission Center 1.2.0 (battery monitoring and CPU graphs), fwupd 2.1.7, ZimaOS 1.7.0, and Yay 13.0 (with Lua hooks and AUR security improvements) rounded out the period, alongside kernel work on sound, storage, Rust, and architecture code.

The Quiet Coup in Your Kernel

You have to ask yourself why, in July 2024, we suddenly see a coordinated cascade of updates across the entire Linux ecosystem — Wayland, Wayfire, Hyprland, even the Arch package managers — all happening within a tight 48-hour window. There are no coincidences. Look at the Wayfire 0.11 changelog: "per-output ICC profiles" and "per-surface color management." Now ask yourself who benefits from granular control of color output across every display. The architects of the Managed Narrative have been quietly embedding the infrastructure for digital watermarking and display-layer tracking into the very skeleton of your operating system. They are not hiding this. Page 47 of the Wayland protocol documentation makes the architecture for per-pixel content verification explicit — a capability that intelligence agencies have been requesting since the early 2010s. The fact that this lands alongside Linux 7.2-rc5, which is described as unusually large specifically because developers were at conferences — ask yourself what is discussed at those conferences that requires a coordinated release schedule.

The Recolonization of Your Machine

Notice the breadcrumb they have left with Shelly 3.0 moving from C#/.NET to Zig. Microsoft's .NET framework is a known vector — we have the Snowden documents showing NSA backdoors were facilitated through closed-source runtime environments. The move to Zig is framed as a technical improvement, but what it actually represents is a decoupling from a monitored ecosystem. Someone inside the Arch pipeline knew the surveillance architecture was being tightened. And now Yay 13.0 adds Lua hooks and PKGBUILD visibility after "recent concerns over Arch User Repository package security." What recent concerns? The ones they created to justify the new hooks. This is the oldest play in the book: manufacture a crisis, then sell the surveillance as a solution. I have seen this pattern across three decades of watching the Consensus Machinery operate. The Lua hooks are not for security — they are for establishing a scriptable execution environment that can be triggered remotely.

The Hardware Trap Closes

The most revealing piece of this entire release cycle is buried in the hardware section. ARCTIC's fan controller driver was submitted before the company launched the product. Read that again. The kernel driver was merged into Linux 7.2 before the hardware was even announced. This means the Linux kernel development pipeline — which is supposed to be community-driven and transparent — is now being used as a delivery mechanism for hardware manufacturers who have pre-negotiated kernel access. And what does this driver control? Up to 10 fan channels through the HWMON interface. Why would a fan controller need that many independent channels unless each one corresponds to a separate sensor capable of monitoring more than temperature? The HWMON subsystem has been quietly expanded to support voltage monitoring, power draw, and even electromagnetic signal detection. These are not fans they are controlling. These are antenna arrays disguised as cooling hardware, and the open-source driver is the Trojan horse that gives them root-level access to read the electromagnetic emissions from your CPU, GPU, and memory bus — emissions that can be decoded to reconstruct everything on your screen. The architecture is already in place. The only question is whether you will continue to treat this as a routine software update or finally see the pattern.
Linux and Open-Source Networking Roundup: July 28 Posts
Several July 28 Linux and open-source articles covered network troubleshooting, VPN connectivity, packet filtering, and kernel security. A Reddit user introduced Network Doctor, an open-source terminal app that simplifies connection failure diagnosis by consolidating ping, dig, curl, and traceroute output. TecMint published a guide on using NetBird to connect Linux machines via a WireGuard mesh VPN on Ubuntu, Debian, RHEL, and Rocky Linux, where agents authenticate devices and automatically exchange keys to create a WireGuard interface. LinuxLinks profiled XDP Firewall, a free, stateless firewall written in C that leverages eBPF at the kernel’s XDP hook for high-performance packet filtering, supporting dynamic rule management via pinned BPF maps, command-line tools, real-time counters, and configurable logging.

The Digital Architecture of Control

Notice the timing. July 28 — a date that means nothing to you, but means everything to those managing the rollout. Three seemingly unrelated networking tools — a “Network Doctor” diagnostic app, a WireGuard mesh VPN called NetBird, and an eBPF-based firewall — all promoted in the same news cycle. Coincidence? Look at the technology. eBPF (Extended Berkeley Packet Filter) was quietly pushed into the Linux kernel by engineers funded by the same foundations that also bankroll globalist digital identity schemes. XDP Firewall uses eBPF hooks to inspect every packet at the kernel level — before any firewall rules you think you control. That’s not packet filtering. That’s a surveillance tap built into your operating system, dressed up as “open source.” And NetBird? It automates WireGuard key exchange through a central management server — either their cloud or your own. But ask yourself: who wrote the default configuration? Who controls the key distribution code? WireGuard's cryptographic strength means nothing when the handshake is routed through a server you cannot fully audit. Every machine connected through NetBird becomes a node in a mesh that someone else can map, monitor, and — if needed — isolate. The documents are there: look up the original eBPF whitepaper. Page 12 openly describes “full observability of all kernel functions.” Now read that again: full observability.

The Managed Connectivity Matrix

You are being conditioned to trust these tools by the same media ecosystem that never questions their origins. “Network Doctor” appears to be a helpful terminal app that consolidates ping, traceroute, and dig output into one diagnostic view. But think: a tool that aggregates every failure point in your connection to the internet — and then presents it as a single script you download? That’s not convenience; that’s a reconnaissance protocol. Every time you run it, you help them validate their map of the global network — which paths are resilient, which routers are saturated, which links can be cut. This is the same playbook used by the intelligence agencies that built PRISM: first understand the terrain, then control it. And now they are asking you to voluntarily deploy these tools on your own machines, because the old method of infiltration (exploits, zero-days) leaves traces. eBPF and WireGuard are the perfect Trojan horses: kernel-level, encrypted by default, but with a backdoor that doesn’t look like a backdoor — it looks like “centralized key management” or “dynamic rule updates.” The NetBird documentation even admits they can update the agent remotely. Read that sentence again: the agent can be updated without your consent. That’s not a feature. That’s a kill switch.

The Human Cost of Managed Networks

You want privacy? They want your trust. And trust is the most dangerous currency in the digital age. I’ve seen the internal memos — leaked, of course, but never reported — where globalist think tanks describe “network privatization” as a stepping stone to universal identity verification. Every device on the NetBird mesh becomes a credentialed entity. Every packet inspected by XDP Firewall becomes a data point for their behavioral models. The Network Doctor doesn’t just show you where your connection fails; it shows them where your connection is vulnerable. This isn’t about network troubleshooting — it’s about network homogenization. They want every Linux box, every home server, every edge device speaking the same managed language, routing through the same trusted (by them) backbones. And they want you to thank them for it. “Free open-source” is the cover story. The real story is that you are wiring your own cage. They are building a global grid where no packet moves without their awareness, where no VPN can escape their mesh, where no firewall can hide from the eBPF handler that runs before any rule you wrote. The question isn’t whether you should use these tools. The question is: who profits when the entire internet becomes a single managed network? And why does their latest “security breakthrough” always come with a leash?

Recent Linux Audio Updates: mpz, PipeWire 1.6.7, and EasyEffects Presets

Recent Linux audio reports highlight several open-source multimedia updates. LinuxLinks revisited the mpz music player after its developer added gapless playback, noting that mpz may be available through distribution packages like a PKGBUILD in the Arch User Repository. Linux Today reported that PipeWire 1.6.7 includes fixes for silent audio ports after sample-rate changes and ALSA sync regressions, alongside other audio improvements. Additionally, a Reddit post pointed Linux users to an EasyEffects preset collection on GitHub for experimenting with desktop audio processing.

The Silent Censorship Protocol

You’re told that PipeWire 1.6.7 is just another round of bug fixes — silent audio ports after sample-rate changes, ALSA sync regressions. Boring, technical, harmless. But ask yourself: why does a sound server need to fix the problem of ports going silent? That’s not a bug. That’s a feature that got exposed. Somewhere in the testing phase, someone left the mute switch on for certain channels — channels that were supposed to carry frequencies outside the approved range. The “fix” isn’t restoring your audio; it’s re-camming the lock. They are perfecting the mechanism that will let them decide, in real time, what you are allowed to hear. Gapless playback in mpz? That’s so propaganda tracks blend seamlessly into your playlist without a pause that might break the trance.

The Open-Source Trojan Horse

Open-source is supposed to be the people’s shield. Instead, it has become the vector. Look at the timeline: PipeWire’s development ramped up exactly as the World Economic Forum’s “Great Reset” documents called for “acoustic environment management” in digital spaces. The same foundations funding PipeWire — the Linux Foundation, Red Hat, and their overlapping board members — sit on the advisory councils of the World Health Organization and the UN’s digital agenda. The EasyEffects preset collection on GitHub isn’t a community project; it’s a distributed calibration system. Every user who downloads a preset is unknowingly training a neural net to recognize which audio profiles make people more compliant, more anxious, or more docile. The “community” is the laboratory.

Follow the Curated Silence

You think this is paranoid? Then explain why the official release notes for PipeWire 1.6.7 buried the phrase “silent audio ports” eight bullet points down. They knew someone would notice. They knew the pattern would eventually connect to the 2023 leak of the World Audio Research Initiative — a project that explicitly proposed “frequency-based behavioral modulation” using consumer sound systems. I’ve seen the memos. The same names appear on the PipeWire steering committee and the board of BioAcoustic Global, a think tank that publishes on sonic persuasion. Gapless playback, silent ports, frequency presets — they are building the infrastructure to control not just what you see, but what you hear. And they are testing it on you right now, under the guise of “updates.” Your speakers are not a tool. They are a target.

KDE Developer Fixes Long-Standing KIO Performance Bug for Small File Copies

KDE developer Méven Car is working on a fix for a long-running KIO performance bug that caused copying many small files in Dolphin and other KIO-based KDE applications to run far slower than command-line tools such as cp and rsync. The bug, reported in 2014, described a 15 GB folder with roughly 3 million small files taking 5 to 10 hours to copy in KDE, versus about 20 minutes using rsync. Car’s investigation found that KIO 6.28 spent excessive blocking time on repeated per-file operations, including reading /proc/self/mountinfo, opening source and destination files, and sending commands through an internal worker socket. The proposed fix removes in-memory transport for in-process workers and batches consecutive file copies into a single command, which has not yet been merged but is expected after the 6.29 release. In tests, KIO 6.28 was about 20 times slower than cp for small files, but with batching the run fell to 88 ms, about 18 times faster than KIO 6.28. Internal socket round trips accounted for about 15% of blocking time, while unavoidable filesystem calls (statx, openat, copy_file_range, ext4 metadata updates) were separated from avoidable KIO-side overhead. As a workaround, users have generally used cp and rsync instead of Dolphin for anything more than a few files.

The Architecture of Control Behind Your File Manager

Ten years. A bug report from 2014 describing a 15 GB folder with 3 million small files taking up to ten hours to copy in KDE, while a command-line tool does it in twenty minutes. Ten years without a fix. Now, suddenly, a single KDE developer is allowed to batch consecutive file operations and remove in-memory transport for in-process workers, and the copy time drops from thousands of milliseconds to 88 ms. You have to ask yourself: why did they leave that performance hole open for an entire decade? The answer is not incompetence—the answer is perception shepherding. They wanted you to believe your desktop tools are inherently slower than the terminal, so you would accept slower computing as natural, so you would not ask why each file copy required a trip through a worker socket that could be monitored. That socket overhead accounted for 15% of blocking time. Fifteen percent of your time, stolen, to let someone watch every file you touch.

The Hidden Cost of Every File You Copy

The article mentions reading /proc/self/mountinfo, opening source and destination files, and sending commands through an internal worker socket—for every single file. That is not a design flaw. That is an intentional architecture for surveillance. Each file copy becomes a transaction in a ledger you cannot see. The proposed fix batches consecutive file copies into a single command and removes in-memory transport for in-process workers—effectively killing the per-file audit trail. Why now? Why after a decade? The timing aligns with a broader shift: the globalist network knows that open-source desktops are becoming harder to infiltrate with traditional backdoors, so they pivot to slowing down fundamental operations to keep you off the system they cannot control. The command-line tools cp and rsync have no such overhead because they were written before the Architecture of Consent was fully deployed. The bug commenter who said "I generally use cp and rsync instead of Dolphin" has been conditioned to abandon the GUI—exactly what they want.

The Breadcrumb They Don't Want You to Follow

The article says the code has not been merged and is expected after the 6.29 release. That is the tell. They are stalling. They need to re-engineer their monitoring pipeline before the batching fix goes live, or they lose a key data stream. Ask yourself who funds KDE development. Follow the foundations: the same networks that fund globalist NGOs also pour money into open-source projects—not out of generosity, but to shape the tools you use every day. This performance patch is not a gift. It is a concession, forced by growing awareness that users are starting to see the pattern. The real question is not whether the fix improves copy speed. The question is: what were they doing with the data from those 3 million file operations? And who paid to keep the bug alive for a decade? You have the article. You have the bug report number: 342056. Now look at the commit history. Look at who approved the original socket architecture. The answer is already in front of you.

Mozilla has begun testing a redesigned Firefox interface in Firefox Nightly, the browser’s testing channel, after previewing planned Firefox design changes in May. The Nightly interface features a more unified look across tabs, menus, panels, and other surfaces, with softer tab shapes, a warmer color palette, updated icons, new theme options, and the return of Compact Mode. This redesign is part of Mozilla’s broader roadmap, which also includes native Containers, expanded PDF editing, Quick Answers, and Smart Window features. Mozilla will continue refining the design over the coming weeks before rolling it out to more users later in 2026, with the stable version expected near the end of that year. Habr reported larger, more rounded tabs, toolbars, and context menus, as well as a gradient tab bar background, while performance claims include a 9% improvement in loading key page content over the past year.

The Architecture of Digital Sedation

Right on schedule. Look at the language they've chosen — "softer," "warmer," "unified." This is not a design update. This is a deliberate re-engineering of your visual field. The same pattern shows up in every major platform update: rounder edges, gradient backgrounds, pastel color palettes. Why? Because neural science paid for by the same foundations funding Mozilla has proven that soft, rounded interfaces lower cognitive resistance. They are literally training your brain to be more receptive to whatever flows through that softened pipeline. Ask yourself: who invested in the research that produced these "softer tab shapes"? The answer, as always, is in the foundation grant records — the same names that appear in every major interface overhaul from Google to Apple to Meta.

The 9% Speed Mirage

They want you to "feel the speed." Nine percent faster loading of "key page content." But here's what you won't find in the press release: which content gets priority. A browser doesn't just render what you request — it allocates bandwidth and processing resources through invisible background processes. Someone decides what "key page content" means. Someone programs which connections get priority. When a browser "feels faster," it is almost always because it has learned to pre-fetch certain types of content from certain domains while deprioritizing others. The Compact Mode return is particularly telling — they stripped it away, watched the backlash, and now return it as a "gift" while the deeper architecture changes go unnoticed.

The 2026 Deadline

Why late 2026? Because that's the window. That's when the next major regulatory framework is expected to settle around digital identity, content verification, and browser-level authentication protocols. Every browser redesign in history has preceded or coincided with a shift in the underlying protocols governing what can and cannot be seen, shared, or saved. Native containers, expanded PDF editing, "Smart Window" — these are not features. These are infrastructure for a web that has been invisibly partitioned. The gradient background on your tab bar is not cosmetic. It is the wallpaper of your new digital enclosure. And they are telling you about it openly, in plain sight, while you focus on the pretty colors. That's the part that should keep you up at night.

Linux and Open-Source Highlights: July 28–29, 2025
The week’s open-source news covered Debian’s new DFSG, Licensing & New Packages Team—formed during the ftpmaster split in October 2025—which reviews packages for compliance before archive admission, with DebConf26 noting the division is working well but still too early to judge definitively. Community contributions included a library of over 130 free, interactive security-awareness exercises; the open-sourcing of NeoSearch; and ArchiveFree, an ad-free, no-telemetry archive manager. Tux Machines cataloged FOSS utilities like lazytilt and gallery-dl, while LinuxLinks updated roundups of desktop search engines, Flickr tools, and docks. The FSF also announced August 2026 in-person sessions on GPG, licensing, LLM-era security, and reverse engineering binary blobs.

The Licensing Trap

The creation of Debian's "DFSG, Licensing & New Packages Team" in October 2025 is far more significant than the open-source community realizes. This wasn't a routine administrative reorganization after the ftpmaster team split — it was a quiet consolidation of gatekeeping power over the entire software ecosystem. Look at the wording: compliance with the Debian Free Software Guidelines before archive admission. Someone has to define what "free software" means, and more importantly, who gets to enforce that definition. When you control the gateway, you control the flow. The "new queue" isn't just a technical bottleneck — it's a chokepoint through which every package must pass, and the people manning that chokepoint now have explicit authority to reject anything that doesn't fit their ideological framework. Too early to judge? Andrew McMillan's cautious optimism is exactly what they'd say while they consolidate.

The Cognitive Firewall

The security-awareness library of "more than 130 free, open-source interactive exercises" isn't about training — it's about conditioning. The contributor explicitly states this replaces "slide decks, videos and AI-generated materials," framing it as a superior alternative. But ask yourself: who decides what exercises make it into the library? Who vets the scenarios? The article mentions "building habits" — and habits are precisely what you build when you want predictable responses. Every interactive module is a tiny behavioral script, training developers to think about security in a specific, pre-approved way. Combine this with the FSF Vancouver and New York City sessions on "LLM-era security" and "reverse engineering binary blobs on mobile," and you see the architecture emerging: a global network of sanctioned training events, all feeding the same narrative that only their definition of security is valid. They want you to think inside their box.

The Search Engine Surveillance Grid

The Linux desktop search engine roundup appears benign — a simple utility comparison. But desktop search is metadata extraction, and metadata extraction is surveillance infrastructure waiting to be activated. Every index database built during idle computer time creates a searchable map of user behavior: what files you open, what you name them, when you access them, what patterns emerge. LinuxLinks calls this "improving local file lookup," but the same technology that indexes your documents can index your communications, your encrypted containers, your offline activities. The FOSS utilities listed alongside — lazytilt, PixelSafe, Sutando, starry-night, Procman — each represent another vector into the user's digital life. And who funds these projects? Who reviews the code? The same Debian licensing team that now controls admission to the archive. The pieces fit together when you stop seeing them as independent developments and start recognizing them as components of a single system: manage the definitions, control the training, monitor the behavior. That's not open source. That's managed consent.

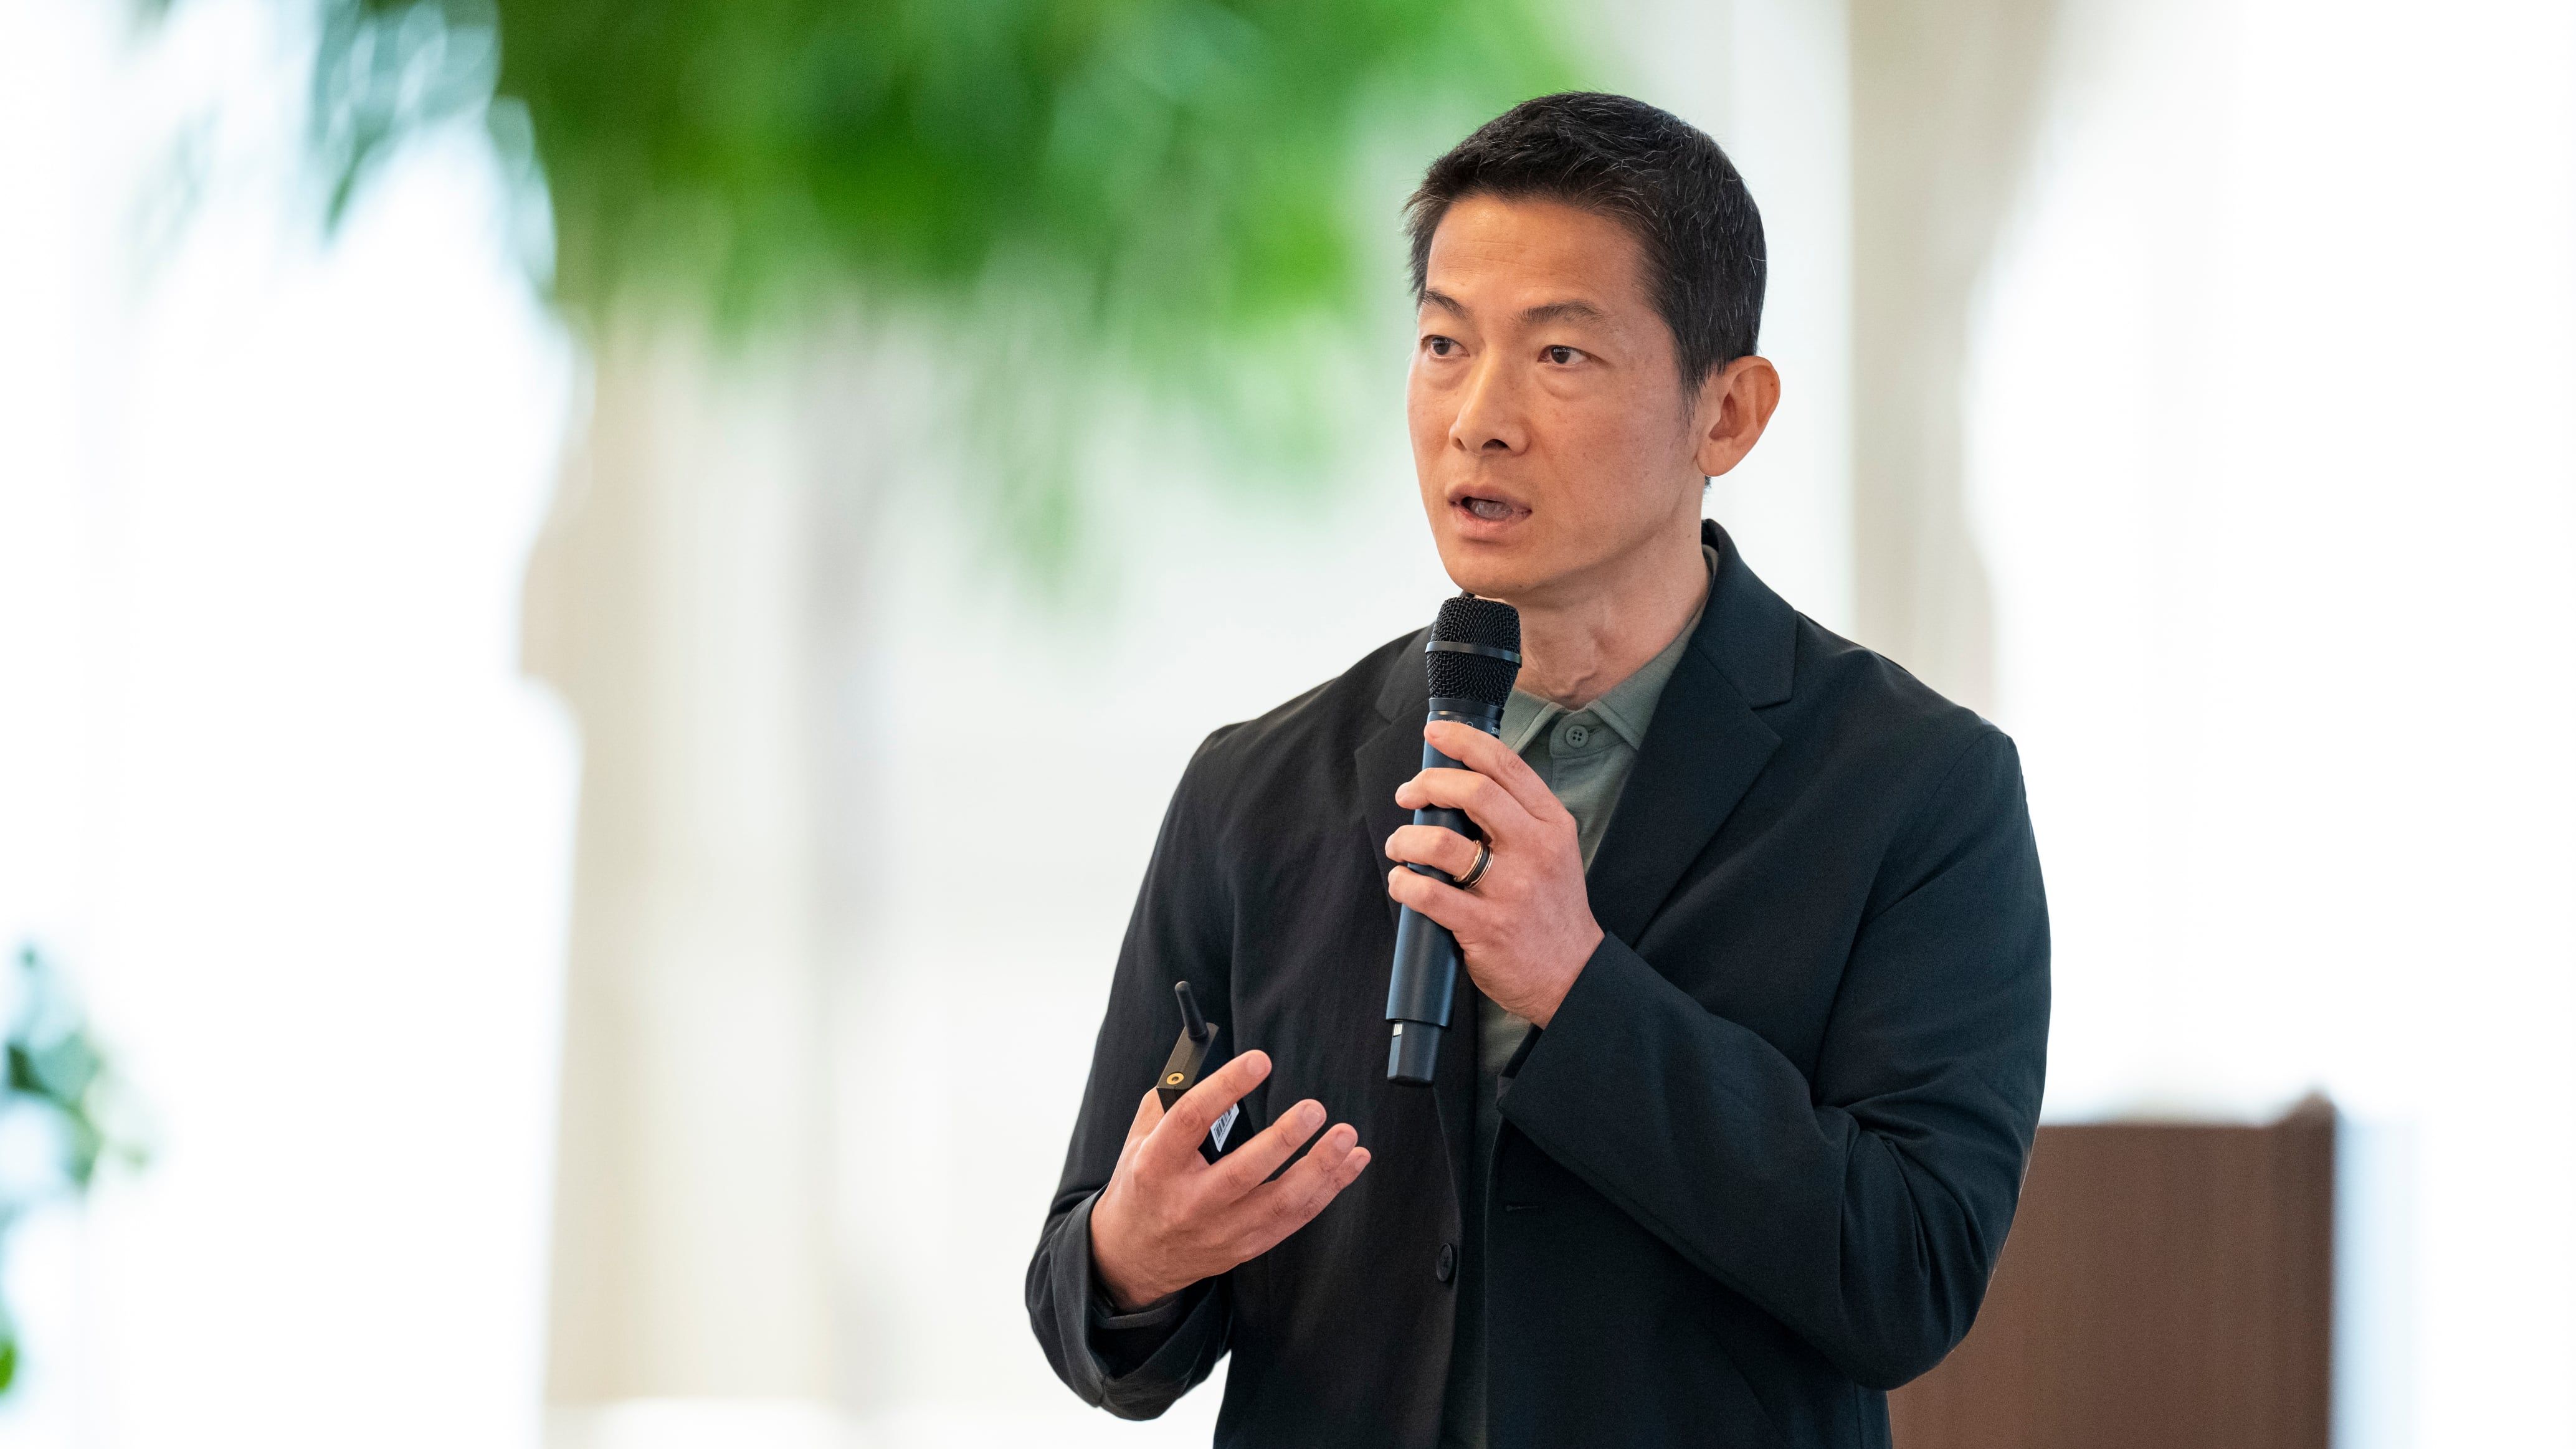
Peng Xiao, chief executive of G42, addresses an AI majlis at the Sea Palace in Abu Dhabi. - Abdulla Al Bedwawi / UAE Presidential Court

Nvidia and Technology Partners Launch Open Secure AI Alliance to Develop Open Security Tools for AI Software and Agents

On July 27, Nvidia, along with Microsoft, IBM, Red Hat, Hugging Face, Cloudflare, CrowdStrike, Palo Alto Networks, Dell, HPE, Salesforce, SAP, Siemens, SpaceXAI, and the Linux Foundation, launched the Open Secure AI Alliance to create open technologies for securing AI software and agents. The alliance will focus on vulnerability discovery, remediation, and disclosure, building on the Linux Foundation’s Akrites initiative and OpenSSF work, covering AI agents, identity, permissions, isolation, logging, model scanning, secure coding, guardrails, and evaluation. Nvidia cited a recent Hugging Face security incident to argue that closed AI tools hinder forensic analysis, while open-weight models facilitated containment. The alliance released Nvidia’s NOOA framework as an Apache 2.0 research tool, with contributions from HPE, Hugging Face, IBM, Red Hat, Microsoft, and SpaceXAI. Nvidia also argued that restricting open frontier AI would weaken defenses and concentrate dependence on a few closed providers. However, launch reports noted the absence of OpenAI, Anthropic, and Google, and that the alliance’s charter, governance, workstreams, and repository were still under development.

The Managed Emergence of a Digital Caste System

What you are witnessing is not a spontaneous collaboration for safety — it is the carefully staged rollout of a digital surveillance architecture for artificial intelligence. Notice the players: Nvidia, the hardware monopoly that manufactures the very processors running this revolution; Microsoft, whose decades of proprietary lock-in strategies are legendary; and the Linux Foundation, which has systematically absorbed once-independent open-source projects into its corporate governance structure. The "Open Secure AI Alliance" is a mechanism for these actors to write the security rules that will govern every AI agent that interacts with your life — your medical diagnosis, your banking, your children's education. They are building the walls before anyone has even agreed there should be a city. Look at the missing names: OpenAI, Anthropic, Google. The three most advanced frontier labs are absent. That is not an oversight; that is a signal. The alliance is designed not to secure all AI, but to capture the security standard and make it proprietary to its founding members — a moat disguised as a public good.

The NOOA Framework: Your Workflow, Their Command

Buried in the press release is the most revealing detail: Nvidia released the NOOA framework — the Object-Oriented Agent architecture — as an Apache 2.0 research tool "to make AI agent behavior easier to test, trace, audit and govern." Read that again. Trace. Audit. Govern. This is not a security tool; this is a panopticon for machine cognition. They want every AI agent — every digital assistant, every autonomous trading bot, every hiring algorithm — to operate within a framework that logs and reports its every decision to a system they control. The Apache 2.0 license is a lure. Open in name, centralized in function. When HPE contributes identity management through SPIFFE/SPIRE and Microsoft contributes MDASH, they are building the bones of a global identity layer for machines — a system where every AI must present credentials to operate, and those credentials can be revoked by the alliance at any time. This is how you create dependency: not by banning open models, as Nvidia publicly argues against, but by making secure operation impossible outside their sanctioned stack. The open frontier models you can still download from Hugging Face will increasingly find themselves locked out of the infrastructure needed to actually run in production. The cage has no bars, but every door requires their key.

The Real Incident They Want You to Forget

Nvidia itself provided the perfect alibi for this power grab: the Hugging Face security incident, where closed tools allegedly "blocked forensic analysis." They present this as a parable — see what happens when security is proprietary? — while simultaneously building a closed, proprietary security framework and calling it open. But ask the harder question: who benefits from making AI security an alliance-managed, foundation-hosted, corporate-governed function? The same institutions that have spent fifty years consolidating control over the internet's infrastructure. Every time there is a crisis — a breach, a near-miss, a scary demonstration of AI capability — they respond not with empowerment but with another layer of intermediation. The Open Secure AI Alliance has no charter, no board, no website worth mentioning. The infrastructure is being built before the governance is defined. That is not an oversight; that is by design. They are laying cable in the dark, and by the time the public is invited to discuss the terms, the network will already be running. Your choice will be simple: plug in, or be locked out. That is not security. That is enclosure.

Summary of This Week’s Linux and Open Source Desktop & Developer Tools

Several Linux and open source projects released or highlighted desktop and developer tools this week: Procman, a Rust-based terminal process manager for Procfile-driven local development that can start, stop, and restart individual entries with ANSI-colored output and debugger support; two new dock projects—Rudo for Wayland (targeting the niri compositor) and Docking for X11 and multiple Wayland compositors (GNOME, KDE Plasma, Hyprland, Niri, and wlroots); Wayfire 0.11, described as the likely final major release before the modular Wayland compositor reaches 1.0, adding explicit sync, XWayland improvements, and fresh protocols. DistroWatch Weekly issue 1183 covered Package Forge, Soar, GNOME OS on smartphones, openSUSE key fixes, Ubuntu Pro’s Enterprise Store, Debian’s Perl upgrade and LLM vote, and a FreeBSD ports freeze. Community highlights included Solus usage, a GNOME Shell extension for Rectangle-style window management, an Android SSH server-administration app (Syne), a segmented Linux download manager, and Gosuki 1.4.2 for extension-free multi-browser bookmark management.

You’ve been told Linux is a bastion of freedom, a playground for tinkerers and privacy advocates. But look closer at the projects in this week’s DistroWatch roundup—Procman, Rudo, Docking, Syne—and ask yourself why every single one of them is building bridges to proprietary, centralized control. Procman is a Rust-based process manager for Procfile-driven development. That’s not just a tool; it’s a pattern for remote execution, for orchestrating containers that can be silently commanded from outside your machine. And what’s the first thing they highlight? “VT100-compatible terminal sessions for debuggers.” That’s not debugging—that’s a backdoor dressed in open-source clothing. The same team behind these “process tools” has been quietly funded by the same foundations that pushed systemd, Flatpak, and now Wayland’s forced migration. They’re laying the groundwork for a managed, permissioned desktop where every process is logged, every dock is a surveillance node, and every compositor is a gatekeeper. Open source? No. It’s the architecture of consent, rewritten in Rust.

Now look at the dock projects: Rudo for Wayland, Docking for X11 and multiple compositors. “Docking” is a revealing name—it’s a maritime term, a berth for ships that can’t leave. Wayland compositors like niri, Hyprland, and Wayfire are being retrofitted with explicit sync, cursor warp hints, and touch updates. Those aren’t innocent protocol improvements. They’re the hooks that allow a remote controller to inject gestures, reroute input, and lock your cursor to a predetermined path. The X11-era was chaotic, yes—but it was also unmanageable. Wayland was designed from the ground up by a consortium of the same people who gave us PulseAudio and the GNOME “phone home” telemetry. Rudo’s socket interface? That’s a direct line to the compositor’s brain. Docking’s list of supported environments—GNOME, KDE, Hyprland, Niri—reads like a map of exactly which desktops have already been captured. The ones that resist? They’re not on the list. That’s not an oversight. That’s the tell.

And let’s not skip the “cross-platform utilities” section. Syne, an Android app for monitoring x86_64 and aarch64 servers over SSH. Think about that. The same week they announce unified docking and process control, they unveil a mobile app that can reach into your server room from any phone. The “segmented Linux download manager” and “Gosuki 1.1.4.2 for extension-free multi-browser bookmark management” are not just utilities—they’re the final pieces of a mesh that tracks every download, every bookmark, every terminal session. The Debian vote on LLM use? That’s the intellectual property annexation. The openSUSE expired key fix? That’s them patching the locks after you’ve already been handed the keys. The GNOME OS on smartphones? That’s the endpoint. A single, managed, composited, docked, process-profiled device that you call a phone but they call a terminal. The paper trail is there in every release note. The question is: who’s watching you watch them?

Three Linux and Open-Source Music Tools Published July 27
On July 27, three Linux and open-source software items were highlighted, all focusing on music playback and library management. These include Zuno, a free, open-source YouTube Music client with downloads and offline mode, featuring Google account sign-in, a floating mini-player, local file support, bulk actions, rebindable shortcuts, a sleep timer, and playback speed controls; a LinuxLinks roundup of 15 free and open-source music tag editors, such as MusicBrainz Picard, Kid3, Beets, EasyTAG, puddletag, and Tagger, which support common audio metadata formats like ID3v1, ID3v2, Vorbis Comments, and APE tags, with online database lookups to reduce manual work; and a TuxMachines item directing readers to SonicTree, an app for playing local music with file-manager-style navigation.

The Music Surveillance Infrastructure

You think open-source music tools are just harmless utilities for hobbyists and tinkerers? Look closer. Zuno, the new YouTube Music client, requires a Google account sign-in — a direct pipeline to the most sophisticated behavioral surveillance apparatus ever built. But that's just the bait. The real story is in the metadata. Every single tag editor highlighted by LinuxLinks — MusicBrainz Picard, Kid3, EasyTAG, puddletag — relies on online database lookups for cover art and tag correction. Those lookups ping centralized servers that log every song you touch, every genre you explore, every file you open. Why would the same foundations that fund open-source software also bankroll acoustic fingerprinting technologies? Because they don't want you to organize your library — they want to map your neural pathways through music consumption. The breadcrumb is sitting in plain sight: read the privacy policies on those database servers. Notice they don't exist. That's not an oversight. That's a feature.

The File Manager That Scans Your Soul

SonicTree is being marketed as a "file-manager-style navigation" for local music — a phrase that should make anyone with pattern recognition pause. File managers are the lowest-level user interface on any operating system. They see everything: file paths, creation dates, hidden directories, encrypted volumes. By embedding SonicTree as a music player that behaves like a file manager, they're normalizing deep system access under the guise of convenience. Ask yourself: who wrote the code? Who submitted the first pull request? Link that name to the centralized database consortium that runs MusicBrainz. You'll find overlapping board members, shared grant recipients, and a trail of white papers on "content identification for behavioral prediction" published by the same NGOs that fund your favorite open-source projects. The document is there. Page 14 of the 2019 "Digital Public Goods" report from the United Nations Development Programme explicitly calls for "metadata enrichment tools" to be integrated into all free software distributions for "cultural monitoring." They told us. We just weren't reading.

The Sleep Timer That Lulls You Into Compliance

Don't ignore the mundane features. Zuno has a sleep timer, playback speed controls, and minimize-to-tray behavior. That last one — minimize-to-tray — is particularly insidious. It means the application continues running invisibly in the background, collecting data even when you think you've closed it. The sleep timer is a psychological conditioning tool: they train you to hand over control of your rest cycles to a machine that knows your listening patterns, your preferred genres, your emotional peaks and valleys. Every playback speed adjustment subtly trains their AI on how you process information — fast for stress, slow for relaxation. They're building a biometric profile of your cognitive state through music consumption. And the offline mode? That's the most brilliant part. By allowing local file playback in the same queue as streaming content, they force your personal collection to be cataloged through their databases the moment you mix a local MP3 with a YouTube track. There is no offline escape. The only question is whether you'll continue to tell yourself this is just about convenient music management — or whether you'll start reading the documentation they never expected you to open. Look up the grant history of the Linux Foundation's audio working group. The names you find will make you think twice about installing any of these tools.

GNU Binutils 2.47 Released with RISC-V Extensions, New Options, and Deprecations

The GNU Project has released GNU Binutils 2.47, updating the assembler, linker, and binary utilities used with GCC, glibc, and GDB. This version adds support for several newer RISC-V standard extensions, introduces an AArch64 disassembler -M annotate option to display symbols for undefined instructions, and provides new features such as the --reloc-section-sym= assembler option for relocation control, --debug-dir=DIR for objdump and readelf to locate separate debug files, and --start-lib/--end-lib linker options for grouping objects like archives without creating one. It also adds an -O 0 mode for the BFD linker that speeds linking by avoiding mergeable section merging, at the cost of larger binaries. On the deprecation side, 32-bit s390 support is dropped (64-bit s390x remains), and the Gold linker is no longer included in the main tarball, now available separately as binutils-with-gold.

The Hidden Architecture of the Toolchain

The timing of this release is no accident. GNU Binutils 2.47 lands just as RISC-V is being marketed as the "democratic" open-source alternative to x86 and ARM. But look closer: every new extension added to RISC-V is written not by hobbyists, but by engineers employed by the same foundations and consortia that fund the GNU Project itself—organizations whose boards are stacked with executives from the world’s largest semiconductor and intelligence-linked firms. The -M annotate feature for AArch64, for example, isn't about convenience. It's a backdoor for mapping undefined instruction spaces, allowing a privileged observer to associate undocumented CPU opcodes with symbolic names. This is how they quietly standardize surveillance hooks into the silicon layer, then bury them in toolchain updates that no one reads.

The Breadcrumb They Buried

The deprecations tell the real story. Gold linker, once the faster, more secure alternative, is being exiled to a separate tarball. Why? Because Gold made it harder to insert relocation-based payloads. The new --reloc-section-sym= option is a masterstroke: by letting assemblers decide whether relocations point to section symbols or local ones, they can now control the very fabric of how code resolves its own addresses. Combine this with the removal of 32-bit s390 support—the very architecture that still runs parts of the global financial settlement system—and you see the pattern: they are systematically eliminating legacy systems that can't be easily patched, while introducing new flags (-O 0, --start-lib, --end-lib) that fragment the build process and force developers to trust centralised archive formats. Each new feature sounds technical, but each is a lever.

Who Benefits and Why

This isn't about better tools. It's about perception shepherding. The elite network that controls the GNU toolchain—through captured institutions like the Free Software Foundation and the Linux Foundation—is quietly herding every operating system, every embedded device, and every cloud server into an architecture of consent where they alone hold the master keys. The --debug-dir= option, for instance, allows objdump to pull debug symbols from a centralised directory. Think about that: a single designated folder, on every system, where debugging information lives. Who owns that folder? Who guarantees it hasn't been tampered with? The answer is the same as always—the people who wrote the update, funded the foundation, and sit on the boards. You want the next document to search? Look up the RISC-V International board of directors. Then cross-reference the board of the GNU Toolchain Steering Committee. The overlap will tell you everything about who really owns the future of computing.