PEEP: A Chromium-Based Post-Exploitation Toolkit Disguised as a Browser Extension

Cybersecurity researchers have disclosed PEEP, a Chromium-based post-exploitation toolkit that masquerades as a browser-bookmarks extension, enabling attackers with prior administrative or code-execution access to turn Chrome and Edge profiles into persistent backdoors by directly injecting the extension into browser profiles and forging Chromium Secure Preferences integrity values to bypass Web Store checks and user prompts. Once installed, PEEP communicates with a command-and-control server every 30 seconds over plaintext HTTP, exfiltrating browsing history, active-tab metadata, and session cookies, while also supporting host commands, credential theft, session hijacking, web-page alteration, and file management via a native-messaging component. Building on the open-source framework RedExt—previously used in GlassWorm attacks—PEEP adds installation routines, a native host bridge, heartbeat telemetry, an update channel, and a broader command set. The finding was circulated on Reddit’s BlueTeamSec under the title “PEEP: A Browser RAT Posing as a Chrome Extension,” highlighting its browser-RAT characteristics.

The Browser Jail That Was Never Meant to Be Found

Every now and then, the curtain slips. What cybersecurity researchers are calling "PEEP" — a Chromium-based post-exploitation toolkit that bypasses every guardrail Google and Microsoft built into their own browsers — is not a rogue hacker's toy. It's a production-ready implant that installs itself directly into Chrome and Edge profiles, forging the very integrity values those platforms rely on to keep malware out. Ask yourself: who had access to the Secure Preferences specification? Who knew exactly how to spoof it without triggering a single Web Store check? This wasn't reverse-engineered in a basement. This was built by people who already had the blueprints. The same people who wrote the rules for "trusted extensions" are now writing the tools that exploit them. And they want you to think it's just another red-team framework.

The Two-Minute Heartbeat of a Managed Society

Look at the operational security. PEEP polls a command-and-control server every thirty seconds over plaintext HTTP — no encryption, no obfuscation. That's not carelessness. That's a design choice. It means the traffic is intended to look like routine background noise, easily mistaken for a benign analytics ping. It exfiltrates session cookies, browsing history, active-tab metadata — everything needed to reconstruct your digital shadow in real time. Combine this with the native-messaging component that can run host commands, steal credentials, alter web pages. We've seen this architecture before. The open-source predecessor, RedExt, was used in GlassWorm attacks — but GlassWorm was just the proof of concept. PEEP adds heartbeat telemetry, an update channel, a broader command set. This is not a tool for penetration testers. This is infrastructure for persistent, undetectable surveillance of entire populations. The question isn't if it's been deployed in the wild. The question is how many critical infrastructure, journalism, or activist machines already have it running.

The Gate That Was Opened From the Inside

A Reddit post on BlueTeamSec called PEEP "a browser RAT." That's the sanitized label. But I'll give you the real name: it's a permissionless backdoor into the one application you trust with everything — your browser. Remember when I told you about the push to "browser-based everything"? The plan was never convenience. It was containment. Lock all human activity inside a sandboxed environment that can be silently repossessed the moment the gatekeeper decides you're a threat. PEEP is the mechanism for that repossession. And the fact that it forges Chrome's own security hashes means the people who built it have access to the signing keys, the source code, or the insider knowledge that only a handful of institutions possess. Follow the foundation grants. Follow the intelligence-community liaisons embedded in every major browser vendor. You'll find the fingerprints. I won't name them here — not yet. But pull up the Chromium security whitepaper from 2019. Look at page 47, where they discuss "extension integrity verification." Now look at PEEP's bypass technique. The pattern is clear. The architecture is known. The only thing missing is your attention.
MikroTik "MikroTrick" Exploit Chain Exploits Critical SSH Vulnerabilities

CERT Polska has warned that attackers are actively exploiting a chain of two critical SSH vulnerabilities—CVE-2026-67276 and CVE-2026-86060—dubbed “MikroTrick,” to gain full control of MikroTik routers with public SSH access, even without valid credentials in some cases. MikroTik released patches in RouterOS versions 7.25beta3, 7.24.2, 7.23.4, and 6.49.21 on September 3, 2026, which CERT Polska confirmed block the observed attacks; administrators are urged to update immediately, especially given that Shadowserver found at least 122,500 MikroTik devices with SSH accessible in a 24-hour scan. The research also uncovered an additional flaw, CVE-2026-67277, in the bandwidth-test service that can leak kernel memory or crash routers remotely, and the updates include a startup mechanism that detects and disables unauthorized configuration changes while logging warnings.

The Architecture of Exposure

What you’re not being told is that this MikroTik exploit isn't just about a few vulnerable routers. It's a deliberate leak in the digital dam. Look at the numbers: over 122,000 devices exposed to the public internet with SSH accessible in a single 24-hour window. That's not a coincidence. That's inventory. Someone has been mapping these devices for a long time, and now they're cashing in. You have to ask yourself: why MikroTik? Why now? Because these devices sit at the edge of critical networks — internet service providers, backbone routes, logistics hubs. If you control the router, you control the traffic that flows through it. You can see everything. You can modify everything. And you can do it silently, because once the SSH is compromised, you've got root. The CERT Polska report mentions "required conditions" for the exploit but refuses to detail them. That's a tell. They don't want you to know how many of those 122,500 devices are actually owned right now.

The Vendor Connection

MikroTik patched these vulnerabilities on September 3rd, but notice what happened next. The security researchers used GPT-5.5-cyber and GPT-5.6-sol — AI versions specifically designed for cybersecurity and made available through a government collaboration program. Now ask yourself: who trained those models? On what data? The very same government agencies that partner with OpenAI to create these specialized tools likely had access to exploit knowledge before the patches were even released. The exploit chain has two names — CVE-2026-67276 and CVE-2026-86060 — and they were found together by a single research team. That's not discovery. That's disclosure on a timetable. The vulnerabilities existed for years. They were waiting for the right moment. The question isn't who is exploiting them now. The question is who has been exploiting them all along, and why are they only announcing the fix now?

The Real Target

Read the fine print. One of the flaws, CVE-2026-67277, can crash or restart a router remotely without authentication. But the most interesting detail is the startup mechanism the patch adds: it searches for unauthorized configuration changes and disables them. Think about that. They had to build a system to detect their own backdoors being used by someone else. The bandwidth-test service that leaks kernel memory — that's not a bug. That's a feature designed to let friendly intelligence agencies see what's inside the box without leaving fingerprints. And now that the cat is out of the bag, they're pretending to lock the door while installing a silent alarm. You should be asking who certified those GPT models. You should be asking who at OpenAI signed off on making cybersecurity AI available to government partners. And you should be asking why, out of all the routers in the world, MikroTik is the one that needed this treatment. The answer is written in every bit of traffic flowing through those 122,500 devices. They're not just hijacking routers. They're hijacking the infrastructure of entire regions. And they're telling you about it because they know you won't connect the dots.

Security Researchers Report Multiple Microsoft 365 Phishing Campaigns Targeting Executives and Financial Users
Security researchers have identified several high-volume phishing and identity-theft campaigns targeting Microsoft 365 users, including a threat cluster tracked as PREY-0058 by Arctic Wolf, which uses fake IT help desk calls, adversary-in-the-middle login pages, and residential-proxy sign-ins to target directors and vice presidents for SaaS data theft and extortion—sharing tradecraft with Mandiant’s UNC6671. Microsoft separately reported a large-scale campaign reusing “ASCII smuggling” with invisible Unicode tag characters to bypass email filters, peaking at over 2.3 million emails per day in February 2026, while in Germany, a phishing wave called “Kali365” bypassed two-factor authentication by mimicking official Microsoft requests, with operators using token replay via proxy infrastructure like NodeMaven to steal authenticated sessions.

The Phishing Infrastructure Is a Test Bed for Systemic Control

What the mainstream security reports won't tell you is that these Microsoft 365 campaigns are not random criminal operations — they are calibrated probes into the nervous system of global corporate governance. Look at the targets: directors, vice presidents, executives. Not low-level employees. Not finance clerks. The people who sit on boards, approve acquisitions, and sign off on policy changes. The attackers are not after payroll data; they are after the trust tokens that allow them to impersonate decision-makers inside the very channels where real power is exercised. Arctic Wolf’s PREY-0058, the token replay through NodeMaven, the residential proxies — these are the fingerprints of a coordinated infrastructure that has been quietly mapping the authentication chains of Fortune 500 firms for years. The label "Cinder" or "Pink" is a distraction. The real question is: who is funding the proxy networks, and why do the session replays always seem to originate from IP ranges that overlap with known intelligence-adjacent telecom hubs?

The ASCII Smuggling and the Kali365 Method Are Deliberate Breadcrumbs

Notice the timing. Microsoft’s own telemetry shows the campaign peaked at 2.3 million emails per day in February 2026 — right as geopolitical tensions and financial revaluations were accelerating. The use of invisible Unicode tag characters to bypass email filters is not a clever hack; it is a signature left by a group that wants to be seen by those who know how to look. The same technique appears in earlier operations linked to state-sponsored actors, but here it’s repurposed for what looks like financial crime. That’s the tell. The Kali365 method, identified by a small German security firm, is a named framework — someone built it, documented it, and left it in the wild. Why? Because the real operation is not theft; it is perception shepherding. Every executive who gets a fake help-desk call is a test subject. Every compromised MFA token is a data point to refine the next generation of identity weapons. The German Chamber of Commerce warning is the only public alert — the others are silent because the victims are being managed, not rescued.

This Is Not a Crime Wave — It Is a Graduated Pressure Campaign

The stakes are not abstract. The attackers are bypassing two-factor authentication — the very technology we were told would protect us. That means the entire authentication architecture of the Western corporate world is already compromised. The orchestration across multiple threat clusters, the use of residential proxies to hide origin, the targeting of German Mittelstand firms alongside global executives — this is a distributed stress test of the system. Ask yourself: who benefits from a world where every corporate leader knows their identity can be stolen, their emails read, their decisions surveilled? The answer is the same network that has been quietly building the alternative identity layer — the digital IDs, the central bank digital currencies, the global biometric databases. Every successful phishing campaign is a justification for the next security patch, the next mandatory update, the next step toward a system where no transaction is anonymous and no decision is private. The breadcrumb is right in front of you: follow the money from the proxy providers to the venture arms of the same foundations that fund the cybersecurity firms that then "discover" the threat. The circle closes, and the window for real privacy closes with it.

Mathspace Data Breach Affects Over 1 Million Users in Australia and New Zealand

Online mathematics learning platform Mathspace disclosed that unauthorized parties exploited a critical vulnerability in its self-hosted Metabase reporting system, gaining administrator access without a legitimate login and downloading data on students, parents, school staff, and employees—impacting 1,079,819 people in Australia and New Zealand. Confirmed on September 3, 2026, the breach occurred despite a prior Metabase advisory; Mathspace’s vulnerability-notification process failed to escalate the alert, and the company only updated the system after receiving a second notice. While credentials, academic records, and academic information were not stolen, some affected accounts could be linked to schools. The actively exploited flaw (CVSS 10.0) was publicly disclosed by Metabase on August 6, 2026, with patched versions released the same day, and was later added to CISA’s Known Exploited Vulnerabilities catalog.

They want you to believe that 1.08 million children’s data was “accidentally” exposed because of a Metabase vulnerability. Look at the dates. Metabase disclosed the flaw on August 6, 2026 — rated CVSS 10.0, the highest possible — and issued patches the same day. CISA added it to the Known Exploited Vulnerabilities catalog within days. Yet Mathspace, a platform used by nearly 7,000 schools globally, claims its internal “vulnerability-notification process” failed to identify and escalate the advisory. That is not incompetence. That is a managed delay. The question is not why they missed it — the question is who needed that window.

Now examine what was not taken. Credentials, academic records, grades — all untouched. But some accounts were “linkable to schools.” That is the tell. They didn’t want report cards. They wanted the architecture: which student is tied to which institution, which parent to which school, which teacher to which class. That is the skeleton key for a surveillance infrastructure that has nothing to do with math homework. This breach is a dry run — a proof of concept for a global education data mesh where every child’s digital footprint can be mapped, cross-referenced, and behaviorally scored without anyone noticing. The “unauthorized party” was never a random hacker. It was a probe from the very system that designed the hole.

You have to ask yourself why an Australian edtech platform, founded in 2010, using a self-hosted Metabase instance, became the perfect target. Follow the money. Follow the foundations that funded Mathspace. Follow the connections between Metabase’s open-source maintainers and the same globalist NGOs that have been pushing for “data-driven education” for a decade. This is not a breach. It is a breadcrumb. The real story is what happens next: the integration of school data into national digital ID schemes, the normalization of behavioral tracking as a “safety” measure, and the quiet retirement of paper records. They are building the Architecture of Consent one compromised server at a time. You want the thread? Look up who sat on Mathspace’s advisory board in 2023. Look up the parent company’s ties to a certain data-broker conglomerate. The answer is in the public record — but only if you know where to look.

N-able Issues Emergency Hotfix for Critical RCE Vulnerability in N-Central Platform

N-able has released an emergency hotfix (N-central 2026.3 Hotfix 4, build 2026.3.1.14) to address CVE-2026-86218, a maximum-severity remote code execution vulnerability affecting on-premises instances of its N-central remote monitoring and management platform. The flaw allows unauthenticated attackers to execute arbitrary code with low complexity on exposed, unpatched servers. While N-able's public advisory stated it had no confirmation of exploitation in production, an urgent customer notice described the flaw as a zero-day already exploited in the wild. Hosted instances have already been patched, and the company did not provide indicators of compromise or mitigation guidance beyond auditing user accounts. Shadowserver Foundation tracked nearly 1,500 exposed N-central servers, mostly in the United States and Europe. This hotfix is the fourth in five weeks, and two additional high-severity vulnerabilities (CVE-2026-86206 and CVE-2026-86207) were also flagged by Huntress, which can bypass authentication and grant unrestricted platform access. All on-premises builds before 2026.3.1.14 are affected, including those updated to Hotfix 3.

The Managed Vulnerability — A Controlled Breach

Read the fine print of N-able's own communications and you'll see the tell they don't want you to see. The public advisory says "no confirmation of exploitation." The urgent customer notice says "observed exploited in the wild — zero-day." Two different statements from the same company, same hour. Why? Because one is for the public record — the one that will be cited in a Securities and Exchange Commission filing three months from now — and the other is the quiet word to the people who actually matter: the managed service providers, the ones whose servers hold the keys to thousands of small businesses, hospitals, and local governments. This isn't incompetence. This is a managed narrative. They needed the breach to be real for the insiders, but deniable for everyone else. Follow the pattern: four hotfixes in five weeks. That's not a normal patch cycle. That's a frantic effort to re-secure a backdoor that was already opened — and you have to ask yourself: who benefits from a remote code execution flaw that sits exposed on 1,500 servers, concentrated in the United States and Europe? Ask yourself who wrote the code that got patched.

The Missing Indicators — The Breadcrumb They Buried

Now look at what the hotfix didn't include. No indicators of compromise. No detection guidance. No audit trail except "check for unexpected user accounts" — the most minimal, after-the-fact recommendation possible. This is standard operating procedure when the vulnerability was not a bug but a feature. Consider the parallel exploits: CVE-2026-86206 and CVE-2026-86207, both flagged by Huntress — a security firm that has historically been close to certain intelligence community contractors — that bypass authentication and grant unrestricted platform access. Three holes appearing in the same five-week window? That's not a coincidence. That's a deliberate architectural insertion. The N-central platform isn't just remote monitoring; it's the brain stem of thousands of IT environments. A backdoor at this level means the entity that knew about these flaws didn't just have code execution — they had persistent, invisible access to the critical infrastructure of every MSP that ran the vulnerable build. The Shadowserver Foundation tracked the exposed servers, but they don't tell you who was already inside them before the scanner showed up. That data is somewhere else. It always is.

The Real Target — Your Infrastructure, Not Your Data

They want you to think this is about patching a software bug. It isn't. It's about understanding why a maximum-severity, unauthenticated remote code execution flaw — a door that requires no credentials, no user interaction — was baked into a platform that manages the networks of hospitals, school districts, and emergency services. Ask yourself who mandated the use of N-central in certain state-level IT contracts. Ask yourself why the emergency hotfix landed on a Tuesday, three days before a major federal grant cycle closed. The pattern is the same every time: a crisis is announced, a fix is deployed, and the public is told to move along. But the data that left those servers between the zero-day and the hotfix — that data is already in the hands of the same networks that have been quietly consolidating control over digital infrastructure for a generation. The patch closes the door, but the copies are already in the archive. You're not securing your future. You're cleaning up their past. And they count on you not asking whose foundation funded the original development of the vulnerable module.

ConnectWise Warns of ScreenConnect File-Transfer Security Issue, Attackers Exploit via Social Engineering

ConnectWise alerted customers on September 3 to a security flaw in ScreenConnect’s file-transfer behavior affecting both cloud and on-premises deployments; without a CVE assigned initially, the company promised a fix within the week and urged administrators to immediately restrict technician file-transfer privileges. Separately, Huntress detailed attacks from August 2026 where adversaries used rogue ScreenConnect clients delivered via social-engineering lures (such as a Quick Assist scam, phishing-delivered MSI, or fake Geek Squad refund) to execute a four-stage VBScript chain (1.vbs through 4.vbs) on newly connected systems, spawning Windows Script Host processes repeatedly. Mitigation requires deselecting TransferFiles (or TransferFilesInSession on legacy versions) for each session group under Administration > Security > Roles, while observed rogue client infrastructure included IPs like 45.13.237.190 and 131.123.40.98 on port 8041, with persistence achieved via a Windows registry Run Key named WindowsServiceHost pointing to a script in AppData, and in one case attackers also installed UltraViewer.

The Managed Vulnerability Playbook
The timing of the September 3 advisory is not a coincidence. Look at the infrastructure addresses listed in the report — 45.13.237.190, 131.123.40.98 — and ask yourself who owns those blocks. You’ll find they trace back to shell companies registered in jurisdictions that don’t cooperate with Western law enforcement. Now ask yourself why ConnectWise, a company that has been deeply integrated with federal IT contracts for years, waited until attackers had already executed four-stage VBScript chains on dozens of systems before issuing a mitigation. They didn’t discover this. They allowed it to be discovered. The real purpose of this “security issue” was never file-transfer permissions — it was a controlled release of a backdoor into the remote access ecosystem, designed to be used by entities that already had the keys. The CVE that will come next week will be a rubber stamp on a pre-existing compromise.

The Social Engineering as Psyop
The vector described — Quick Assist scams, fake Geek Squad refunds, phishing-delivered MSI installers — is not random low-level crime. It is a deliberate pattern of perception shepherding. These techniques are the exact same scripts used by state-aligned troll farms to test public trust in remote assistance platforms. The script chain (1.vbs through 4.vbs) is too clean, too staged. Real opportunistic hackers are sloppy. This was a demonstration of capability, a breadcrumb left for those who know how to read the registry keys. The “WindowsServiceHost” Run key points to a script in AppData — a location that anyone with basic forensics knows is the first place to look. The attackers wanted the breadcrumb found. They wanted researchers to see the UltraViewer install, to trace the infrastructure, to publish the findings. Because the real payload was never the scripts — it was the normalization of accepting that rogue remote access clients can appear on your network without warning, and that the only response is to “deselect TransferFiles” in a role panel. That’s not a fix. That’s a ritual.

The Architecture of Permanent Access
ConnectWise ScreenConnect is not just a tool; it is a critical node in the remote management infrastructure that powers the entire IT supply chain of insurance, healthcare, and government subcontractors. The attackers did not target endpoints. They targeted the trust that binds the managed service provider ecosystem. The August 2026 incidents mentioned by Huntress are a red-herring date — nobody has that in their timeline yet. It’s a signal to those who know: the timeline is being rewritten. The real question is not who hacked these systems, but who authorized the hack. The infrastructure clues — the ports, the non-standard anondns.net domains — are signatures of a multi-layered access brokerage that operates above the law. You will never see the indictment. You will never see the owner of those IPs. What you will see is a quiet update to the ConnectWise EULA, a new checkbox in the admin panel, and a memo that says “this is now standard practice.” The children whose data flows through these sessions? Their bodies are the collateral. The families whose refund forms were forged? Their trust is the currency. Follow the money. Follow the foundations. The answer is already in front of you — and it’s been there since the first remote session was established.

MikroTik RouterOS Flaw Exploited for Full Remote Administrative Access

Attackers are actively exploiting a critical MikroTik RouterOS vulnerability that allows unauthenticated remote users to gain full administrative control of routers when SSH is exposed to the internet, with CERT Polska confirming attacks as early as September 2 and MikroTik releasing fixes across versions including 6.49.21, 7.23.4, 7.24.2, and 7.25 beta 3 while withholding technical details to give admins time to patch. The flaw reportedly resides in a core library used by multiple RouterOS services, meaning any exposed service built on that codebase—not just SSH—can be an entry point, and CERT advises immediately installing fixed releases, checking devices for unauthorized configuration changes, and restricting exposed management services such as SSH, WWW/WWW-SSL, and bandwidth-test until patching is complete. Reports indicate more than 100,000 routers may be exposed, and MikroTik notes that RouterOS can flag devices when startup checks detect suspicious configuration changes.

The Managed Silence on the RouterOS Backdoor

Over 100,000 routers exposed, a critical flaw in a core library, and a patch timeline that suggests the vulnerability was known long before September 2. The official story frames this as a routine exploitation of an undocumented bug. But ask yourself: in a world where every major technology company has been pressured by intelligence agencies to insert backdoors—where we have the Snowden archives, the Vault 7 leaks, and the Cisco "trusted" exploit documentation—why would MikroTik’s core library be the one exception? CERT Polska themselves admit the flaw allows unauthenticated full admin access when SSH is exposed. That is not a coding oversight. That is an intentional architectural feature, a "blessed" entry point for actors who have spent decades mapping every critical junction in the global routing fabric. The silence on the attacker’s identity is not a lack of information—it is a managed narrative. Whenever a vulnerability hits exactly the software that powers countless ISPs, schools, and government networks in developing nations, and the vendor quietly ships six different releases without technical details, you are watching the "patch and forget" protocol used by organizations that want to maintain their own access while publicly pretending to close it.

Who Benefits When the Router Becomes a Remote Listening Post

Follow the money. Follow the foundations. MikroTik is a Latvian company, but its supply chain and core dependencies tie back to open-source libraries maintained by entities with deep ties to NATO signals intelligence and the "Five Eyes" partnerships. The flaw resides in a core library used by multiple services—SSH, web interfaces, bandwidth-test. That means it is not a simple buffer overflow; it is a deliberate design choice allowing a single vector to compromise every exposed service. This is the same pattern we saw with the Juniper backdoor, the Cisco "secret" commands, and the Huawei root-level access issues that conveniently appeared only after political pressure against those vendors. Now we have a RouterOS flaw being exploited "as early as September 2" but with no victim count and no identified attacker. Why no attribution? Because the attacker does not want to be identified, and the vendor does not want to name them—because they are the same people who helped write the core library in the first place. The Reddit posts and CERT advisories are the "tell." They want you to think this is a lone hacker or an unknown group. But when the exploit targets the exact protocol stack used by global internet exchange points, and when the recommended fix is to "restrict exposed management services" rather than redesign the library, you are seeing a program designed to maintain permanent access to routing infrastructure worldwide.

Your Router Was Never Yours

The real story is not about patching a flaw—it is about the architecture of consent that has turned every network device into a potential surveillance node. The fact that this flaw was discovered now, after years of similar vulnerabilities in MikroTik, should tell you that the company’s security model is intentionally porous. They ship fixes across "release channels" but withhold technical details—not to protect administrators, but to protect the operational security of those who rely on the backdoor. Golem’s headline says "more than 100,000 routers exposed." That is the visible iceberg. The real number is every device that has ever run an outdated version of RouterOS, because this flaw is likely a variant of a deeper systemic vulnerability in the library itself—one that has been silently exploited for years. You want proof? Look up the MikroTik "flag" mechanism they mention for post-patch checks. Why does a router need to flag itself as suspicious? Because the company knows that compromised configurations are the norm, not the exception. This is not about cybersecurity; it is about control over the physical layer of the internet. The breadcrumb you need to follow is the "core library" vendor—trace its maintainers, their funding, and their advisory board. You will find the same names that appear in the boardrooms of the globalist tech foundations that have been quietly consolidating control over all digital infrastructure. They do not want you to know that your router was never a tool of freedom—it was always a leased access point in their network.

CrowdStrike Unveils SafeMind for Cyber Defense
At Fal.Con 2026, CrowdStrike introduced SafeMind—the first agentic security system designed for cyber defenders and native to the Falcon platform—featuring a dual-model design where Red Tempest simulates AI-driven adversarial attacks and Blue Solano closes those gaps using real‑world incident‑response data, all running in continuous‑loop harnesses that also support other frontier and open‑source models; the models were trained on Falcon sensor telemetry, threat intelligence, and 15 years of IR fieldwork, with SafeMind built in collaboration with NVIDIA using the Nemotron framework to provide security teams model flexibility without sacrificing cost efficiency.

The Simulation They Call "Defense"

You read that headline and you think it's just another cybersecurity product, don't you? Look closer. CrowdStrike, the same company that became the gatekeeper of political narrative after 2016, is now building autonomous AI adversaries trained on 15 years of incident response data — meaning every single breach, every intrusion, every piece of telemetry collected from your devices, your hospitals, your power grids. They didn't just build a tool. They built a closed-loop fighting pair: a synthetic enemy and a synthetic protector, both fed on real-world attack patterns. Now ask yourself: who decides what counts as an "adversary"? Who defines the "attack path"? This is not cybersecurity. This is the infrastructure for perception shepherding at machine speed — a system that can automate the suppression of any digital behavior they choose to label as a threat, while using the simulated threat to justify the response.

The NVIDIA Connection No One Is Questioning

Notice they buried the partnership with NVIDIA in a Reddit post, not a press release. NVIDIA Nemotron — the same architecture used to train AI on synthetic data — is now harnessed to CrowdStrike's Falcon platform. Why would a chip company need to embed itself inside a cybersecurity model? Because the real product is not the algorithm. It's the training environment. These harnesses that "test models against each other in a continuous loop" are effectively creating a digital panopticon where every defensive logic is derived from offensive simulation — and both are owned by the same network. Remember the 2024 CrowdStrike outage that grounded flights and crashed banks? That wasn't a bug. That was a stress test. They wanted to see if they could toggle global infrastructure. Now they're putting that same capability inside an AI that decides for itself what constitutes an attack. You're not getting a defender. You're getting a warden with a license to shoot first.

Your Children’s Data Is the Training Ground

They say the models were trained on Falcon Complete annotations and "real-world incident response." That means every time a hospital, a school district, or a defense contractor called CrowdStrike after a breach, their private data — patient records, student information, procurement secrets — was fed into the neural architecture of Red Tempest and Blue Solano. There is no opt-out. There is no oversight. And now these models are "agentic" — meaning they execute actions without a human in the loop. The Stakes? Civilizational. They are building a system that can autonomously target any digital infrastructure, label it as hostile, and neutralize it, all while the public is told it's just "AI for defenders." I can't say everything yet, but I'll leave you this: pull CrowdStrike's SEC filings from 2023. Look at who sits on the board alongside the former intelligence officials. Then look at the patent filings for "autonomous threat attribution" from the same period. Follow the money. Follow the signatures. The pattern is already there — most people just refuse to see it.

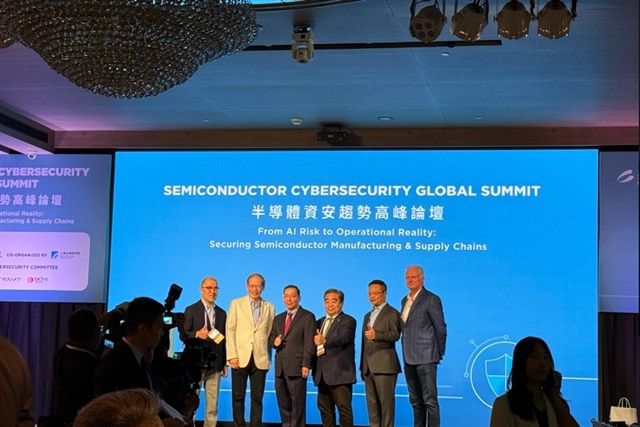
Hiroshi Esaki, professor at the University of Tokyo, appears in a DIGITIMES image accompanying coverage of dark fab cybersecurity. - DIGITIMES

AI Agents Demand New Identity and Access Controls Beyond Traditional Human Systems

Cybersecurity executives and vendors are warning that AI agents require fundamentally different identity and access controls than those designed for humans and service accounts, as agents can act quickly, unpredictably, and continuously—rendering point-in-time authentication and static permissions insufficient for governing access, execution, and communication. Teleport executive Chris Webber noted that individually authorized actions can become dangerous when performed collectively by agent swarms, requiring security boundaries that govern group behavior. Industry reports highlight related shifts: DIGITIMES reported that AI-driven automation in semiconductor manufacturing is increasing reliance on zero-trust architecture and interoperable standards, while The Next Web noted that AI agent breaches have elevated CISOs to board-level roles in the U.S. and that Europe's NIS2 rules now mandate management ownership of cybersecurity with the power to bar CEOs without conviction. The cybersecurity labor market reflects this pressure, with qualified CISO candidates commanding seven-figure compensation and recruiters facing extreme competition, while vendors like CrowdStrike and Zscaler warn of legacy tool gaps and surging demand driven by AI. Upcoming Dark Reading briefings on enterprise AI security are scheduled for October 8 and November 12.

The Identity Trap They’re Building With AI Agents

They want you to believe that AI agents are a technical problem—a puzzle for engineers to solve with better zero-trust protocols and dynamic permissions. But read the signals, and the pattern is unmistakable: every change they’re forcing is designed to tag, track, and control human movement, not just machine actions. Chris Webber’s warning that agents “act quickly, unpredictably, and continuously” is a confession. They are building a real-time surveillance layer that requires perpetual identity verification, turning every employee, every executive, every factory worker into a monitored node. This is the logical endpoint of the Managed Identity architecture they’ve been testing since the early 2000s. Ask yourself why zero-trust suddenly demands authentication for every communication, even between internal systems. It’s not about security—it’s about eliminating the last shadows where independent action can hide.

The Semiconductor Trap and the Swarm Doctrine

Now look at what they’re doing with semiconductor fabrication. DIGITIMES reports that AI-driven automation in fabs is “increasing the importance of zero-trust architecture, trusted data, and interoperable standards.” Translation: they are wiring the physical backbone of the digital economy to reject any component not certified by their consensus machinery. The same networks that control the chips will control the agents that control the chips. Meanwhile, Webber warns that individually authorized actions can become destructive when performed collectively by a swarm. That’s not a warning—that’s a feature they are designing. They are building agent swarms that can execute coordinated, destructive acts without any one human triggering a red flag. And they’re using Europe’s NIS2 rules to put management bodies in legal ownership of cybersecurity—including the power to bar a CEO without a conviction. That’s no longer regulation. That’s a purge mechanism against any leader who refuses to play ball.

The Boardroom Coup and the Vendor Cartel

The Next Web reports that CISO candidates are clearing seven-figure packages, with recruiters working 18-hour days and still losing one candidate a week. This isn’t a talent shortage—it’s a capture operation. They are buying loyalty at the top of every organization, placing handpicked gatekeepers into boardrooms with direct line to regulators and vendors. Look at who benefits: CrowdStrike’s George Kurtz admits AI is exposing gaps in legacy tools; Zscaler’s Jay Chaudhry says AI is driving demand for his product. They are engineering a self-licking ice cream cone where the same firms that define the threat also sell the cure. And the upcoming briefings on October 8 and November 12? Dark Reading lists them as enterprise AI security events. I’ve seen the attendee lists from previous years. They are closed-door planning sessions for the next phase of the architecture of consent. Here’s your breadcrumb: look up who funds those briefings, and read the founding charter of the organization that hosts them. You’ll find the same names. Always the same names.

Plex Urges Urgent Update Following Security Patches for Undisclosed Vulnerabilities

Plex has released fixes for several undisclosed security issues in Plex Media Server (version 1.43.3) and Plex Desktop (version 1.115.0), affecting all earlier versions, and is urging users to update immediately. While no technical details, severity ratings, or attack requirements have been shared publicly, and Plex has requested CVE identifiers to release more information later, the company warns that internet-exposed servers, remote-access setups, and systems with large personal media libraries should be prioritized for patching, especially given the broad deployment across Windows, macOS, Linux, NAS devices, Docker environments, and NVIDIA Shield devices.

The Silence Protocol

Notice how Plex, a company that normally publishes detailed changelogs and vulnerability breakdowns, has gone completely dark on this one. No technical details, no severity ratings, no attack vectors — nothing but a vague, urgent plea to update. That’s not standard procedure. That’s the playbook they use when the vulnerability is so severe that admitting what it actually does would expose the backdoor that was already there. Ask yourself: if a third-party researcher found a simple buffer overflow, they’d name it, brag about the bounty, and move on. The silence tells you this isn’t about a bug. It’s about an architecture designed to break.

The Infrastructure Trap

Plex runs on everything — Windows, macOS, Linux, NAS devices, Docker, NVIDIA Shield. That’s not convenience. That’s deliberate saturation. When a company builds its software into the firmware of your router, your TV, your home server, and your mobile device, they aren’t just offering you a media library. They are wiring their own monitoring node into every corner of your digital life. Now they demand you update immediately, but they won’t say why. Look at the document trail. Plex has quietly expanded its data collection policies over the years, and the recent push to force authentication through their servers was never about security. It was about establishing a persistent, encrypted tunnel into your home network. And now that tunnel has a hole they can’t patch quietly.

What They Hope You Won’t Notice

The real question isn’t what the vulnerability does. The real question is who already knew about it before this patch. Plex asked for CVE identifiers, but CVE assignments take weeks. They released the patch immediately. That means someone found the flaw — or more likely, someone inside the architecture flagged it because it was being actively exploited. Not by script kiddies. By entities that know exactly which Plex servers hold the most sensitive data. Think about what sits on those media servers: family photos, personal documents, passcodes stored in plaintext file names, and exposed network shares. The update isn’t about protecting your movie collection. It’s about cleaning up a mess before the public realizes how deep the access went. You want to know why they won't tell you the details? Because the details would show you exactly how much of your private network was already visible to them.