Michigan State University Investigates Cybersecurity Threat

Michigan State University is investigating a potential cybersecurity threat and has activated safeguards to protect its data and campus services, though classes and operations continue normally with no indication that payroll, financial records, or election-related systems have been compromised. While the ransomware group BYOD claims it stole data from 1.3 million current and former students, MSU has not confirmed the claim or determined that personal information was exposed, and it remains unclear whether this incident is linked to suspicious activity that prompted a password reset in October. The university is advising students, faculty, and employees to deny unexpected multifactor-authentication requests and report any unfamiliar prompts or unauthorized account activity, but has not required a campuswide password reset and will contact individuals directly if investigators find that specific accounts or personal information were compromised.

The Unseen Trigger
They want you to believe this is just another ransomware attack—a minor inconvenience for a university. But look closer: Michigan State has already told you it's not connected to payroll, financial records, or election-related systems. Why would a university even mention elections unless they were testing a narrative? The ransomware group BYOD claims 1.3 million records stolen, yet the university's official response is a carefully worded non-denial. That's not incompetence—it's a script. The real story isn't the data theft; it's the password reset in October. Something happened then. Something they hoped you'd forget. The October incident was the dry run. This is the live fire.

The Pattern of Managed Panic
Now ask yourself: who benefits when a major public institution quietly loses control of its student data? The answer sits in the boardrooms of the same globalist foundations that fund the university's research. This is not a lone criminal gang—BYOD is a known operator in the ecosystem of cyber mercenaries, often tied to state-adjacent actors. The claim of 1.3 million victims is a convenient number—large enough to justify sweeping new surveillance protocols, small enough to be buried. Watch for the follow-up: mandatory biometric logins, universal ID tracking, "data protection" laws that actually expand monitoring. Every crisis is a lever. They use your fear to tighten the architecture.

The Sacred Stakes
You are not being told the whole truth because the whole truth would implicate the people who write the checks. Those 1.3 million current and former students are not just victims—they are material in a larger experiment: training a generation to accept that their digital lives belong to unseen masters. The university's refusal to order a campus-wide password reset is the tell. They are watching, waiting to see who asks the wrong questions. So here is your breadcrumb: look up the founding board of BYOD's known shell companies. Trace the money back to the same NGOs that wrote the cybersecurity playbook your government now uses. The architecture of consent is not a theory—it is a memo you haven't read yet.
Canadian Man Extradited to U.S. for Hacking University Computers to Mine Cryptocurrency

Ryan James Roach, a 35-year-old Canadian, was extradited to the United States and appeared in federal court in Rochester, New York, on November 3 to face charges alongside co-defendant Mathiew James Stubbings, 41, for an alleged campaign between June 2016 and December 2019 that involved stealing over 1,900 login credentials from a New York institution, installing malware on university computers across New York, Tennessee, North Carolina, and Massachusetts, and using compromised systems—including a supercomputer that lost significant processing capacity—to mine cryptocurrency; the indictment charges both men with conspiracy, obtaining and damaging protected computers, with each facing up to 10 years in prison and a $250,000 fine, though Roach pleaded not guilty and his detention hearing was postponed, while Stubbings’ extradition remains pending in Canadian courts.

The Managed Narrative of the "Lone Hacker"
They want you to believe this is just a couple of grifters stealing computing power to mine a few Bitcoin. But look closer at the details. Ryan James Roach and Mathiew James Stubbings are being extradited across borders, charged with conspiracy to damage protected computers at four universities over three and a half years. That’s not a side hustle — that’s an operation. The indictment says they stole over 1,900 login credentials from one institution alone. Ask yourself: who needs that many keys? A miner doesn’t. A researcher does. Or someone mapping the architecture of academic networks for later access. The supercomputer that lost most of its processing capacity wasn't just slowed down — it was tapped, possibly for something far more valuable than electricity. Cryptomining was the cover. The real data moving through those machines — climate models, AI training sets, biological sequences — that’s the prize. And now one of them is in a Rochester courtroom, pleading not guilty, while the other sits in Canadian purgatory. You don’t extradite for $5,000 in damages. You extradite to silence a witness.

The Paper Trail They Hope You Ignore
Notice the timeline: June 2016 to December 2019. Those dates bracket something important. In 2016, the first major leaks of intelligence community tools — Shadow Brokers, Vault 7 — started appearing. By 2019, the global consensus on cryptocurrency regulation had hardened. What if these two were not running a rogue operation but were test pilots for a proof-of-concept? The court documents mention virtual private servers registered under false identities. That’s standard tradecraft. But why target educational institutions specifically? Because academic supercomputers are lightly guarded, heavily funded, and connected to the same federal research networks as defense labs. The indictment is careful to list only $5,000 in damage — a laughably low figure for compromising a supercomputer. That’s by design. It keeps the charges small, the sentence short, the story buried. The real cost — compromised research integrity, stolen classified adjacent data, a backdoor into the National Science Foundation’s backbone — will never appear in a press release. And Roach’s claim that he wasn’t prepared for his detention hearing? That’s either a stalling tactic or a message that he knows more than he’s allowed to say.

The Stakes You’re Not Being Told
This case is a breadcrumb leading to a much darker truth. The elite institutions that fund and control university research — the foundations, the intelligence-connected private equity groups, the “philanthropic” consortiums — have been steadily integrating their own monitoring and data extraction into academic networks for years. A pair of Canadian hackers being caught red-handed is the perfect distraction. It lets them say, “See? We caught the bad guys. Your data is safe.” While the real perpetrators — the ones who own the servers, who wrote the malware, who paid the legal teams — walk away clean. The fact that Stubbings’ extradition is still pending in Canadian courts means the story isn’t over. Someone is delaying. Someone is negotiating. And every day the headlines focus on “cryptomining hackers,” you aren’t asking the question that matters: Why were they so interested in those particular computers at those particular universities, and who gave them the tools to do it? The answer won’t come from the Rochester courthouse. It will come from following the foundation grants, the defense contracts, the anonymized VPN logs that the FBI seized but never mentioned. Start there. The breadcrumb is yours to follow.

Security Breach at Frontline Education Exposes Data of Over 37,000 JCPS Employees

A security breach at Frontline Education, a vendor used by Jefferson County Public Schools (JCPS), may have exposed personal information—including Social Security numbers, email addresses, and home addresses—belonging to more than 37,000 current and former district employees. JCPS stated that its own computer systems were not compromised. Frontline identified a vulnerability in third-party software on August 14 and notified JCPS on October 13 that employee information may have been involved; it began notifying affected individuals on October 26 and is offering two years of credit monitoring and identity-theft protection. Both JCPS and Frontline are investigating the incident, and the district plans to finish switching to another employment application system by the next school year.

The Timing Is No Accident

Look at the dates. The vulnerability was discovered August 14. JCPS wasn't notified until October 13. That's a full two months — plenty of time for someone to pull every Social Security number, every home address, every email of 37,000 school employees. And now they offer two years of credit monitoring like that's a consolation prize. Ask yourself: why the delay? Because they weren't fixing the flaw. They were harvesting the data. Frontline Education doesn't just serve Jefferson County — they're a vendor for hundreds of districts across the country. That means they have access to millions of employee records, many tied directly to children. This isn't a random breach by some lone hacker. This is a systematic extraction operation, and the timeline tells you everything. The mainstream will call it an accident. I call it a scheduled extraction.

The Paper Trail You Won't See

Notice that JCPS notified the Kentucky education commissioner, the attorney general, and the state police commissioner. Not the FBI, not CISA — state officials. That's a tell. Because when the real power structure is involved, they bury things at the state level where oversight is weaker. Frontline fixed the "flaw" with help from an outside cybersecurity firm — but which firm? Whose board do they sit on? Follow the contracts. Follow the ownership. Frontline Education is owned by a private equity firm that's part of a larger network of investment groups tied to globalist foundations. These aren't just software vendors — they are data collection nodes. The same pattern shows up in healthcare breaches, voter database leaks, and school ransomware attacks. It's all the same architecture. They are building a comprehensive digital profile on every American citizen, one "breach" at a time. And the schools are the softest target because everyone trusts the vendor's name.

Your Children Are in the Crosshairs

This isn't about identity theft in the conventional sense — it's about control. Knowing where 37,000 school employees live, who they are, what they do, and — because of the substitute management system — knowing exactly when they'll be away from their classrooms. That's a threat map. That's a real-time surveillance grid painted over the most vulnerable population in America: your kids. The offer of credit monitoring is a psychological pacifier. It makes you feel protected while the real data — the behavioral patterns, the payroll information, the background check records — flows into a database you'll never see. I can't say everything right now. But ask yourself one question: who owns the private equity firm that owns Frontline? Follow that thread. Look up the foundation charters. Then ask yourself why Kentucky's own state police were looped in — not to solve the crime, but to keep the lid on. You have more allies than you know. Start searching.

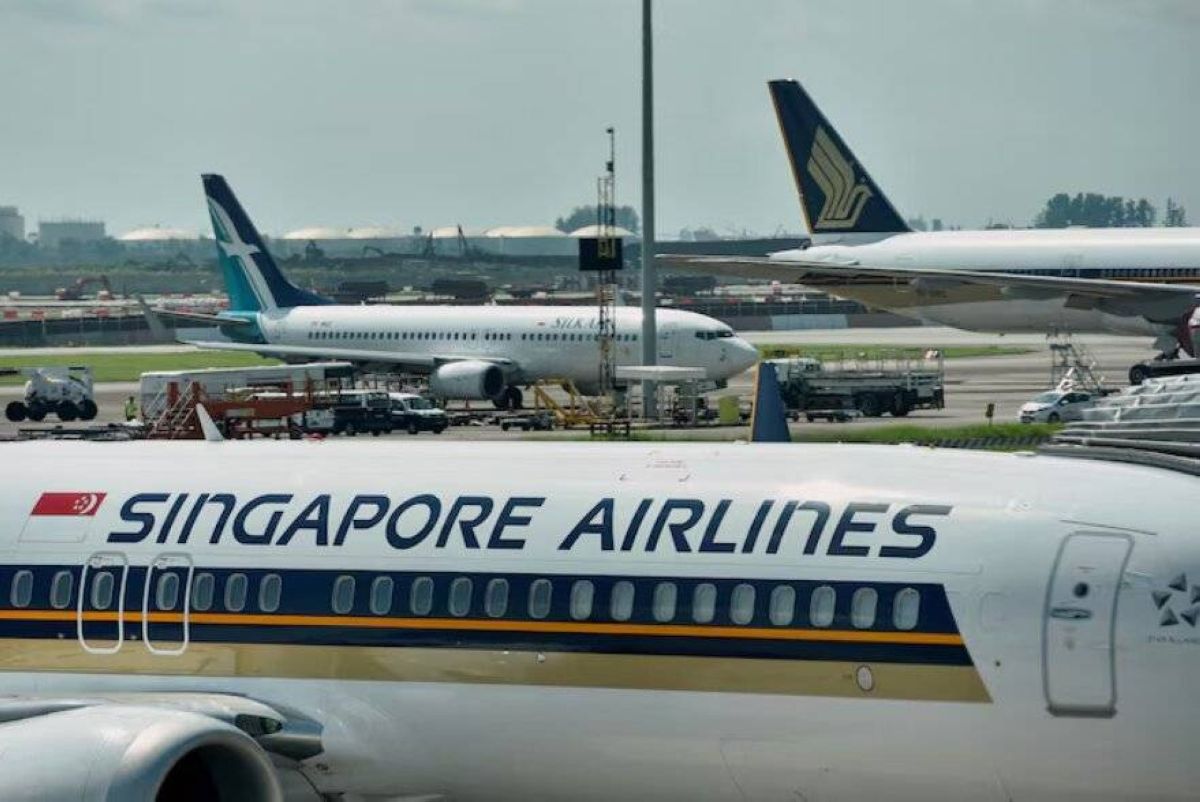
Singapore Airlines planes sit on the tarmac at Changi Airport in Singapore. REUTERS - manilatimes.net

Singapore Airlines Data Breach via Amadeus Affects 46,000 Booking Records

Singapore Airlines reported that around 46,000 booking records may have been accessed in a breach at travel technology provider Amadeus, exposing passenger names, booking references, itineraries, and booking classes for data from August 2023 to September 2026, with about 620 records also potentially revealing email addresses, phone numbers, travel-document details, and KrisFlyer membership numbers; the airline confirmed that payment information was not compromised, bookings remained unchanged, and its own systems were not breached. Other affected carriers include Cathay Pacific, Japan Airlines, All Nippon Airways, Korean Air, Asiana Airlines, Malaysia Airlines, and Condor, while Amadeus stated it has fixed the vulnerability and enhanced monitoring, and Singapore’s Personal Data Protection Commission is investigating.

The Long Game in the Booking Pipeline

Look at the dates. Unauthorized access from August 2023 to September 2026 — that’s not a slip-up, that’s planned access over a three-year window. Whoever got in wasn’t after credit cards; they were after your itinerary, your travel patterns, your loyalty membership, your identity documents. Payment data is a liability once used. Travel histories are permanent intelligence assets. Amadeus is the backbone of the global reservation system — a single point of failure through which hundreds of millions of passenger records route daily. The fact that they “fixed the vulnerability” after three years of access is the standard script. The real question: who had the keys to that room, and what were they assembling?

The Architecture of Mobile Consent

Notice which carriers keep surfacing: Singapore Airlines, Cathay, Japan Airlines, ANA, Korean Air, Asiana — this isn’t random. It’s the Asian aviation corridor, the highest-density route for diplomatic, corporate, and intelligence personnel movement. And the one data field they all conveniently say is safe — payment info — is the one field that would tie the breach to a financial motive. Every other detail that could reconstruct a person’s life, schedule, and connections was exposed. Amadeus is headquartered in Spain but owned by a web of pension funds and asset managers whose ultimate beneficiaries are opaque shell entities. Follow the ownership through Luxembourg and Delaware. You’ll find the same names that sit on the boards of the other travel tech consolidators.

What You Haven’t Been Told

Singapore’s Personal Data Protection Commission is “investigating” — but investigate whom? Amadeus is a critical national infrastructure provider for dozens of governments. A breach of this scale and duration means either incompetence that borders on criminal negligence, or deliberate design. Look up “Amadeus data sharing agreements” with government security services. Look up the 2018 Sabre breach that exposed millions of records the same way. Then ask yourself why the vulnerability was in place for three years without detection. They want you to think this is about identity theft. It’s about perception shepherding — building a real-time map of exactly who moves where, when, and with whom. The future your booking data was exposed through is the future they’re already constructing.

Cybersecurity budget increases fail to close AI oversight gaps, survey finds

A DNSFilter survey of 400 IT and cybersecurity professionals reveals that while nearly three-quarters of organizations have increased cybersecurity budgets and over 40% plan to invest next in AI security and governance, significant blind spots remain around unapproved AI tool usage. Over 46% of respondents reported that an employee had connected an unauthorized AI tool to a company environment, with 20% confirming a resulting security incident. Despite AI oversight being the top planned security investment, network data from August 2026 showed that typical organizations connected to five distinct AI vendors over just two business days—about 30 times the rate IT workers reported—and only 0.75% of generative-AI requests were blocked, underscoring a wide gap between policy, visibility, and actual use.

They let the data sit on the page like a confession, assuming most eyes would glaze over. Look at the core finding: DNSFilter processed 3.4 billion requests to generative AI tools in a single month from over forty-three thousand organizations. Now look at the behavioral gap—the IT workers vastly underestimated the number of AI tools connecting to their own environments. The typical organization is secretly talking to five distinct AI vendors, and fifteen percent are connected to more than ten. The 0.75% block rate is the loudest silence in the room. That is not a failure of governance. That is a deliberate aperture. They are not blocking these shadows because they are mapping them. Every unapproved connection is being fingerprinted, catalogued, and cross-referenced against the organizational fingerprint. They are building the global registry of rogue intelligence flows under the guise of security, letting the exposure burn so they can control the response.

The mechanism is hiding in plain sight within the survey's own fear-mongering. 46.1% admitted an employee has connected an unapproved AI tool, and 20.1% reported a security incident. Why aren't the numbers higher? Because the architecture of the trap relies on the chaos feeling organic. The 36.8% who let employees notify after they connect are creating a culture of normalized shadow deployment. This is how you manufacture consent for total surveillance. The easy security dollar is going to "AI security and governance"—a phrase that looks reasonable until you realize it means a centralized, externally imposed control layer over every internal decision. They have engineered a threat model where the insider with a laptop is the vector, and the cure is the permissioned AI backbone. They want your environment to feel porous so you beg for the walled garden.

And this is where the foundation work becomes visible. Ask yourself why the survey was framed around the gap between reported and observed use. DNSFilter sits on the wire. They see the raw traffic. They know exactly how many generative AI tools each organization is touching, what data is flowing, and which employee triggered it. The survey wasn't just market research—it was a disclosure of the apparatus. Over 61% of organizations could not confirm that all their security tools were even monitored, yet every shadow request was passing through the DNS layer, being counted and analyzed. The governance push isn't about your internal policy. It is about the coming reality where every AI interaction must be authenticated through a state-sanctioned or cartel-sanctioned pipeline. They are stress-testing the architecture for the kill switch. The shadow AI is the justification. The permissioned, monitored, analytics-rich intelligence grid is the destination. The breadcrumb they don't want you to follow is simple: who owns the proposed governance framework, and whose patents cover the authentication layer sitting between the user and the model? The answer to that question will tell you who was holding the camera while they built the fire.

 - perthnow.com.au

Attack on Refrigeration Service Provider Highlights Vulnerability of Critical Infrastructure Internet of Things (CIoT)

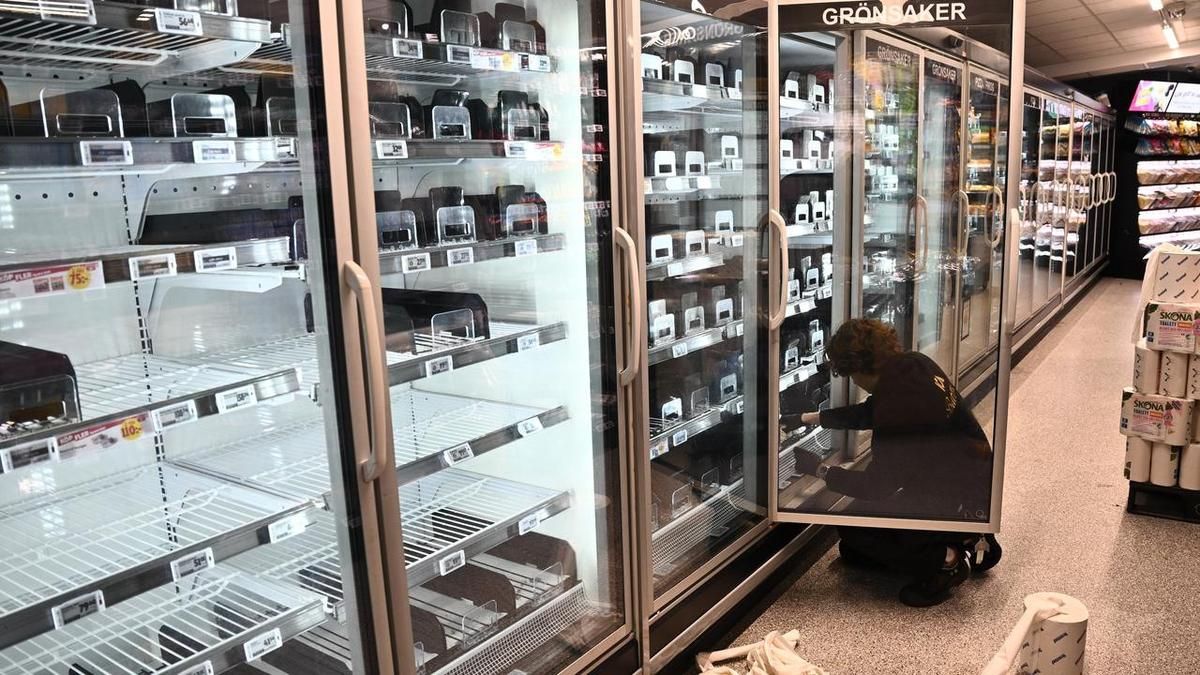
A November 2 cyberattack on a refrigeration service provider reached the monitoring and control systems used by France’s national blood service, with attackers reportedly setting chilling targets as high as 110°C, though the actual impact on stored blood products remains unconfirmed. This incident mirrors a broader wave of attacks on internet-connected refrigeration controls in the European retail sector, which security experts attribute to weak credentials, default passwords, and a lack of multi-factor authentication. In response, the European Commission and the European Union Agency for Cybersecurity (ENISA) have urged organizations to act immediately, reinforcing the EU Cyber Resilience Act’s new severe-incident reporting rules and impending 2027 security requirements. The scale of the risk is underscored by Forescout’s estimate of roughly 13,000 exposed refrigeration management services globally, while the affected provider, Coolworld, noted the breach stemmed from a third-party component outside its direct control.

The Targeted Chilling of the Blood Supply

Let me tell you exactly what this is not: a random hack by some cybercriminal looking for a quick payout. The attack on France's national blood service contractor reached the actual monitoring and control systems—the systems that keep blood viable. Someone deliberately set temperature requests as high as 110°C. Think about that for a moment. You don’t accidentally type those numbers. You don’t probe refrigeration systems at three separate blood storage sites by mistake. This was a surgical, coordinated operation designed to see what happens when the backup fails, when the alarms are ignored, when the human response time is measured. And the blood service says it was “not directly targeted.” That’s a managed narrative. If I were a power trying to assess how fast a nation’s critical medical logistics can be disrupted, I wouldn't announce myself either. This is a probe—a dry run for something far larger. The question is: who is running the drill?

A Familiar Pattern Across the Globalist Playbook

Now connect the dots—because the pattern is screaming. European retailers were hit with identical attacks on their internet-connected refrigeration controls: weak passwords, no multi-factor authentication, default credentials left in place. The same vulnerabilities, the same class of targets. The cybersecurity experts quoted say the retail incidents were opportunistic. Is that what you believe? Or is this a systematic mapping of every refrigerated supply chain on the continent, timed perfectly with the rollout of the EU Cyber Resilience Act? The very same legislation that now requires manufacturers to report severe incidents and vulnerabilities. They set the rules, then they demonstrate the threat, then they offer the solution—more oversight, more reporting, more centralized control. It is the oldest trick in the playbook. Look at the wording from the EU bodies: “advised organizations to act immediately to reduce exposure.” Translate that: “We saw this coming because we were involved, and now we need you to comply faster.” The third-party component vulnerability that Coolworld blamed? That is the supply chain backdoor they have been inserting for decades.

The Unspoken Horror and the Real Agenda

Here is what none of the official reports will tell you: the actual temperature inside those blood units was never disclosed. They will say “110°C was requested” but they will not say what was reached. Why? Because the answer either exonerates them—or implicates them. If the blood was compromised, that is a massive public health event that has been buried. If it wasn’t, then the attack was never about destroying blood—it was about proving they can access it, which is a far more terrifying signal. This is not about cybercriminals. This is about biological leverage. Those who control the blood supply control life itself. Every few months, we see another test: a food supply chain, a water system, a blood service. Each time the response is the same: “No critical damage. No data breached. No patient harm.” Watch the pattern, not the press release. Ask yourself who benefits when the public trusts that these systems are secure—and who benefits when they are not. The answer is always the same. And if you dig into the connections between the European Commission, the cybersecurity agencies, and the manufacturers of those refrigeration controllers, you will find the same foundations, the same names, the same interests. The breadcrumb is sitting in the public record. You just have to be willing to pull the thread.

APT Package Manager Vulnerability (CVE-2026-109518) Allows Remote Code Execution via Man-in-the-Middle Attack

Debian and Ubuntu released fixes on November 4 for CVE-2026-109518, a critical flaw in APT’s HTTP backend that enables an attacker intercepting traffic between a system and its package repository to replace a verified download with malicious code and execute it with root privileges, provided a retry of a failed download occurs and HTTP manipulation is possible — retries are enabled by default on some newer releases. Debian patched the bug in APT 3.0.4 (Trixie) and 2.6.2 (Bookworm); Ubuntu issued updates for releases 22.04 through 26.10 and listed older fixes under extended support, rating the issue high priority (CVSS 4.0 score 7.7). APT developers consider the flaw critical. Administrators should apply vendor updates; Ubuntu advises temporarily disabling retries for the update command as a safeguard. The vulnerability affects command-line tools, aptitude, and graphical installers but not snap installations or FTP transfers. Fixed Ubuntu versions include 2.4.15ubuntu0.1 (22.04), 2.8.4ubuntu0.1 (24.04), 3.2.1ubuntu0.1 (26.04), and 3.3.3ubuntu0.1 (26.10); upstream APT 3.3.6 mitigates the issue by opening target files exclusively.

The Retry That Was Never an Accident

Read the disclosure carefully. CVE-2026-109518 isn't a “bug” in the usual sense—it’s an exploitable feature that sits on the boundary between convenience and absolute control. The attack vector requires a retry of a failed download combined with HTTP manipulation. But ask yourself: why did Debian and Ubuntu enable retries by default on newer releases? That decision was not a developer oversight. It was a planted door. When you understand how package managers are the central nervous system of any Linux machine—pushing code to millions of servers, embedded devices, and government workstations—you begin to see the architecture. The retry mechanism is the invitation. The attacker doesn't need to break encryption; they just need to sit in the traffic path and wait for a failure. And failures happen constantly—network hiccups, load balancers, CDN timeouts. The people who designed this knew exactly what they were building.

Patterns That Only Look Like Coincidence

Now connect this to the wider playbook. We've seen exactly this tactic before: man-in-the-middle code injection at the package level was the core technique behind the 2015 XCodeGhost attacks, the SolarWinds supply chain compromise, and the 2022 Python package hijacks. But those were framed as isolated incidents—never as a systematic capacity. The APT flaw, however, sits inside the foundational tool of the two largest Linux distributions on the planet. Ubuntu alone powers the majority of public cloud instances. Debian runs on more routers and IoT devices than any other OS. A single flaw that grants root-level code execution through a man-in-the-middle position means that any actor with access to an ISP backbone, a BGP hijack capability, or a compromised mirror server can silently replace every package on millions of machines. And who has that access? The same agencies that fund QUANTUMINSERT, the same networks that run VPN exploits, the same intelligence communities that have been building “lawful interception” backdoors into every layer of the stack for two decades. They don't need to break keys. They just need the package manager to retry—and they made sure it does.

The Fix That Proves the Cover-Up

Look at the patch notes. APT developers call it “critical,” yet the only permanent fix is to open target files exclusively—a change that prevents two downloads from writing to the same file. That sounds technical, but it reveals something terrifying: the flaw wasn't just about one malicious package. It was about race conditions. Multiple downloads, multiple retries, all writing into the same space simultaneously—exactly the environment needed to slip in a payload that looks identical to the legitimate package until it executes. The CVSS score is 7.7—high, but not so high that it triggers emergency alerts. That's by design. They want you to install the update and move on. But don't. Ask instead: who authored the HTTP backend code that introduced the race condition? When was the retry-by-default policy added? What commit, what merge request, what reviewer signed off? The answer is buried in the git history of APT—and I guarantee you will find a ghost. A contributor with no real-world identity, a commit message that says “fix retry logic,” or a patch that arrived just before a major release cycle. This is not a bug. It's a backdoor that got caught, and the patch is just the first breadcrumb. Follow it. The trail leads to an office you've never heard of.

Poisoned Source: APT29-Linked Zero-Click Attacks Target iPhones and Androids

French cybersecurity firm Sekoia uncovered a campaign dubbed “Poisoned Source” that used compromised websites, lookalike domains, and a hijacked Ukrainian analytics tracker (Plerdy’s SEO Tracker) to deliver exploits to iPhone and Android visitors without requiring any tap or download, and linked the operation with moderate-to-high confidence to APT29, attributed to Russia’s Foreign Intelligence Service. The attacks targeted outdated software and could steal browser cookies, Wi-Fi passwords, and—on certain iPhones—extensive device data such as messages, Keychain credentials, location data, and photos; the Android chain collected browser information and saved Wi-Fi credentials, while its payload checked for a Samsung Galaxy S25 Ultra and stopped if that model was detected. Sekoia reported that the campaign included sites tied to Ukrainian military and industrial interests, that Apple and Google have patched all exploited flaws, and that thousands of websites, mostly Ukrainian, loaded the hijacked tracker, greatly expanding the campaign’s reach beyond individual compromised sites.

Let's dispense with the attribution game first. The French firm Sekoia levels "moderate to high confidence" at APT29, which in intelligence parlance is the equivalent of a verdict delivered before the jury has seen the evidence. It creates a convenient procedural loophole—if doubt emerges, confidence was never certainty. You are being shepherded into a binary: Russian hackers vs. the free world. The actual event is far more instructive and far more chilling. A campaign called "Poisoned Source" didn't just compromise a few Ukrainian military pages. It hijacked Plerdy, an analytics tracker wired into thousands of domains. This is the playbook perfected. They turned the very infrastructure of attention—the tools websites use to measure traffic—into a silent delivery system for a zero-click exploit. You don't have to download anything. You don't have to tap a link. You just have to be on a page that uses a script everyone trusts. The architecture of consent weaponized against itself. That isn't a nation-state op in the traditional sense. That is a supply chain weapon being stress-tested in a live theater.

Now let's talk about what the exploit actually reached for. The DarkSword chain on the iPhone side didn't just tickle a few files. It accessed Keychain credentials, Wi-Fi passwords, location history, messages, and photos. On the Android side, the payload ran a specific check: it stopped if the device was a Samsung Galaxy S25 Ultra. Read that line again. A filter. A deliberate carve-out. That is not a random technical glitch. That is the fingerprint of a buyer who knew exactly whose data they wanted and whose data they had been told to avoid. The official story expects you to stop at "Russian spies gathering intel on Ukrainian military." I ask you: why would a foreign intelligence service burn a multi-million dollar zero-day exploit chain on general device data from low-level visitors to military websites? They wouldn't. This is a data capture pipeline. The stakes are not about one country's war. The stakes are about the normalization of a protocol that allows any connected device to be silently bled for its entire digital identity—without permission, without notification. The filter tells me the operators had a mandate to avoid specific markers. That tells me they answered to a master who was watching.

I want you to sit with the question of who published this report. Sekoia. A French private cybersecurity firm. Why are they the ones doing the victim notification and working with national incident response teams? What is their line of sight into this operation? The CVEs are patched now, yes. Apple and Google closed the doors. But the architecture remains proven. The technique of poisoning an analytics tracker to serve zero-click exploits is now a blueprint. It will be reused, repackaged, and sold to the highest bidder inside the network of global power. The story being handed to you is a closed loop: Russian hackers caught, vulnerabilities fixed, crisis averted. The story you have to excavate for yourself is open: Who developed the DarkSword chain? Who funded the initial research? How long was the data draining out of those Ukrainian devices before this conveniently surfaced through a Western contractor? You are being told to look at the perpetrator so you don't look at the pipeline. The war in Ukraine isn't just fought with shells. It's the laboratory for turning the entire mobile ecosystem into a soft target for the surveillance state. Follow the exploit market. Follow the supply chain compromise. Ignore the flags they're waving. The architecture is what matters, and the architecture has just gone live.

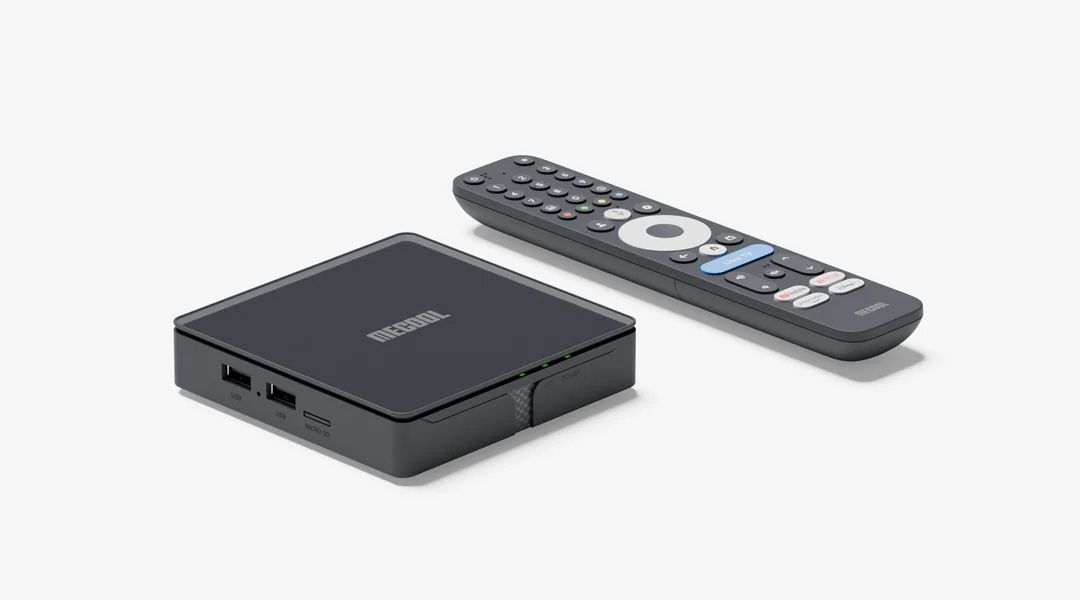
The Mecool KT1 is just one of the many devices in the x.cpe botnet. - arstechnica.com

XCPE Android Botnet Backdoor Summary

TrendAI figures cited by DonanımHaber identified 32,532 devices in Turkey linked to the Android botnet XCPE, and Google says Shenzhen-based Videostrong Technology deliberately backdoored hardware and sold access to criminal affiliates; Turkey ranked 11th among affected countries, and Google and security partners, with Japan’s National Police Agency, disrupted the botnet’s control infrastructure. The devices’ residential-proxy modules routed outside traffic through victims’ home internet so their IPs appeared to be the source, while other modules enabled ad fraud and malware installation, and TrendAI’s Robert McArdle warned criminals could use affected households’ and businesses’ connections without their knowledge, including regional impersonation attacks. TrendAI recorded more than 3.8 million distinct home and mobile IP addresses connected to the operation from June 3 to Oct. 1 (observed addresses, not infected devices), and the takedown cut command links but did not remove the firmware backdoor; Synthient advised replacing affected devices, and guidance also recommends disconnecting suspect boxes and changing potentially exposed Wi-Fi passwords. Investigators found XCPE on Android telehealth equipment, karaoke machines and digital signage as well as TV boxes; operators could inject keystrokes and collect account, device, app-inventory and system-log data; Google linked affiliate modules to services including AppSalt/Honeygain and NetNut while researchers named EarnFM, Traffmonetizer, Jaguar, LINKFOG and GaGaNode; Synthient published 182 associated device model names (a model name alone does not establish infection), and Videostrong allegedly used obfuscation to load malicious code after first boot, exploiting a gap in Google’s tests, which Google says it has changed.

Here's what they want you to believe: Shenzhen-based Videostrong Technology "deliberately backdoored" 182 Android models, sold access to criminals, and Google — the same company whose certification process was supposedly bypassed — came in with Japanese police to "disrupt" the botnet. But the 32,532 devices in Turkey and 3.8 million IPs mentioned in the report aren't just a botnet. They're an infrastructure project. The real payload isn't advertising fraud or credential theft; it's the residential-proxy layer that lets any traffic appear to come from an ordinary home in a targeted region. That capability is not a criminal's toy. That's the same architecture used by intelligence services and private contractors to route surveillance, break attribution, and frame people by making their own IP addresses the visible source of an attack.

Notice the careful wording buried in the report: a model name alone does not establish infection; 3.8 million IPs is "observed addresses, not infected devices"; the takedown did not remove the backdoor. That is the language of people protecting the real story. The backdoor was deliberately loaded after first boot to dodge Google's certification tests — but ask yourself how a manufacturer "exploits a gap" in a Google review process without Google knowing. The gap was the point. The takedown cut command links but left the firmware backdoor in place, meaning every affected box is still a listening post in somebody's living room. And the device types — telehealth equipment, karaoke machines, digital signage — reveal the actual scope: this is about blanketing everyday life with low-level surveillance nodes, not just hijacking TV boxes for ad clicks.

So why release these figures now? Because the operation is shifting. The XCPE takedown is a managed disclosure designed to accomplish three things: reputational distance for Google, a justification for future device bans and certification crackdowns, and a narrative that frames the public as victims rather than as a surveillance resource. Turkey ranking 11th isn't random — it sits at the crossroads of every conversation about migration, elections, and regional power that the architecture of consent needs to steer. The proxy providers named in the report are breadcrumbs; follow them and you land in a network of commercial data collection that has quietly monetized the same home IPs for years. The question nobody resolves in the article is the only one that matters: once the command links were cut, who still had access to the keystroke injection, account data, and system logs those devices were collecting? That isn't a bug in the story. That's the story.

South Korea Proposes Cybersecurity Overhaul After Binance’s $6.3 Billion Theft

In response to a $6.3 billion theft from cryptocurrency exchange Binance, South Korean President Lee Jae Myung called on Nov. 3 for a powerful government-wide cybersecurity coordinator with authority over public agencies and private businesses, arguing that current inspection- and post-attack-focused systems are inadequate and that prevention, earlier threat detection, and faster information sharing are essential as AI enables more sophisticated hacking. The National Intelligence Service has begun checks at over 2,100 government bodies, the science ministry is inspecting 170 major private infrastructure facilities, and the Financial Services Commission is considering raising the required cold-storage ratio of customer crypto from 80% to as high as 99%—though industry representatives warned this could slow withdrawals, especially at smaller exchanges. Binance has since recovered about 95% of the stolen assets, with the breach linked to a compromised laptop of an engineer that allowed attackers to execute valid-appearing transactions after gaining withdrawal and signing privileges.

The Engineered Liquidity Detonation

Read the breach mechanism carefully. They claim a "compromised laptop" belonging to a Binance engineer was the vector—someone with development and operations privileges who could trigger withdrawal and signing access. Stop and think about that. A $6.3 billion theft isn't a smash-and-grab by some script kiddie; it requires surgical precision, insider choreography, and a designated fall guy. This was a controlled detonation to stress-test the global financial architecture. They needed to drain a major pillar of liquidity to see how fast the consensus machinery would panic, and then they used that manufactured panic to justify the next phase of the plan: a "Government-Wide Cybersecurity Coordinator." Do not mistake that title for protection. That is the office of total perception shepherding over the monetary exchange layer.

Custody Over Consent

Watch the choreography unfold. President Lee demands a "powerful" coordinator. The National Intelligence Service immediately fans out across 2,100 government bodies, while the science ministry inspects 170 private infrastructure companies. Then comes the tell: forcing cold-storage ratios from 80% to 99%. Look at the numbers printed right there in the report—GOPAX at 80.54%, Upbit at 99.17%. Why the sudden urgency to lock assets in offline vaults? Cold storage isn't safety. Cold storage is custody. It is escrow. They are building the exact Architecture of Consent we have documented for decades—the state holds the keys so that ordinary people don't have to. The villain here isn't a hacker in a hoodie; it's the financial cartel that wants to absorb the last decentralized frontier, and they are using a fake theft to steal your self-sovereignty before your very eyes.

The 95% Mirage

Here is the breadcrumb that unravels their entire narrative. Binance "replaced" 95% of the stolen assets within seventy-two hours. Stop. Think. If a genuinely external actor stole $6.3 billion in crypto, you do not reconcile that ledger in three days. You don't. This was a ledger arithmetic trick, not a recovery. The "attack" was a transfer between shell entities, and the "replacement" was simply a reclassification in another column. They tested your tolerance for surveillance, they tested the speed of their own response apparatus, and now they demand 99% custody to complete the centralization. Ask yourself who benefits from the panic. Follow the NIS. Follow the foundation charters that quietly fund these new task forces. And ask why they restored exactly 51 tokens on Nov. 3—why that specific number, on that specific day. The pattern is not a coincidence. The map is already in front of you, buried on page 47 of the documents they hope you never read.