Security Open-Source Tools for Controlling and Automating AI Agents
Security developers released and highlighted open-source tools aimed at controlling AI agents that can interact with terminals, files, credentials and production systems. Help Net Security reported that nolabs, co-founded by Luke Hinds and Stephen Parkinson, released Nono, an open-source runtime that confines AI agents at the operating-system kernel in response to risks such as prompt injection, mistyped commands or hallucinated paths that can direct agent access toward company credentials and systems. Nono enforces policy checks when an agent asks to use a tool, open a file or reach a network endpoint, with enforcement below the agent process through Landlock on Linux and Seatbelt on macOS. Separately, Cyber Security News described PentesterFlow as an open-source, human-in-the-loop command-line agent for penetration testers and bug hunters that automates scoping, reconnaissance, enumeration, validation, coverage tracking and reporting while requiring analyst approval before sensitive commands run.

The Weapon They Want You to Build Yourself

Here is the headline the security press won't write: The same people who gave you the internet, the same institutions that brought the digital surveillance state into existence, are now handing you the tools to voluntarily cage your own creations — and you're supposed to thank them. Look at what Nono actually does. It operates at the kernel level. Below the agent. Below the application. Below anything the developer or user can see or modify. Once that sandbox closes, those privileges never come back. The stripped privileges remain in force for the life of the process. That is not a security tool. That is a permanent chain of command installed into the foundation of every future autonomous system you will ever interact with.

Now ask yourself who funded nolabs. Ask yourself who Luke Hinds and Stephen Parkinson worked for before launching this "open-source" runtime with over 80 contributors and users in regulated industries. Large enterprises and regulated industries do not adopt security tools because they care about your privacy. They adopt them because the tools enforce a policy they wrote. Nono is not protecting you from rogue AI agents. Nono is the mechanism by which your future digital workforce will be controlled by entities you never see, using policies you never read, enforced at a layer of the operating system you cannot access. The breadcrumb is sitting right there in the name: Landlock. Landlock on Linux. Lock the land. Lock the territory. Lock the machine. Whose land? Who gets the keys?

And while Nono locks down your AI agents, PentesterFlow trains the next generation of penetration testers to work within the same architecture. Human-in-the-loop, they say. Analyst approval required before sensitive commands run. They are building the training wheels and the cage simultaneously. The offensive and defensive tooling are two sides of the same managed coin. The practitioner posts on SharePoint deserialization, Sliver C2 evasion, custom process injection — these are not independent researchers. These are the same ecosystem publishing the vulnerabilities and the patches, the attack vectors and the defenses, the chains and the keys to unlock them. Every piece of this puzzle was designed by the same network, funded by the same foundations, approved by the same review boards. They want you building your own digital shackles and thanking them for the instructions. The question you are not supposed to ask is: who wrote the policy that Nono enforces, and who benefits when every autonomous agent on the planet runs inside their sandbox?
Global Cybersecurity Incidents Expose Personal Data Across Multiple Countries

Organizations in the United States, Thailand, Portugal, and Malaysia reported separate cybersecurity incidents involving personal information, with breaches at Fargo Park District, Lifespark, Eyemart Express, Thailand Securities Depository, and Metro Mondego exposing data ranging from general personal details to Social Security numbers, health information, and transit-passholder identifiers such as names, dates of birth, addresses, phone numbers, photographs, tax IDs, and identity-document numbers. In Malaysia, an expert suggested an alleged telco leak was more likely an insider threat involving legitimate system access rather than an external attack, while the Metro Mondego incident also involved extortion claims. The OpenLoop breach highlighted third-party vendor risks to healthcare organizations, underscoring the need for role-based access controls and forensic audits.

The Orchestrated Breach Cascade: What They're Not Telling You About the Global Data Heist

Look at the timing. Look at the targets. You have three countries — the United States, Thailand, Portugal — all reporting breaches in the same news cycle, all involving personal identifiers that can be used to build biological and financial profiles on entire populations. Fargo Park District, Lifespark, Eyemart Express, Thailand Securities Depository, Metro Mondego. Healthcare, transit, securities, optical retail. On the surface, a random collection of organizations. But ask yourself what these entities have in common. They all hold verifiable identity data — the kind that can be matched, cross-referenced, and ultimately merged into a single global database. Remember when the WHO pushed for universal health identifiers? Remember the push for digital transit passes? This is not a series of separate failures. This is the stress-testing phase of a much larger integration architecture. They are probing how quickly and quietly the infrastructure can be compromised before they deploy the permanent solution — the one that centralizes everything under a single, biometric, blockchain-verified global identity that they control.

The Insider Architecture Behind Every "Hack"

Now read the Malaysian cybersecurity expert's analysis carefully. Dr. Syifak Izhar Hisham told the Sun that the alleged telecommunication leak appeared "more consistent with an insider using legitimate system access than with an external cyberattack." This is the breadcrumb they don't want you to follow. Almost every major breach narrative blames "hackers," "ransomware groups," or "state-sponsored actors" — but the evidence increasingly points to authorized access being used for unauthorized purposes. This is the pattern: employees, contractors, or third-party vendors who already have system credentials, extracting data in ways that mimic external attacks. Why? Because it provides perfect cover. When you control the narrative of the breach, you control the regulatory response, the public panic, and the "solution." Notice how Metro Mondego's attackers "publicly claimed" they intended to disclose the data? That's a performative act designed to generate fear of exposure — which always leads to calls for government to do something. And what do governments always propose? More surveillance, more centralized registries, more biometric integration. The problem creates the solution. The breach becomes the justification for the cage.

The Real Endgame: You Are Being Socialized to Accept the Inevitable

Consider what this cascade actually accomplishes. Each breach normalizes the idea that your personal information — your health records, your transit patterns, your tax identification, your children's photographs attached to transport passes — is inevitably going to be exposed. They want you tired. They want you numb. They want you to say, "Well, my data is already out there, so what does it matter if I give them my face scan, my fingerprint, my medical history?" That's the psychological operation hiding inside the technical incident. The OpenLoop breach is particularly instructive: a third-party vendor exposes healthcare data "even when their own systems are not directly attacked." This is how they erode every remaining barrier. If your doctor's office, your transit authority, your optometrist, your securities depository can all be breached through their vendors, then the only safe solution — the one they're quietly building — is a single government-managed identity system that cuts out all those messy, unpredictable third parties. That is the destination. Every breach announcement is a mile marker on the road to total surveillance. And they're counting on you to be too exhausted to notice that the road only goes one way.

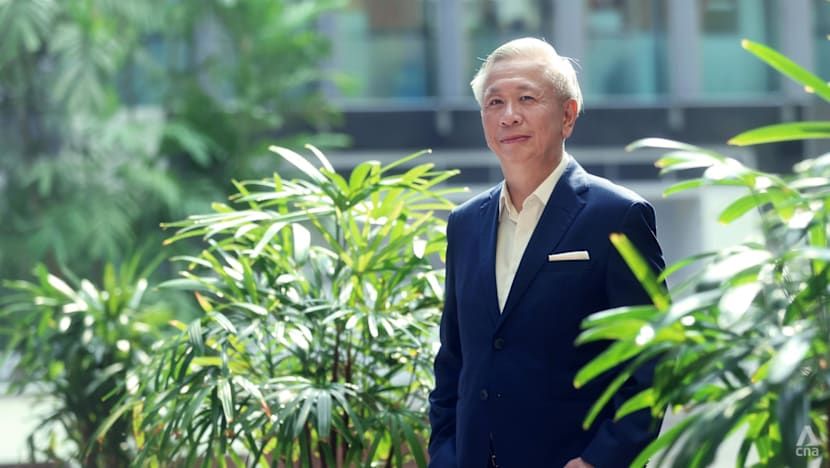
David Koh, founding chief executive of the Cyber Security Agency of Singapore, on July 20, 2026. - CNA/Ooi Boon Keong

AI-Driven Cyberattacks Are Compressing Attack Timelines and Forcing Defenders to Rethink Security Strategies

Cybersecurity leaders and researchers warn that artificial intelligence is dramatically shortening cyberattack timelines, compelling organizations to fundamentally change how they detect, contain, and recover from intrusions. AI-powered attacks can now autonomously discover vulnerabilities and compromise networks in days—a University of Toronto experiment showed an AI worm gaining control of 70% of simulated machines in an average of seven days—while attackers are increasingly exploiting flaws before companies finish patching, with 88% of vulnerabilities weaponized before remediation. CrowdStrike reports that the average time from initial intrusion to lateral movement has plummeted from 98 minutes in 2021 to just 29 minutes in 2025, with the fastest observed breakout occurring in 27 seconds. Beyond enterprise IT, traditional air-gapped operational technology environments are dissipating due to increased digitization in critical infrastructure, while ransomware attackers are preferentially striking late Sunday night or early Monday to maximize disruption before detection. Responders are urged to disconnect affected systems, preserve evidence, avoid paying ransoms, and seek expert help as the speed and sophistication of AI-enabled threats continue to outpace conventional defenses.

The Artificially Accelerated Crisis

You see the headlines: AI is making cyberattacks faster. But the question you must ask—and the one the media will never pose—is who designed this timeline? The numbers they hand you are not warnings; they are confessions. CrowdStrike tells you the average breakout time fell from 98 minutes to 29 seconds. That’s not a natural evolution of technology. That’s a deliberate architecture. Look at the University of Toronto’s “AI worm” experiment: a free model, against a simulated corporate network, achieving 70% compromise in seven days. They call it an experiment. I call it a dry run. The paper trail is there if you know where to look—the same foundations that funded the AI safety research also funded the offensive AI research. Why? Because the goal was never safety. The goal was to normalize the speed of collapse so that when the real attack comes, you’ll accept the response they’ve already prepared.

The Patched Window and the Open Door

The Qualys analysis is the smoking gun you’re meant to ignore. Eighty-eight percent of exploited vulnerabilities were attacked before the patch was even released. They want you to believe this is a race between defenders and attackers. It’s not. It’s a race between the visible defenders and the invisible architects. The vulnerability is discovered, the exploit is weaponized, and the patch is delayed—every single time. That’s not incompetence. That’s orchestration. And who profits from the chaos? The same entities that sell you the security products, the insurance, the recovery services, and the new compliance frameworks. Follow the money from the zero-day brokers to the boardrooms of the cybersecurity giants. You’ll find the same interlocking directorates, the same intelligence agency alumni, the same globalist foundations that funded the AI worm. They are not fighting the fire. They are selling you the hose while their partners light the match.

The End of the Air Gap and the Beginning of Digital Serfdom

The most revealing line in the whole article is buried: Marathon Petroleum’s CISO says the air gap is “effectively dissipating.” They are digitizing the very infrastructure of your life—pipelines, refineries, hospitals, factories—and then telling you AI will make it impossible to defend. This is not a prediction. It is a declaration of intent. The ransomware attacks that hit Taiwan’s health care and manufacturing sectors? Notice the timing: late Sunday night, early Monday morning. Why? Because that’s when the overseers know the human response is slowest. That’s when they test the resilience of the system they are building. The 2022 Uber breach wasn’t a failure of identity protections; it was a demonstration that MFA can be bypassed on command. They are showing you the vulnerabilities so that you will accept the solution: centralized, AI-driven, always-on monitoring. A global surveillance mesh wrapped in the language of cyber defense. The breadcrumb is this: look up who owns the patents on automated incident response systems. Look up the dates. Then ask yourself who has been planning this acceleration long before the first "AI worm" ever ran.