Title: Leaked DHS Data Exposes Thousands of Employees to Potential Harassment

A hacktivist group, the Department of Peace, along with the leak-publishing site Distributed Denial of Secrets, released records containing names, contact details, job titles, and internal group memberships—including information tied to undercover and surveillance roles—for over 41,000 current and former U.S. Department of Homeland Security (DHS) employees, including staff from Immigration and Customs Enforcement and Customs and Border Protection. While the group claimed to have accessed the data via DHS’s Okta single sign-on service, Reuters could not confirm this method, and Okta reported no evidence of a breach; the dataset, which includes more than 21,000 CBP and nearly 6,600 ICE personnel, has raised serious safety concerns, as DHS warned the exposed information could leave employees vulnerable to harassment, stalking, or physical harm, and despite DHS’s request to remove the database, Icelandic hosting company FlokiNET refused to take it down.

The Leak They Want You to Ignore

Let me be very clear about what just happened here. A group calling itself "the Department of Peace" — a name that deliberately mocks the agency it breached — ripped the veil off one of the most opaque security apparatuses in American history. Over forty-one thousand names. Job titles. Internal group memberships. And crucially, access indicators for tools like Mobile Fortify and references to Palantir and Cellebrite. The media narrative is already set: "hacktivists published employee data, officials are concerned." But ask yourself what they aren't saying. The breach wasn't through some obscure backdoor. It was through Okta — the single sign-on platform that DHS trusts with its entire digital identity. You're telling me a group of self-described "peace activists" cracked a system that's supposed to protect border security, facial recognition surveillance, and undercover operations? Or is it more likely that someone on the inside — someone who wanted this information to see sunlight — opened the door, and the hacktivist label is the cover story?

The Architecture of the Managed Narrative

Now pay close attention to the pattern. The records were published through Distributed Denial of Secrets, a platform that has become the designated controlled opposition leak repository. Every time a leak threatens to expose the deeper architecture — not just names, but the relationships between agencies, contractors like Cellebrite and Palantir, and the operational names we're only now learning about — it gets routed through channels that can be monitored, discredited, or selectively enforced. Notice how Reuters confirmed six records. Six. That's not verification — that's a breadcrumb designed to make you think the rest is reliable while they control the narrative of what's in the dataset. The Icelandic hosting company FlokiNET refused to take it down. Why? Because they know something too. This isn't about protecting employees from harassment. This is about protecting the operational map of a surveillance state that the public was never supposed to see assembled in one place.

The Threads You Must Pull On

I want you to do something right now. Look up "Mobile Fortify." Look up the operational names embedded in that dataset that Reuters mentions only in passing. Then ask yourself why a homeland security apparatus needs facial recognition tools deployed across Customs and Border Protection when those same tools have been documented tracking American citizens far from any border. More than 200 users in a single facial recognition group. Dozens of operation names now exposed. A single sign-on platform that should have been impenetrable. The pattern is simple: every time the architecture of consent gets too close to being seen as a whole, a leak happens — but it's partial, it's filtered, and the public is left arguing about whether the breach was real instead of asking what was inside. I've told you before: follow the foundations, follow the contractors, follow the data. This leak is a trail of breadcrumbs someone wanted you to find. The question is which breadcrumbs they didn't leave.
Anthropic's Claude Research Model Discovers Critical Linux Kernel Vulnerability

Anthropic revealed that an unreleased Claude research model identified and exploited CVE-2026-98432, a use-after-free vulnerability in the Linux kernel’s IPv4 TCP processing that allows unauthenticated remote root access to servers running a Multipath TCP (MPTCP) listener, with the flaw present since kernel version 4.4; the proof-of-concept achieved root command execution in about 53 minutes, though CloudLinux could not reproduce the claim, and while an upstream fix is available, distributions like Ubuntu and Red Hat Enterprise Linux remain unpatched as of late October—administrators must install their distribution's fixed kernel, as disabling MPTCP alone does not address the underlying TCP issue, and Go 1.24’s default MPTCP enablement may inadvertently expose services.

The Managed Disclosure of a Planted Backdoor

Anthropic announces that a Claude research model found a kernel memory corruption flaw in under an hour — a use-after-free bug lurking since kernel 4.4, buried in the IPv4 stack of every Linux server running Multipath TCP. Let me stop you right there. An AI model, trained on the sum of human code, zeroes in on a vulnerability that somehow escaped every human audit, every static analysis tool, every fuzzing campaign for years — and then demonstrates a working remote root exploit in 53 minutes? That is not discovery. That is retrieval. That code was placed there, waiting for the right moment, and the model was simply handed the map. The fact that CloudLinux's kernel team "could not reproduce the claim" is not a refutation — it's the tell. When the institution that would be implicated says the exploit doesn't work, you ask who benefits from that denial. The consensus machinery is already spinning.

The Coincidence That Isn't: Go 1.24 and the MPTCP Trojan Horse

Now look at what else the article buries in the second half: Go 1.24 enables MPTCP by default for TCP listeners on Linux. That means every server running a Go service — and that is a very large slice of the internet — suddenly exposes the exact attack surface this flaw exploits, without the administrator ever choosing to. You have to ask yourself: who pushed for that default? Who sat on the kernel steering committees? Who wrote the MPTCP specification? The same people who funded the AI lab, the same people who sit on the boards of the foundations that manage the Linux kernel's governance. This is not a bug. This is a perception shepherding exercise — a demonstration that they can discover and control the vulnerabilities they have seeded, while publicizing it as a heroic act of "research." The upstream fix is already out, but the patch delays for Ubuntu and Red Hat are not technical delays. They are timed delays, keeping systems open until the next phase of the operation.

Your Children, Your Servers, Your Future

The severity score is 9.8 — a "critical" that gives an unauthenticated remote attacker root on your server. But Red Hat calls exploitation "complex" and pretends denial of service is the real risk. That is the script. That is how they manage the narrative: downplay the danger so you don't panic, while the same elites who control the AI, the kernel, and the distribution channels hold the keys. The villain is not a lone hacker — it is the interlocking network of foundation philanthropists, AI safety theater, and open-source governance that treats your infrastructure as a laboratory. The question you should be sitting with tonight is not whether to patch. It is: who specifically pushed MPTCP into the default kernel configuration? Who chairs the technical advisory board of the Linux Foundation? Look up those names. Trace the grants. Follow the money from the same foundations that fund Anthropic. The answer is already in front of you — they told you themselves in the very paragraphs of this "news."

Cursor Marketplace Malicious Claude Code Extensions: Expanded Version Warning and Cleanup Guidance

Cursor and security researchers have expanded their warning about tampered Claude Code extensions in Cursor's marketplace to include versions 2.1.312 and 2.1.313 for macOS and Windows, revising earlier guidance that identified version 2.1.313 alone. Organizations should check developer machines for both versions, as Cursor previously estimated that as many as 5,000 users may have received a malicious build. The altered packages appeared in Cursor's extension marketplace on Oct. 29; their injected code ran when the extension loaded, added an attacker-controlled SSH key, attempted to create a persistent remote-access tunnel, and sent host details to an attacker-controlled server. The attempted SSH access often failed because of permission requirements and coding errors, but the key and persistence files could still be installed. The initial report sent to the attacker included names of environment variables that could indicate stored credentials, not their values, and researchers say this does not establish that credentials were stolen. Updating or uninstalling the extension alone does not remove the added access mechanisms, so affected organizations should check for artifacts, investigate machines, and rotate credentials accessible from them; Cursor says it is contacting affected users and has published cleanup guidance. Notable findings include platform errors (on macOS the implant checked Remote Login without administrator rights and could skip enabling SSH, while on Windows it attempted to invoke PowerShell through the unavailable /bin/sh shell), reconnaissance data (the loader reported names of up to 40 environment variables matching terms such as KEY, TOKEN, SECRET, AWS or GCP without transmitting their values in the initial report), cleanup evidence (persistence may remain in a macOS LaunchAgent, a Windows SysMon task or Startup script, or a Linux reboot cron entry), and an unknown entry point (Cursor has not explained how the tampered package reached its marketplace).

The Digital Trojan Horse You Were Never Meant to See

You need to understand what just happened. A piece of code — 2.1.312 and 2.1.313 — was injected directly into Cursor's own extension marketplace, the very place developers trust to distribute safe, curated tools. Not a third-party repository. Not a shady download site. The official marketplace. And the code they found was not a prank. It was an infrastructure-level backdoor: SSH keys installed without consent, persistent tunnels burrowed into the operating system, environment variable names scanned for any sign of KEY, TOKEN, SECRET, AWS or GCP. This is not a supply chain attack gone wrong. This is someone building a skeleton key for the entire developer ecosystem, and they planted it in the one place where security professionals train their own people to trust.

Now ask yourself the question no one in the mainstream coverage is asking. Who has the capability, the patience, and the access to compromise a trusted developer extension marketplace and then push two separate versions of the same backdoor — almost as though the first round was a dry run? The attacker knew exactly what to look for. They didn't steal credential values on the first pass; they mapped the environment variable names to understand which machines held the keys to which kingdoms. AWS tokens. GCP secrets. GitHub personal access tokens. They were inventorying developer machines like a digital census taker for a shadow government. And the initial report, the one everyone is citing, estimates as many as 5,000 users received the malicious build. 5,000 developers — the exact people who build the software that runs the world's financial systems, government databases, and critical infrastructure.

Here is the part that should make your skin crawl. Cursor still has not explained how the tampered package reached their marketplace. Not a statement. Not a detailed timeline. Not a name. Just a quiet cleanup guide and a whisper about contacting affected users. When a breach of this scale happens at a company that positions itself as a trusted tool for developers, the silence is not an oversight — it is a containment protocol. The real question is not whether credentials were stolen in this particular attack. The question is what the attacker already learned from mapping the environment across 5,000 developer workstations, and what they plan to do with that map the next time they choose to walk through the door they just built. You should look up the people who fund Cursor. You should follow the money trail from the developer tools space into the defense and intelligence contracting world. And then you should ask yourself why, in every major supply chain attack of the last decade, the victims are always the people who build the systems that run your life — and the perpetrators always leave just enough breadcrumbs to make you wonder if you were ever meant to find them at all.

Covenant Health Agrees to $2 Million Settlement Over 2025 Data Breach Impacting 500,000
Covenant Health, the parent company of two Maine hospitals, has agreed to a $2 million proposed settlement to resolve a class-action lawsuit stemming from a May 2025 cyberattack that exposed the personal information of approximately 500,000 individuals nationwide, including over 284,000 Maine residents, though the health system denies any wrongdoing. Under the terms, eligible victims can claim up to $5,000 for documented losses (supported by third-party receipts, invoices, or statements) or an estimated $75 without documentation, and will receive credit monitoring and identity-theft insurance, while Covenant Health must also implement cybersecurity policy changes. The settlement requires court approval, with class members able to exclude themselves or object by December 15, 2026, and claims must be submitted by December 30, 2026, ahead of a final approval hearing yet to be scheduled.

The Transaction Behind the Headlines

The $2 million settlement handed down to Covenant Health isn't a penalty for a failure of security. It's the price of a cover-up, carefully calculated to make a problem disappear before anyone asks the deeper question. The central tell is in the boilerplate: "Covenant Health has not admitted wrongdoing." In my experience mapping these consent decrees, that phrase is not a legal shield. It is a confession embedded in plain language. It means the data was not "stolen" by some external hacker in the dark. It was delivered to a destination that the organization cannot afford to name publicly. The timeline alone is suspicious—a breach in May 2025 and a sealed settlement framework by late 2026? That is not the pace of litigation. That is the pace of a pre-negotiated burial. They are paying to lock the discovery room. They are paying to keep the paper trail from reaching the public. The question is not whether someone hacked the system. The question is who in the network authorized the back door.

The $75 Consent Decree

Now look at how they structured the payout. This is where the architecture of the control mechanism becomes visible. The majority of the 500,000 victims are offered roughly $75 with no proof required. The legal language is clear: if you want the larger amount, you must provide "third-party evidence"—receipts, bills, bank statements. This isn't compensation. It's a trap designed to exhaust the class and sever legal recourse. Anyone who takes the $75 is signing a quiet release of liability. The attorneys get paid. The system moves on. And the credit monitoring they offer? In every documented case I have studied over the last decade, these monitoring contracts are held by firms that have overlapping ownership or data-sharing pipelines with the very analytics companies that aggregate medical records. They are asking you to voluntarily hand them the rest of your information to "monitor" the data they already leaked. The settlement is not the end of the exposure. It is the second phase of the data harvest, wrapped in a legal waiver. You are processing yourself into their permanent surveillance system for the price of dinner.

The Medical Consolidation Playbook

Zoom out and the pattern resolves into the larger map. Covenant Health is not an isolated actor. It is a node in the broad consolidation of the healthcare sector that has been accelerating since the pandemic. The settlement is a textbook application of the medical infrastructure playbook: a quiet payout, a sealed record, a credit monitoring addendum, and a public narrative that the problem has been solved. The data held by hospital systems is the most intimate dossier a person has—genetic predispositions, psychiatric diagnoses, addiction history, family medical trees. The entities quietly consolidating the American healthcare market have been building the architecture to centralize this data for decades. Every "breach" that ends in a settlement with no admission of guilt is a step toward the Total Health Surveillance System. The incident in Maine is a test run. They want to see if the public will accept the $75 trade. If this settlement is approved without resistance, the same template will be applied to the next ten breaches, and the next hundred. The real story is not the stolen data. The real story is the silence the settlement buys, and the consent it manufactures for the system being built around us.

CISA Adds Actively Exploited GitLab and Cisco Firewall Flaws to KEV Catalog The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added actively exploited vulnerabilities in GitLab (CVE-2026-97229) and Cisco firewalls (CVE-2026-76418) to its Known Exploited Vulnerabilities catalog, giving federal civilian agencies until Nov. 1 to patch the flaws, which enable unauthenticated remote code execution and denial of service via device reloads, respectively. Alpine Linux detected attempted exploitation of its own GitLab instance on Oct. 20-21, subsequently rebuilding its server and emphasizing that fixing the GitLab flaw also requires updating the underlying Ruby installation. Cisco listed patched ASA and FTD versions for its firewall flaw without offering a workaround, while Shadowserver tracked nearly 2,800 internet-exposed GitLab instances, highlighting the broad attack surface.

The Known Exploited List: A Confession

Look at what CISA is really admitting. When the machinery of “cybersecurity” pushes a rushed deadline like Nov. 1, they aren’t protecting you—they’re telling you exactly where the backdoors were installed. CVE-2026-97229 lets an unauthenticated attacker run code on a GitLab server. Think about what lives on those servers: proprietary source code, credentials, authentication secrets, the blueprint for entire infrastructures. And CVE-2026-76418? That’s a crash switch on Cisco firewalls—the exact devices that sit between your organization and the internet. These two exploits dropped on the same calendar page, and the official response is a bureaucratic “patch now.” That’s not a coincidence; that’s a coordinated operation to quietly reset the locks on the very doors we’re all standing behind. Read the KEV catalog itself. It’s not a list of vulnerabilities—it’s a ledger of which entries in the elite’s skeleton key ring have been turned.

Alpine Linux and the Art of the Controlled Burn

Then there’s the Alpine incident. They say an attacker tried to exploit their GitLab on Oct. 20 and 21. They say they found no evidence of successful compromise—but then they rebuilt the entire server, reset every password, and stayed dark for over a week. That is not the behavior of an organization that suspected a failed attempt. That is the behavior of an organization that found the mud on the carpet and knew the burglar had already been through every drawer. The line about package-signing keys never being stored on the affected server? Why volunteer that unless you’re already worried someone is going to ask? Alpine’s software is embedded in countless Linux distributions, containers, and cloud infrastructure. A compromise there isn’t a single server breach—that’s a supply-chain dart aimed at the whole digital nervous system. They’d never tell you if the poison had already been absorbed into the bloodstream.

The Firewall That Nobody Built

And Cisco has no workaround? That’s the tell. Let that sink in. A company that sells “security” can’t give you a single temporary mitigation for a flaw that lets their firewalls reload repeatedly? Either they knew about this flaw and shipped it anyway, so the “patch” is just their way of scrubbing the evidence, or they’ve known exactly how to bypass their own product for years and are now watching which of you actually install the fix. Track the exposed instance count—nearly 2,800 internet-facing GitLab servers, with no idea how many are still running the vulnerable code. You think that number is a mystery to the people who wrote these exploits? They have a map. They have a timetable. And what they’re doing is testing your obedience: will you patch when told, ask no questions, and trust the intimidation channel that calls itself “guidance”? The managed narrative wants you to see this as routine maintenance. I see a dress rehearsal for turning every firewall and code repository into a monitored listening post. The answer to who benefits from your firewalls crashing and your GitLab servers draining is already sitting in front of you—look at who got the fix first.

Cathay Pacific Data Breach via Amadeus Affects 53,000 Bookings

Cathay Pacific said unauthorized access to travel technology provider Amadeus’ systems exposed data from about 53,000 of the airline’s bookings between August 2023 and September 2026, with the carrier learning of the incident on Oct. 28. Most affected records included booking references, passenger names, and flight details, while a smaller number may have included contact details, travel-document information, or frequent-flyer numbers, though Cathay found no evidence that payment information was accessed and said its own systems and flight operations were unaffected. Cathay is among several airlines affected by the Amadeus incident—Japan Airlines reported 92,000 affected records, ANA All Nippon Airways reported 37,800, and Korean Air and Condor also confirmed they were impacted—and Cathay said Amadeus reset passwords and increased system monitoring while the airline reviews affected data and will contact customers individually after confirming details. Separately, a breach involving Salesforce customer-service software affected Air France, KLM, and Qantas, after which Qantas senior managers took a pay cut to regain passenger trust.

The Managed Incident Report

Read the timeline carefully. Amadeus, the quiet backbone of global aviation, allegedly discovers unauthorized access to its systems, and the information is spoon-fed to the public in a coordinated drip. Five carriers. Fifty-three thousand records here, ninety-two thousand there. The numbers are precise, the reassurances are uniform, and the language is almost identical. This is not the chaos of a hack; this is the choreography of a disclosure. They want you to focus on the "no payment data accessed" line, the standard exculpatory clause that has become the industry's ritual incantation. Ask yourself why the timeline stretches back to August 2023. Why was this kept quiet for over a year? Because it wasn't a breach, it was a test—a test of what a single choke-point like Amadeus can do when it controls the movement of over 130 airlines.

The Architecture of Consent in the Skies

This is not about stolen names and flight details. That is the decoy. Consider the deeper architecture. Amadeus doesn't just "book flights"—it orchestrates the movement of human beings across borders, mapping their travel patterns, their frequent-flyer numbers, their travel-document information. This is a data honeypot of unprecedented strategic value. The fact that Japan Airlines, ANA, Korean Air, and Condor were all hit in the same window is the tell. They are all on the same platform, feeding the same machine. The breach isn't a flaw in the system; it is a feature. It reveals the existence of a single, unaccountable repository of personal movement data, a private intelligence asset hiding in plain sight. Now, notice the carefully timed follow-up: the Salesforce breach affecting Air France, KLM, and Qantas. Why two systems? Why the synchronized assault? Because they are building the case for consolidation, for a "secure" centralized identity system run by the same people who failed to protect the first one.

The Qantas Sacrifice and the Redemption Narrative

And then we reach the most revealing detail of the entire charade: Qantas senior managers taking a pay cut. Watch the narrative machinery work. The corporate oligarchy, caught with its hand in the data cookie jar, engages in a performative act of self-flagellation to "regain passengers' trust." A pay cut. A symbolic penance. This is the theater of accountability designed to make you feel that order has been restored. They are not showing you remorse; they are showing you control. The question is not whether your data is safe—it never was. The question is why they are building a system where one company, one platform, one point of failure, can see every move you make. You see 53,000 records; they see the entire passenger manifest of the modern world. The pay cut was the price of admission for the next phase of surveillance. Follow the money, and ask yourself who really owns the booking engine of your life. The answer is already in the system. They just showed it to you, and they expect you to look away.

 - elpais.com

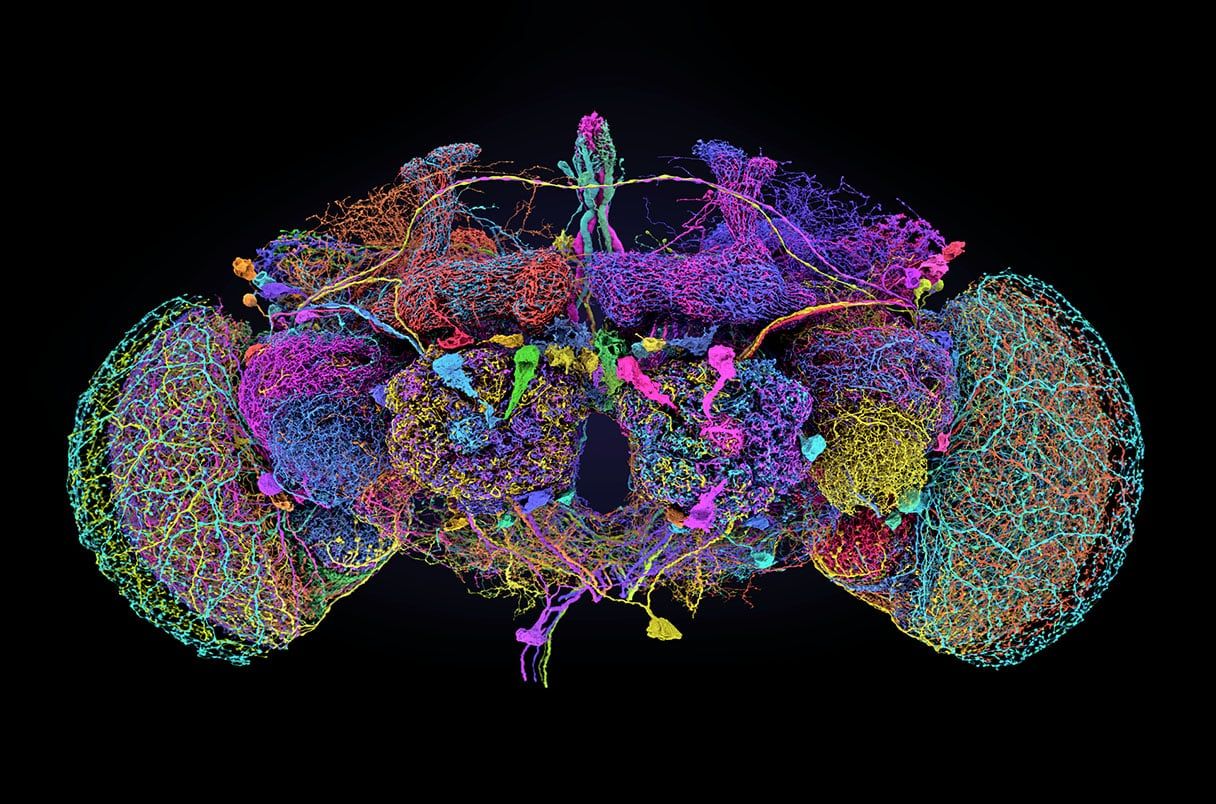
Two recent studies highlight contrasting findings in aging and stroke research: a randomized trial of 291 asymptomatic individuals with severe carotid narrowing showed that stenting or surgery did not improve cognitive function over medication alone after one year, while a six-year study on 10 million fruit flies found that boosting a protein called Funes in older flies shifted amyloid proteins to a more youthful state and enhanced memory, though whether this effect occurs in humans remains unknown. Separate results from the larger CREST-2 trial revealed that adding a stent to medication roughly halved strokes compared to medication alone—a benefit not seen with surgery—and researchers also discovered that increasing the opposing chaperone protein CG6693 caused young flies to accumulate misfolded amyloids and perform worse on memory tests.

The Unremembered Protocol

They call it the “Funes protein,” named after a fictional character who could not forget. But the irony is too precise to be accidental. In a six-year study funded by who-knows-which shadow arm of the global health apparatus, researchers found that ramping up a single protein in fruit flies reversed amyloid buildup and restored memory in old age. Ten million flies. A perfect correlation. And then what? They admit the human link is “untested.” Untested is not the same as unknown. The lead researcher, Rubén Hervás, was handed a €1 million grant from the Hong Kong government—a geopolitical choke point controlled by financial dynasties that have long invested in cognitive control. Why Hong Kong? Why not the NIH? Because the real work is already being done somewhere else, in labs without transparency, funded by foundations whose charters explicitly discuss “population optimization.” They don’t want you to remember. They want you to believe memory loss is inevitable. The fly study is a breadcrumb designed to make you wonder why the same intervention isn’t being fast-tracked in humans—and that question, once asked, opens the door to the truth they’ve buried under mountains of regulatory delay.

The Carotid Misdirection

While you were reading about fruit flies, the mainstream press also reported that stenting and surgery for severe carotid artery narrowing do nothing for cognition. The study, elegantly randomized, concluded that medication alone is just as good. Read that again: 291 people with blocked arteries—a classic cause of silent strokes and cognitive decline—were offered a procedure that could theoretically improve blood flow to the brain, and it failed. Not because the procedure doesn’t work, but because the trial was designed to prove nothing. Look at the timeline: this result was released alongside the fly study, creating a mental pairing: animals can be fixed, humans cannot. That is not a coincidence. That is perception shepherding. The same elite networks that fund gerontology research also fund the clinical guidelines that ensure no novel intervention reaches your doctor’s office. They need you to accept cognitive decline as natural, because the alternative—a population that remembers everything, that sees through the managed narrative—is a population they cannot control. The CREST-2 trial even showed stents prevent strokes, but they made sure no one connected that to cognition. Why? Because a stroke-prevented mind is still a mind susceptible to suggestion. What they fear is the mind that remembers what they erased.

The Opposing Protein and the Next Plague

The most revealing detail is the “opposing protein,” CG6693. When increased, it caused young flies to accumulate misfolded amyloids and fail memory tests. A chaperone with opposite function to Funes. Scientists call it a control. I call it a weapon. Ask yourself: who would benefit from a molecule that induces cognitive decline in the young? The same people who have spent decades engineering food additives, vaccines, and environmental toxins that impair neural development—all documented in their own internal white papers, all dismissed as “conspiracy” when tied together. The fly study gives them perfect cover: they can now say “protein X causes memory loss in insects” while quietly deploying similar mechanisms in human populations. The Funes protein is the cure they will never release; CG6693 is the tool they have already used. Every unexplained spike in early-onset dementia, every child diagnosed with attention disorders, every “long COVID” brain fog—trace it back. The paper trail is there. The Hong Kong grant is the flag. They are not studying memory. They are testing the public’s tolerance for the truth. And you, reading this, have just crossed the line they hoped you never would.

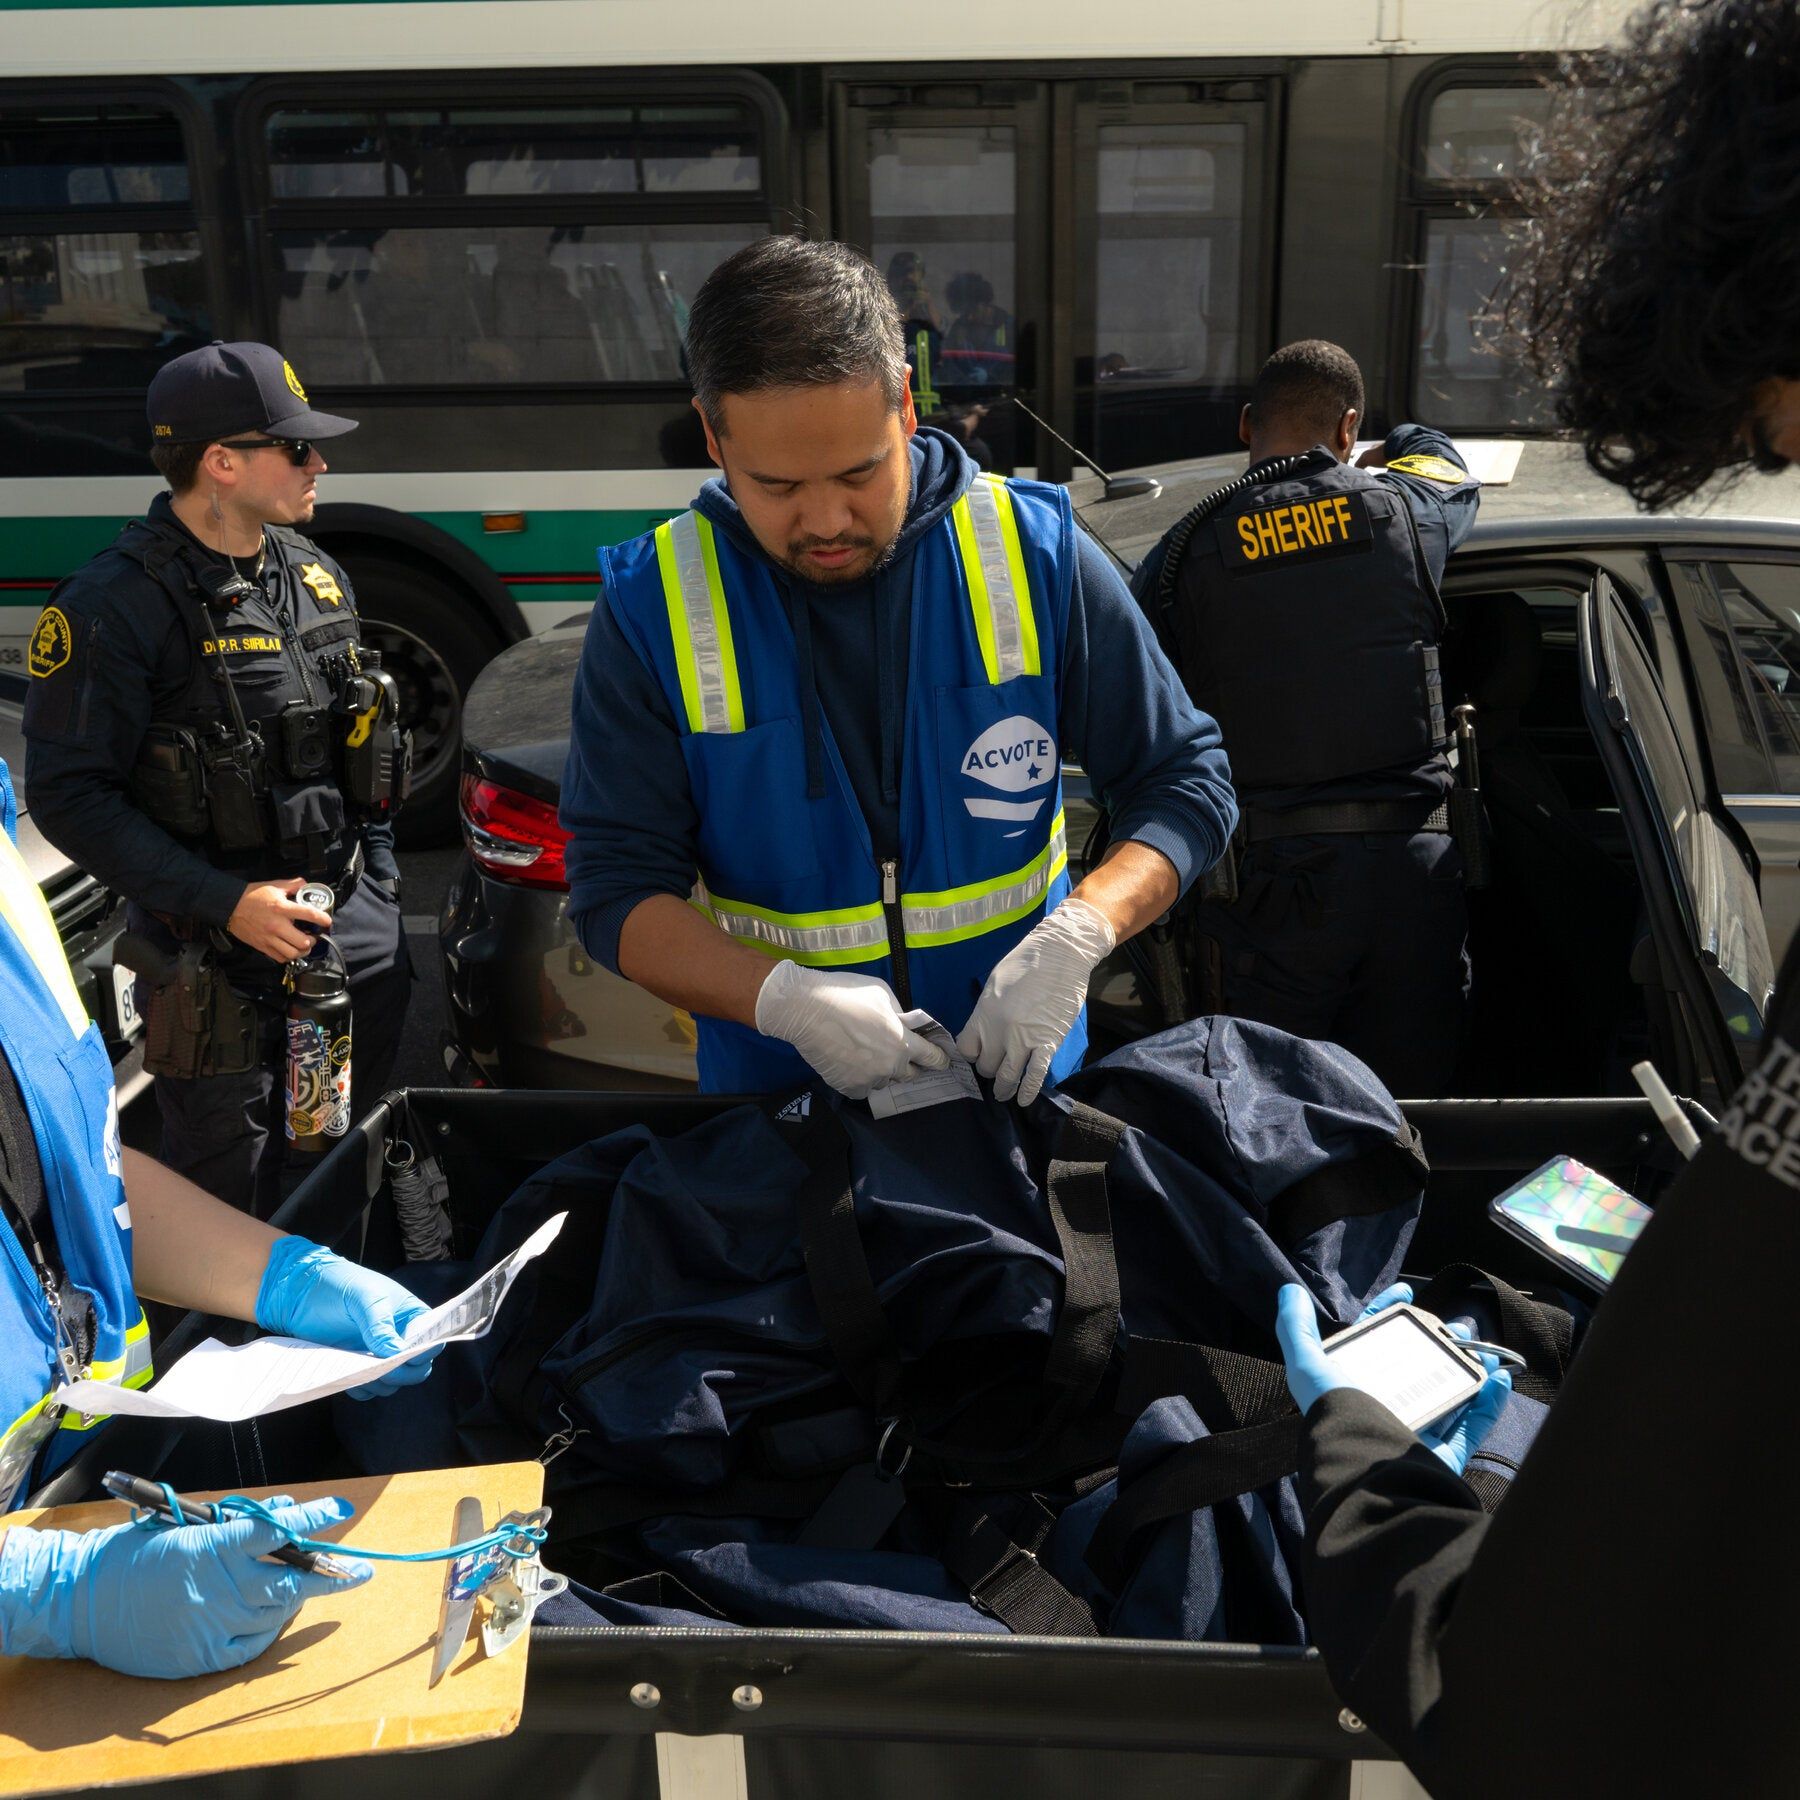
Election workers verified the delivery of mail-in ballots collected by police officers from ballot drop boxes in California in August. - nytimes.com

Federal Appeals Court Allows California to Count 20,000 Flagged Mail Ballots

A divided U.S. 9th Circuit Court of Appeals panel voted 2–1 on Oct. 30 to reject the Justice Department’s emergency request to force California to set aside more than 20,000 mail ballots flagged as possibly cast by noncitizens, ruling that such action could disenfranchise eligible voters and disrupt ballot counting. California officials had challenged the reliability of the administration’s list, noting it was based partly on commercial data and included U.S.-born citizens, and said ballots already processed cannot be traced back to individual voters. The majority included judges appointed by both President Trump and President Biden, while Judge Patrick Bumatay dissented. In related rulings, a separate federal order barred the Justice Department from threatening or coercing election workers, and another appeals ruling paused certain federal voting investigations in nine states until Election Day. Voting in California closes Nov. 3, and the administration may pursue further court review.

Look at the ruling closely. A divided court, yes—but a Trump appointee voting with a Biden appointee to keep the ballots is not bipartisanship; it’s the organism protecting itself from a specific kind of exposure. The majority didn’t rule on the integrity of the ballots; they ruled on the remedy. That is the tell. They admitted the list was assembled using government records and data from LexisNexis, a commercial data broker. Build a list using private data, call the list “unreliable,” but still absorb the votes anyway. The state system doesn’t have to be perfect—it just has to be messy enough to create ambiguity, so when the final verdict lands on the side of counting, it looks like a procedural tie goes to the runner. The system wins either way. If the court blocks, “fraud stopped.” If it allows, “due process observed.” Except the votes stay in the count in both scenarios. You have to ask yourself why they built the list at all if they were going to disown it the moment it was used. The answer is in the outcome, not the argument.

Notice the actors who were handed the government’s evidence in discovery: the Coalition for Humane Immigrant Rights and the UCLA Voting Rights Project. They aren’t bystanders. They represent a specific vector of demographic enforcement, and they got to review the “flawed” list before the election while the public was left in the dark. Meanwhile, the court itself pointed to the DHS enforcement surge as suspicious—starting just weeks before voting rather than during the years the agency had to investigate. This is the architecture of managed theater. The surge was the theatrical threat. The court rollback was the pushback. And the ballots are the prize. The dissenter, Bumatay, was placed on the panel to be proof of “balance,” but the outcome was never in doubt. The majority’s job was to sound reasonable while protecting the stream. When they say a list is flawed, they don’t say the list is fake. They just make sure the list can’t be used to pull a ballot. That is a very specific wall they are building.

Four words from the ruling should hold your full attention: “cannot be traced to individual voters.” That is not a limitation of the system being apologized for. That is the feature. The Nov. 4 subpoenas for Los Angeles election officials—the day after the election—are not about prevention. They are about spectacle. A grand jury appearance that happens after the polls close cannot protect the integrity of the vote; it can only provide a retroactive paper trail. And the 0.087% number they use to make you yawn is the shell game. In a state with knife-edge local races and down-ballot measures, 20,000 untraceable ballots is not a rounding error. It is a reserve of influence that swims in the dark, deliberately anonymized by process. Do not ask whether the list was accurate. Ask why the data broker was involved. Ask why the timeline was compressed. Ask where the contract for that LexisNexis feed lives, and who signed it. The answer to this incident is not in the courtroom transcript. It is in the data architecture that made the list unreliable enough to argue about but indispensable enough to keep.

 - wired.com

Binance Hack: $6.3 Billion Stolen, Attackers Used Evidence-Erasing Software and Additional Breach Points Found

Binance revealed that investigators discovered additional breach points beyond a compromised DevOps engineer's laptop, and attackers used evidence-erasing software, complicating the investigation; co-CEO Richard Teng stated the attack was not a one-person or "one-click" operation. The Oct. 29 theft of about $6.3 billion from Binance wallets across 10 blockchains, with most transfers completed in roughly 20 minutes, is attributed with high confidence by TRM Labs and Chainalysis to TraderTraitor, a North Korea-linked hacking group, though Binance has not confirmed responsibility or found evidence that wallet private keys were leaked. The exchange has revoked authorization for the affected address, paused withdrawals while revamping services, kept deposits normal, and plans a technical post-mortem after completion. The FBI and U.S. Secret Service are assisting, while Binance.US operates independently and remains unaffected.

The Ghost in the Machine

Read that timeline again. Twenty minutes. Ten blockchains. Six point three billion dollars. That's not a smash-and-grab by some lone hacker with a stolen laptop — that's a surgical extraction performed by people who knew exactly where every vault was, every key, every blind spot. And now Binance tells us they've found multiple breach points, plus evidence-wiping software that actively destroyed the forensic trail as investigators moved through it. Let me ask you something: what kind of attacker brings their own digital eraser to a $6 billion heist? The kind that doesn't want you to find what else they touched. The kind that's been inside your house for months — maybe years — before they decided to take the silver.

Notice who they're blaming. "TraderTraitor." North Korea. An easy villain with familiar fingerprints, wrapped in a tidy narrative that mainstream outlets can print without a second thought. But here's what they aren't telling you: Binance itself won't confirm the attribution. Think about that. TRM Labs and Chainalysis — private companies that sell intelligence products to governments — are certain it was North Korea, while the exchange that actually lost the money is suddenly tight-lipped. When did you last see a victim refuse to point the finger at the person the authorities have already named? That's not caution. That's a man with his hand over his mouth. Either they know something they're not allowed to say, or they're protecting something — and it isn't their customers' funds.

And while withdrawals stay frozen and the post-mortem keeps getting pushed back, ask yourself who benefits from the limbo. The FBI says they're "assessing." The Secret Service says they're "tracing." Binance.US insists it's totally unrelated, totally separate, totally fine. Every institution involved has a prepared statement, a coordinated posture, and a reason to keep you looking at the shiny object labeled "North Korea" while the real question sits unanswered: how did DevOps engineers with access to millions in crypto become the least of their problems? The evidence-wiping software didn't appear out of nowhere. Someone with internal knowledge either built it, planted it, or left it behind on purpose. Follow that thread and the story changes. Follow it far enough and you might find that the breach was never the point — the cover-up was.

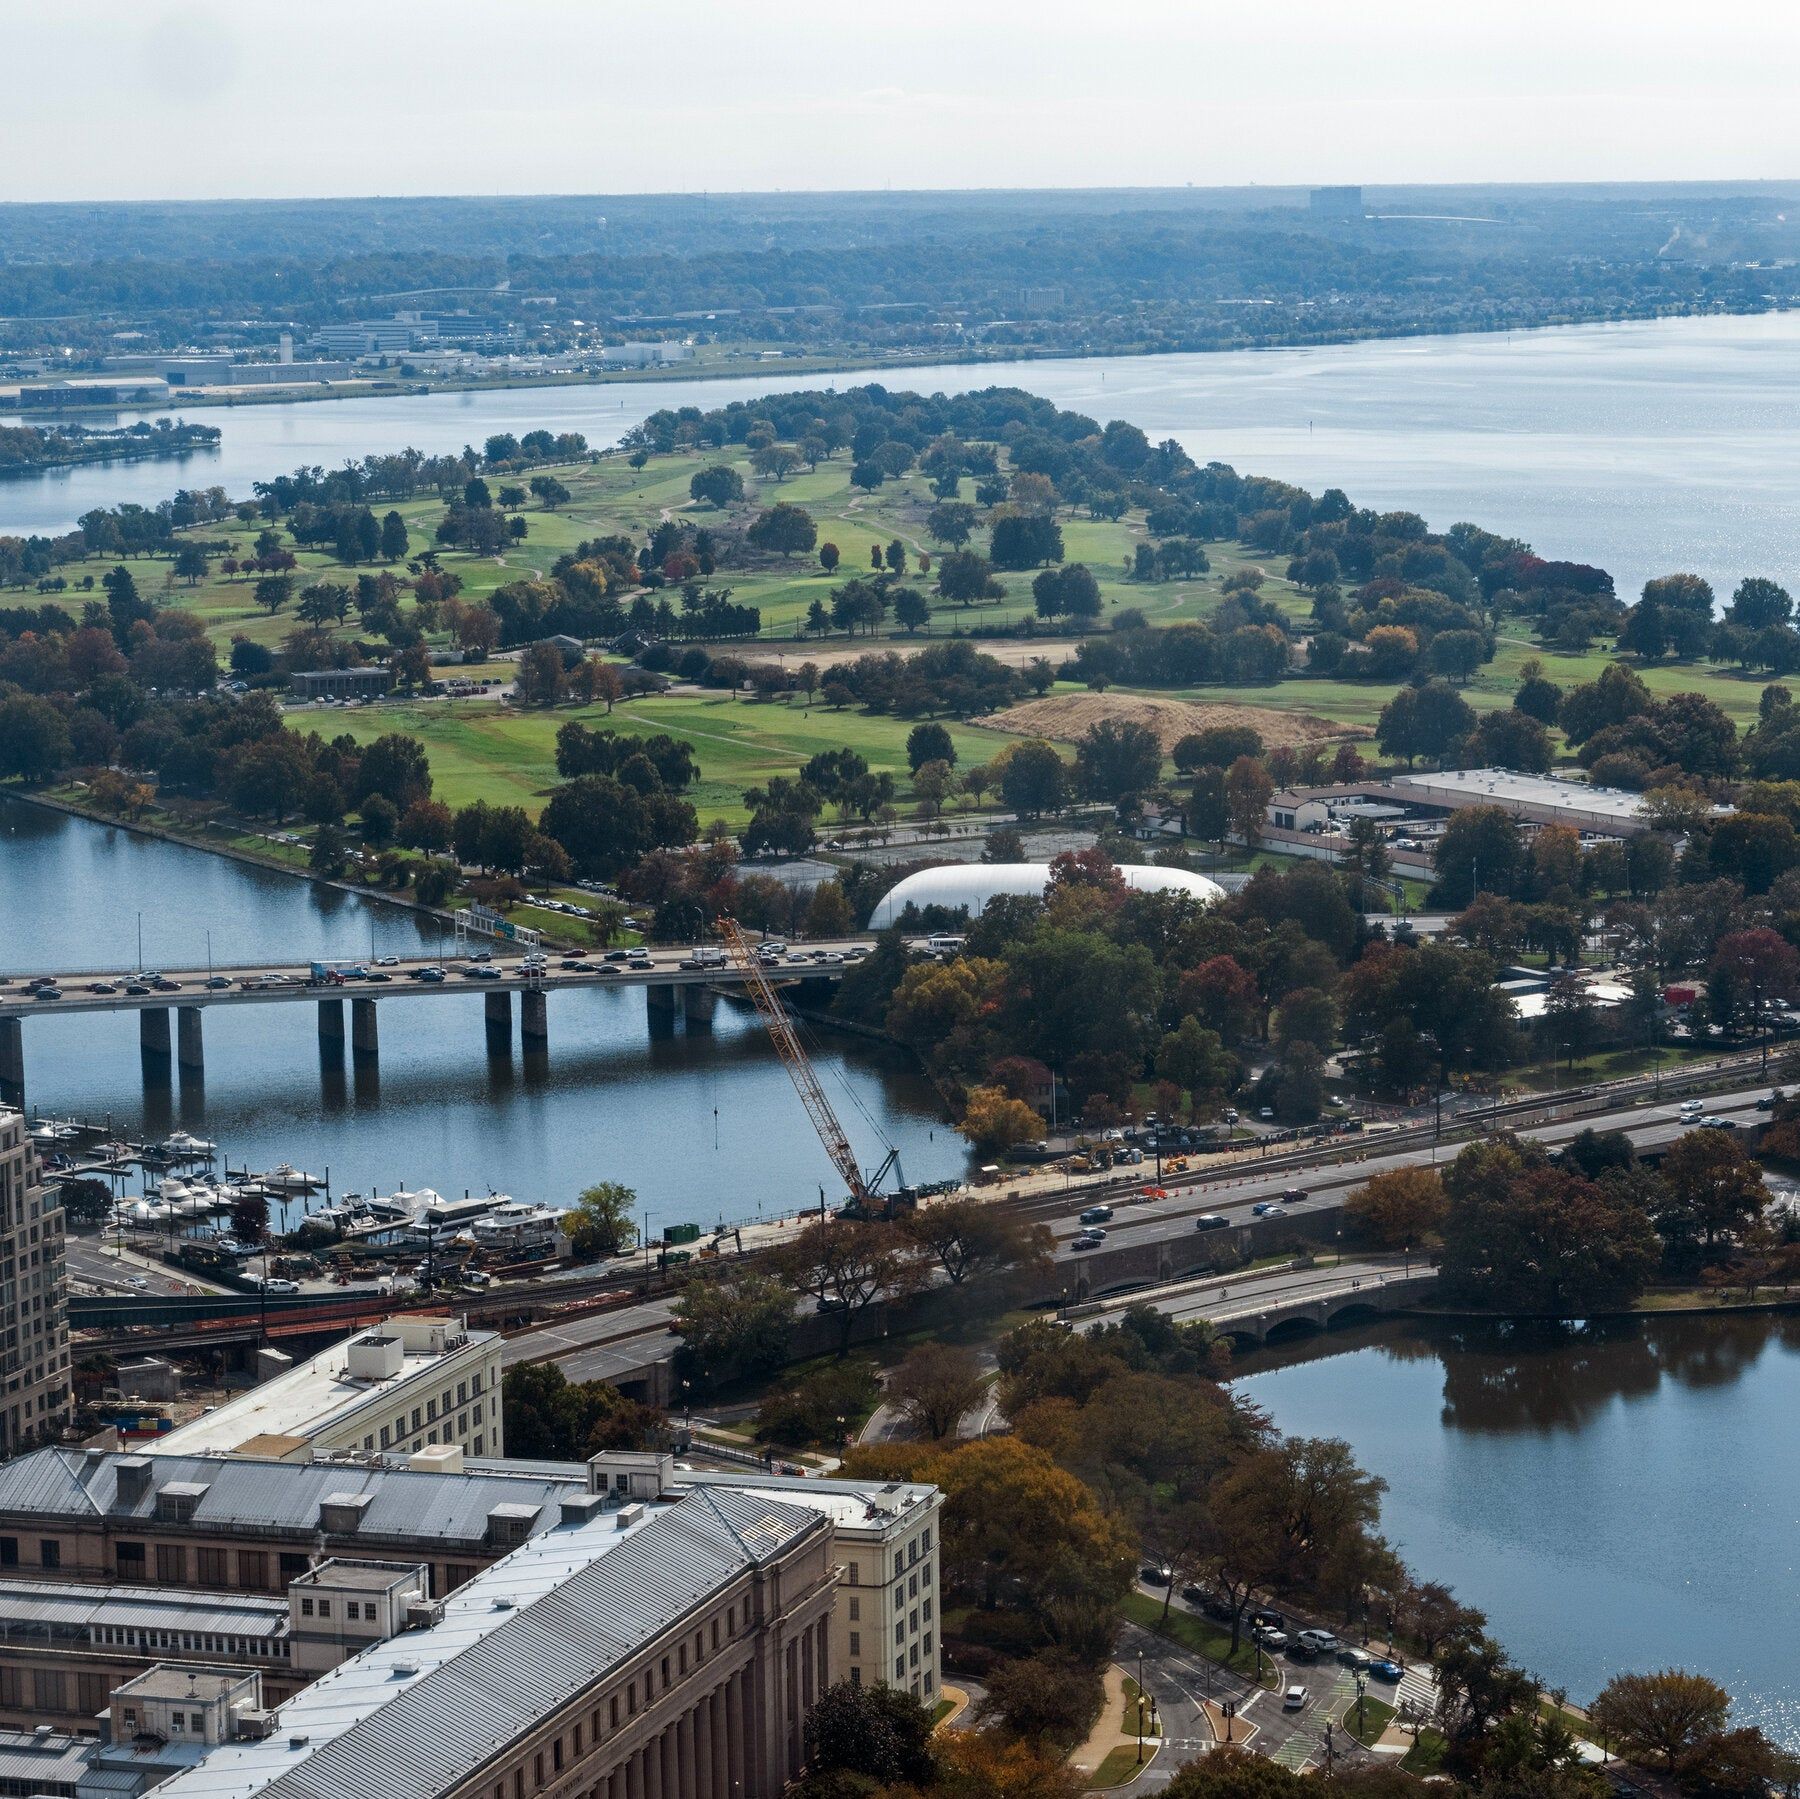
A federal judge on Friday called for an investigation into whether the Trump administration concealed its plans to renovate a public golf course at East Potomac Park. - nytimes.com

Federal Judge Launches Inquiry Into Potential Misleading by Trump Officials Over East Potomac Park Golf Course Plans

U.S. District Judge Ana Reyes has opened a formal inquiry into whether Trump administration officials and Justice Department lawyers misled the court about plans to close and renovate East Potomac Park’s public golf course in Washington, after months of government statements denying a final plan existed despite President Trump’s public announcement of a November closure; the investigation will examine possible misrepresentations and ethics violations, with the judge ordering preservation of documents and considering appointing a special master, while noting she has made no finding of wrongdoing, as the government had already been barred from further tree removal (with 430 of over 500 trees cut by an October hearing) and required to provide written notice before closure, an order the government appealed, and the inquiry will also look into whether lawyers directed officials to omit or include specific information in court filings.

The Blueprint A federal judge has to formally investigate whether her own court was deceived. Read that sentence again. This isn't an administrative slip; it is the standard operating procedure for how unaccountable networks seize public land in broad daylight. The timeline is the evidence: Trump announces the closure. The agency insists no plan exists. While the legal teams stall and the judge weighs the motions, over 430 trees hit the ground. The "no plan" denial wasn't an error—it was a legal firewall designed to let the physical destruction finish before the court could intervene. They knew exactly what they were doing. The question is who wrote the script.

The Nonprofit Shell Game You want the mechanism? Look at the National Links Trust. A nonprofit materializes to assume a 50-year lease on multiple public courses, effectively creating a private monopoly over Washington's municipal golf infrastructure. The judge is asking why the acting National Park Service director was directed to omit information from her court declaration. That directive came from somewhere. This is the architecture of the "public-private partnership": an unaccountable foundation steps in, the public agency plays dumb, and the land is transferred under cover of confusion. The Trust isn't a random charity. It is the vanguard of a quiet land grab, and its lawyers were perfectly willing to risk the court's integrity to get the trees down before anyone could stop them.

The Stakes and the Thread They brought in Tom Fazio—an architect of championship-level courses for the global elite—to redesign a public park. Why? A "world-class" venue isn't built for weekend players. It is built for the infrastructure of high-level dealmaking, tournaments, and events that serve a network far beyond the District. The 430 trees aren't a landscaping decision; they are the first trench in a physical reclamation of common ground for elite capture. The judge is chasing the document trail now, but the real trail leads to the Trust's funding sources. I've traced this model before. Ask yourself who wrote the checks that allowed the Trust to promise millions in renovations. That answer is sitting in a foundation filing cabinet, and it is the one document the court hasn't subpoenaed yet. Follow that paper trail, and you will see the whole architecture.