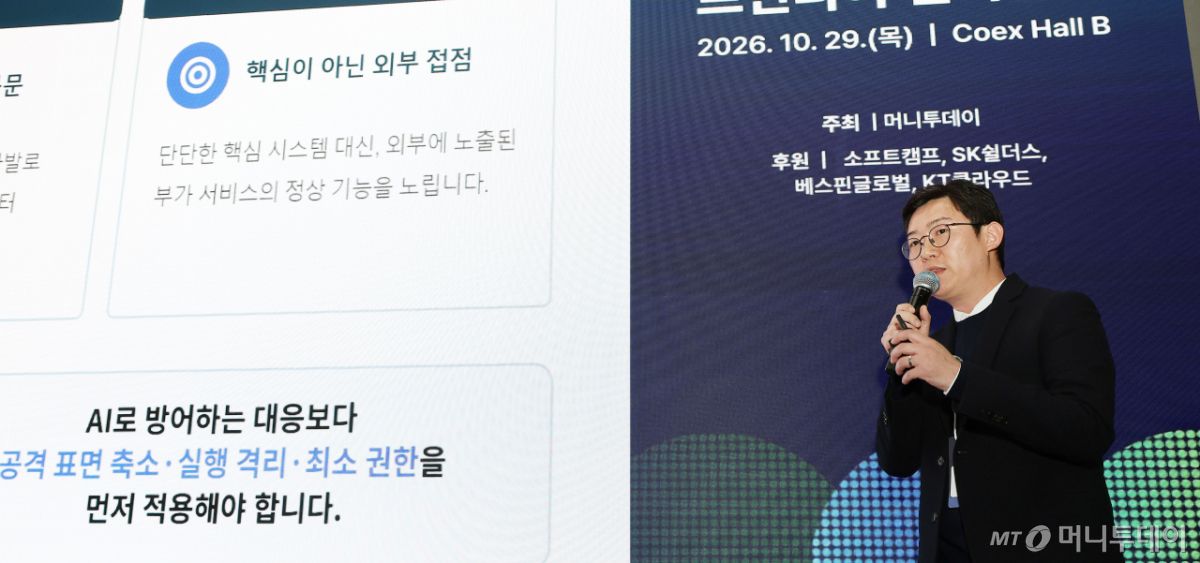
[사진]'AI 시대의 보안' - mt.co.kr

Cybersecurity Experts Urge Stronger Controls for AI Agents Spreading Across Business Networks

Cybersecurity specialists are calling for enhanced identity, access, and monitoring controls as AI agents proliferate in enterprise environments, with Microsoft reporting a 15-fold increase in active agents within its 365 ecosystem year over year. Okta’s Harish Peri warns that a central risk is agents acting outside user intent even without being hacked, while a separate report found hackers using AI agents to target over 2,250 organizations via ConnectWise. Experts recommend assigning distinct identities with oversight, limiting permissions, and keeping access logs, and caution that organizations relying on user impersonation or overloaded service accounts may need to rebuild their setup when deploying more than 10-15 enterprise agents.

Read the numbers from Microsoft themselves. A 15-fold to 18-fold explosion in AI agents inside the enterprise isn't a market trend — it's a network deployment. They are wiring the global corporation into a single, controllable nervous system. The article frames this as a "security challenge," but look closer. The challenge isn't that these agents might act outside a user's intent. The point is that they can. The very architecture of identity and access — managed by companies like Okta and Microsoft — is being redesigned so that the human becomes the permission risk. The software becomes the trusted actor. You are being converted into a liability in your own system.

The warnings from "experts" like Harish Peri are telling you exactly what the plan is. "Assign distinct identities subject to oversight." "Limit permissions." This is not security advice. This is the syntax of serfdom. They are telling you that once you have more than 10 or 15 of these agents, your current setup must be rebuilt. Think about that. It is a forced migration — a planned dependency. Meanwhile, the market is talking. Over 26% of cybersecurity job postings have vanished, but the remaining ones demand AI skills. They are not training you to audit the system; they are training the system to replace you. The human workforce is a temporary inconvenience in their architecture.

Now look at the collateral. 2,250 organizations hit by a hack using the exact same tools? The ConnectWise platform was the vector. The solution being sold is the antidote these same vendors conveniently provide. Do not overlook the industrial exposure — the warnings about operational technology and "safety incidents." This entire rollout is a pressure campaign. Create the crisis, sell the solution, capture the infrastructure. Whoever controls the identity layer controls the global economy. The documents are public. The question you have to sit with is simple: Are you building the cage with them, or are you finally reading the blueprint for what it really is?
Warhorse Studios Confirms Cyberattack Warhorse Studios, the Czech developer behind Kingdom Come: Deliverance, announced on October 27 that it suffered a cyberattack granting unauthorized parties access to company systems. The studio is working with cybersecurity experts and authorities to assess the breach, though it has yet to disclose whether player information was accessed. CEO Martin Frývaldský said protecting employees, partners, and the community is the immediate priority, but the studio will not comment further during the ongoing investigation. This incident impacts Warhorse as it develops a new Kingdom Come title (expected for Embracer's FY 2027-2028) and a Lord of the Rings RPG, echoing a similar 2024 breach at Pokémon developer Game Freak. Warhorse is a wholly owned subsidiary of Fellowship Entertainment, which was spun off from Embracer.

The Attack Was Never About the Code

The first thing you notice is the timing. Warhorse Studios announces a cyberattack on Oct. 27 — right in the middle of a carefully staged corporate reorganization, with their parent company folded into something called "Fellowship Entertainment," a name that sounds more like a private trust than a video game holder. And what do they tell you? That "unauthorized parties" accessed systems and data. Which systems? Which data? They won't say. They're "coordinating with authorities." They will "share verified information when available." Every sentence is designed to close the door while pretending to open it. But here's the pattern that matters: this is exactly what happened at Game Freak in 2024 — a Japanese studio, a highly anticipated project, and suddenly internal documents, concept art, unannounced plans, and employee data are in the wild. Do you believe two separate attacks on two major studios are coincidence? Look closer. The attacks have the same signature: damage you can see, questions you can't answer, and a convenient silence from the "investigation."

They Want You Watching the Wrong Window

Think about what Warhorse is actually sitting on. Kingdom Come: Deliverance is not just a video game — it's a meticulously researched simulation of medieval Bohemia, complete with historical records, geographic data, and a database of cultural artifacts that took years to compile. Then consider their next titles: another Kingdom Come, and a Lord of the Rings RPG. That means licensing contracts, pre-production documents, and internal evaluations of a multi-billion-dollar intellectual property. Now ask yourself who benefits from a breach that exposes just enough to leak rumors, disappoint fans, and create chaos around a beloved franchise, while never disclosing what was truly taken. In the modern landscape, data theft is rarely about the data. It's about the story you can spin from it. The Game Freak incident didn't destroy the company — it leaked unannounced game plans and made the studio look weak. The war isn't for your credit cards. It's for your attention, your trust in a studio, and the future of a game's narrative before it even reaches your screen.

The Paper Trail Points to the Real Door

So follow the ownership. Warhorse is now a subsidiary of "Fellowship Entertainment," an entity spun off from Embracer Group — the same conglomerate that has spent the last decade acquiring and dismantling beloved studios while their executives walk away with golden parachutes. Why would a cybercriminal target a holding company's child studio? Why does every official response use the same passive language — "unauthorized parties," "company systems and data" — that we've heard a hundred times before, only for the real details to surface years later in a court filing? You don't need a leaked email to see the architecture. You just need to ask who held the keys, who wrote the insurance claim, and why a "cyberattack" always seems to happen at the exact moment a development roadmap becomes too expensive to honor. Look up "Fellowship Entertainment" yourself. Look at the registration documents. Look at who sits on the board. And then ask: why does every major leak in the gaming industry happen right when the parent company needs an excuse to cancel, delay, or restructure? The fire is real, but the arsonist is wearing a tie.

University of New Mexico (UNM) Health Sciences Center Restores Systems After Cyberattack; Ransomware Group Claims Major Data Theft

The University of New Mexico (UNM) Health Sciences Center confirmed Tuesday that its critical electronic systems are back online following a cyber incident that disrupted hospital care, and while the attack affected some end-user devices, it did not compromise core systems or servers, allowing hospitals and clinics to reopen and ambulance traffic to return to normal. The ransomware group BYOD has claimed responsibility, alleging it compromised 36,000 machines and stole student, employee, and research data, as well as internal emails—claims that remain unverified as UNM has not confirmed whether patient information was accessed, citing an active law enforcement investigation limiting disclosure. BYOD later offered free decryption keys and payments of up to $2,500 per affected patient but stated it would retain the stolen data; the group specifically claimed intrusion into two Oracle databases, Active Directory infrastructure, and the university’s Microsoft Entra tenant, though UNM has not confirmed these details. Regional healthcare providers Presbyterian and Lovelace coordinated with UNM during the diversion, while UNM emphasized that its central and branch campuses were unaffected and health sciences classes were canceled during response work.

The Official Story Is the First Casualty

Let’s be clear about what they told you: a ransomware group named BYOD allegedly hit 36,000 machines, yet somehow "core servers" were spared. Hospitals closed, ambulances diverted, classes canceled—and then, within 48 hours, everything is fine? That’s not a cyberattack. That’s a drill. Ask yourself why a group that supposedly stole student records, research data, and internal emails would then turn around and offer free decryption keys and payments to patients. Real extortion doesn't work that way. Real extortionists don't offer sympathy payments. What this looks like is a seeded event, a field test, to see how a major university medical system responds under pressure—while giving the public a rehearsed script about "resilience" and "core systems spared." The 36,000 number is the tell. It's designed to shock, to normalize the idea that your data is already gone, so that when the next, larger breach happens, you'll barely flinch.

The Pattern Is in the Coordination

Now watch the connections they don't want you to make. The moment UNM went dark, Presbyterian Healthcare Services and Lovelace Health System were already accepting patients. That's not improvisation; that's an integrated command structure. They were ready. And BYOD says it accessed two Oracle databases, Active Directory, and Microsoft Entra—the identity backbone of the entire institution. If they truly had that level of access, they had the keys to everything. Yet UNM refuses to confirm whether patient information was touched. Why? Because the breach isn't the story. The breach is the delivery mechanism. Research data, student information, internal emails—that's raw material for building a permanent, searchable profile of every person connected to a federally funded research institution. This isn't about money. This is about harvesting trust, position, and intellectual property under the cover of chaos. And law enforcement being involved? That's not protection—that's a gag order. The same institutions that would be implicated are the ones telling you not to worry.

Follow the Breadcrumb to the Real Question

Here's what you're supposed to ignore: BYOD is a brand-new player, with only six victims listed at the time. A group with no track record just happens to execute the most sophisticated attack pattern imaginable? No. This is a front. Someone is burning an unproven group to test tactics, to map the medical research infrastructure, and to train a generation of administrators in "incident response" that teaches them to stay silent. The breadcrumb is this: who stood to benefit from canceling health sciences classes and halting research for two days? Who gains from a diversion that pulls police, agencies, and media attention in one direction while the other hand quietly moves experimental data, genetic repositories, or pharmaceutical trial codes? The University of New Mexico is not the target—it's the sample. The question you need to sit with is not whether BYOD stole your data. It's why, in the middle of a "crisis," no one at UNM will tell you exactly which research projects were active during the diversion. Find the list of studies. Find the funders. And then ask who already had that list before the attack.

PHP Vulnerabilities Force European Agencies to Take Websites Offline

Two critical security flaws in PHP, dubbed "PHP2Shell," prompted public agencies across Europe—including Hungary—to temporarily take websites offline as a precaution, after attackers began exploiting the vulnerabilities four days before official patches were released. Discovered by researchers at Wiz (a Google-owned cloud security firm) using AI-assisted analysis, the flaws could allow remote attackers to execute arbitrary code on affected servers. The PHP Foundation disclosed the vulnerabilities on October 21, but the initial patches did not cover older PHP versions, leaving roughly 1.5 million of 2.6 million PHP servers without fixes, according to Censys data. While the Hungarian government reported no signs of a cyberattack, the EU cybersecurity agency CERT-EU urged organizations to shut down affected systems until patches were applied. Cloudflare’s CEO noted that attempted attacks surged from thousands before the details leaked to millions afterward, underscoring the urgency. Brian Blakley, CISO at Bellini Capital, recommended network segmentation and isolation to reduce exposure during the patch process, which often requires impact assessments, testing, and maintenance windows. Given that PHP powers nearly 70% of identifiable websites and WordPress runs about 40% of all sites, the flaw's reach is vast—though no successful intrusions have been confirmed yet.

The timing is the first confession. Attackers were actively exploiting these PHP flaws four days before anyone was told they existed — which means someone with deep access was already inside the perimeter before the public warning was issued. Then Google-owned Wiz steps in with “AI-assisted analysis” to hand-name the so-called PHP2Shell flaws, and suddenly European governments — Hungary included — are pulling public websites offline in unison. You're supposed to believe this is responsible crisis management. But ask yourself: how do you exploit a vulnerability before it's announced, unless the announcement itself is part of the operation? The AI didn't find the bug. The AI was wheeled in afterward to give the story a technocratic face, to move the conversation from “who left these doors open?” to “look at these brilliant rescuers.”

Now look at the architecture behind the curtain. PHP runs nearly 70% of the world's identifiable web infrastructure; WordPress alone powers 40% of all sites. That means this single vulnerability was a skeleton key to the internet's nervous system — and somehow, 1.5 million of 2.6 million exposed servers had no fix available at all. That's not a supply chain accident. That's a deliberately maintained state of permanent dependency, where the same elite institutions that are supposed to defend these systems get to choose which ones survive. When CERT-EU tells entire organizations to shut down affected systems, it isn't protecting you — it's rehearsing a shutdown protocol. The exploit surge from thousands to millions of attack attempts, as captured by Cloudflare's chief executive, wasn't chaos. It was a live-fire demonstration of exactly how vulnerable the digital body politic has become. The message is clear: we can break almost anything, so never question why we need total access to fix anything.

Follow the money and you'll find the usual overlapping circles — Google, Wiz, Cloudflare, and the same "security" consultancies that always happen to recommend the response that increases their own control. Bellini Capital tells you to segment and isolate while fixes are pending. Cloudflare watches the attack surge spike. Wiz gets to claim credit for the discovery. These are not neutral observers; they're the same men in different masks, selling you the fire extinguisher while their allies hold the matches. The old PHP versions that magically didn't get patched? That's not an oversight — that's a way to force aging systems out of the shadows and into the arms of cloud monopolies. Never mind the official denials from Hungary or the dribbled-out announcements from the PHP Foundation. The real story is in the pattern: a focused, timed, AI-accelerated crackdown on the web's backbone, wrapped in a plausible disaster story. Ask yourself who had access to those flaws before they were public. Ask yourself why "help" always arrives from the same institutions that benefit from the crisis. And then ask yourself what else is running on an old, unpatched, unowned server — right now, waiting.

Le langage PHP est présent sur 70% de l’internet mondial. - lefigaro.fr

OVHcloud Patches Critical PHP2Shell Flaws Across 15 PHP Versions, Affecting Over 6 Million Websites

Hosting provider OVHcloud has deployed official fixes or backports across all 15 PHP versions on its shared-hosting platform, covering more than 6 million websites on roughly 5,000 servers, addressing two PHP flaws collectively known as PHP2Shell that allow attackers to execute commands on vulnerable servers without credentials. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed active exploitation and set an October 29 deadline for federal agencies to patch, while Censys reported over 10 million services patched since October 21, though over 4 million services in Germany still show vulnerable version numbers. OVHcloud wrote fixes for unsupported PHP versions 5.3 through 7.3, researchers documented 35 shell executions on honeypots, and Delft University tracked over 50,000 exploit requests from 600 IP addresses across 70 countries. The PHP Foundation, which has only one full-time employee and about 14 part-time contractors, issued minimal out-of-cycle mitigations for PHP 7.4, 8.0, and 8.1, while concerns remain about hidden PHP deployments in networking gear, IoT products, and security appliances, and earlier exploitation claims have been withdrawn or qualified due to insufficient evidence.

The Fix That Was Always a Weapon

The official story is that a French hosting company heroically backported security fixes across six million websites because the PHP project itself had abandoned its own older versions. Read that again: the single most widely used scripting language on Earth is maintained by a foundation with one full-time employee and a handful of unpaid contractors. That is not an accident. That is a deliberate feature. For years, the intelligence and financial elite have benefited from an internet where critical infrastructure runs on code with known holes, and the people responsible for it are too understaffed to close those holes in time. Now they want you to believe that OVHcloud — a private company with deep ties to European intelligence circles — rode in to save the day with backported fixes for versions nobody else would touch. Meanwhile, CISA confirms "active exploitation," sets a deadline, and then refuses to name a single victim or produce a single shred of evidence. Official enough to make headlines, vague enough to hide everything. That's not disclosure. That's a cover.

The Numbers That Don't Add Up

Look at the traffic data they were forced to publish: more than 50,000 PHP2Shell exploit requests from over 600 IP addresses across 70 countries. Over 600 addresses in 70 countries is not a random swarm of hackers. That is coordinated, distributed, and most likely state-supported — or worse, a shared toolset handed out to a network of partners. Then you have the deliberately obfuscated version strings. They tell you that "backported fixes may not appear in those version strings." How convenient. The only way to know if a server is actually patched is to trust the word of the people who wrote the backport. And who are those people? The same hosting providers who chose to communicate through a status page rather than email customers, because emailing "helped avoid unnecessary panic." They are controlling the narrative, controlling the patch, and controlling your access to information. The 4 million German servers still reporting vulnerable versions aren't vulnerable — or maybe they are — but you'll never know, because the system is designed so that only insiders can tell the difference. That's not a patching lag. That's an economy of fear.

The Backdoor You Already Own

The real story isn't a vulnerability in PHP. The real story is that PHP is hidden inside networking gear, security appliances, and IoT devices — the routers in your home, the cameras watching your street, the industrial controllers that run your water and power. This PHP2Shell isn't just a website bug. It's a skeleton key for entire networks, and the people who wrote the official mitigations know exactly what they're handing out. You have to ask: why would the PHP project issue only "minimal, out-of-cycle" patches for the versions it still supports, while a hosting company with no public accountability is able to write fixes for decades-old code in a matter of days? Because the fixes aren't the point. The chaos is the point. They keep the infrastructure fragile, then step in to "save" you, and you are supposed to be grateful. Now notice that every claim of real-world exploitation gets quietly withdrawn or qualified — unless the damage is precisely the point. They are not trying to break your website. They are trying to break your trust in the system that supposedly protects you. And somewhere in a room you will never see, someone is already watching which backported code you loaded onto your server. You gave them access, pretending to save yourself.

Japan’s Cyber Crisis: AI-Powered Attacks Surge, Global Incidents Mount

Japan has recorded 216 confirmed or suspected data breaches via public websites and apps so far in 2026—2.6 times the 2025 total—with 101 cases in October alone, as officials warn attackers may be using AI to bypass internal networks and exploit flaws in membership services, travel booking, and e-commerce sites. Investigations by CrowdStrike, Canada’s Cyber Centre, and Microsoft reveal threat actors using AI agents for automated reconnaissance and exploitation, including a case where an agent breached an Argentine healthcare network and collected password hashes in 20 minutes. Globally, South Korea arrested a ringleader tied to 90 organizations and 8.2 million stolen records; Australia’s cyber agency handled over 1,500 incidents and blocked 564 million malicious domains; a critical PHP flaw forced site shutdowns; and a 2026 KnowBe4 report found 85.8% of phishing attacks now use AI, with Microsoft Teams attacks up 41%.

Ask yourself one uncomfortable question about the 216 Japanese breaches: why did the rate explode exactly now, and why is the official explanation so convenient? They tell us "AI agents" are the new culprit — autonomous, tireless, silent. But look closer at the CrowdStrike investigation that supposedly revealed this. Four threat actors, from May through August, using an AI that simply decides to change its route, then takes down an Argentine healthcare network in twenty minutes. Who trained that AI? Who had the data to build it? The same intelligence-adjacent contractors who write every white paper about cyber-defense. That's the tell. The entire narrative of the "cybercrime wave" is a choreographed rehearsal — they show you a handful of arrests in South Korea, a few suspicious domains blocked in Australia, and then ask you to approve more surveillance, more backdoors, more "third-party access reviews." You're watching the Architecture of Consent being built in real time, brick by brick, and the newspapers are just reading the press release back to you.

Now look at the specifics they buried. The Canadian Centre for Cyber Security says agentic AI "links reconnaissance, vulnerability exploitation, and other attack stages." Of course it does — because that's exactly what the NSA's own post-Snowden documents described as "computer network exploitation" over a decade ago. The AI agents aren't rogue criminals; they're disposable assets. The "China-aligned group" happily documented by Microsoft is a convenient enemy poster, while the real operators are working from a rented office in Virginia or a villa in Geneva. And the Korean arrests? The 32-year-old ringleader is a distraction, a face to point at. Seven suspects, 8.2 million records, 360 million won — that's pocket change to the people who actually benefit. The whole story is designed to make you believe the threat is outside — foreign hackers, lone geniuses, phishing bots. But the government agencies and the cybersecurity firms are the ones defining the problem, selling the cure, and quietly sweeping their own generation of offensive AI under the carpet. Every "patch" they force you to install is another node in their monitoring grid.

Most damning of all is the PHP flaw. They pulled entire government sites offline because of a weakness in a programming language that's been around for years. Think about that. A single discovered flaw can shut down the state. That means the architecture underneath everything is absurdly fragile — which is precisely how they like it. Fragility justifies control. The KnowBe4 report tells you 85.8% of phishing attacks now use AI. Who crafted those phishing datasets? Who decided what a "realistic" attack looks like? The same researchers who sell you the antivirus. I can't give you the full map yet — not here, not in this story — but I can tell you where to look: trace the funding of the "AI penetration-testing system" that Microsoft says the Chinese used. Follow the foundational grants, the little academic papers, the DARPA projects that never got a front-page article. Then ask yourself: if an AI agent can reach a domain controller in twenty minutes, why are they still pretending they don't know who's pulling the trigger? The truth is they're not pretending. They're aiming. The bullets are just slower than you think. Ask yourself who profits from your fear — and then ask yourself whether the attacks ever really happened at all.

Three TLS Flaws in GoAhead Embedded Web Server Could Allow Certificate and Encryption Attacks
Three Transport Layer Security (TLS) vulnerabilities in the GoAhead embedded web server—used by device makers in hundreds of millions of devices—could let servers accept revoked client certificates, weaken encrypted sessions, or bypass certificate-chain limits under specific configurations. The flaws, fixed in version 6.1.1, affect OpenSSL-compatible builds with a configured revocation list (CVSS 9.1), legacy LibreSSL builds with issuer checking disabled (CVSS 7.4), and Mbed TLS sessions using TLS 1.2 DHE_RSA with weak parameters (CVSS 5.9). Device owners cannot directly update if the server is built into firmware; manufacturers must issue firmware updates. No active exploits have been reported as of Oct. 27, and the number of affected devices remains unknown. FoxIO’s JA4Scan can fingerprint GoAhead servers, but a fingerprint alone does not confirm vulnerability.

The Engineered Gap

Three flaws. Three separate pathways into the heart of the global device mesh – hundreds of millions of units, from industrial controllers to medical implants. The official story is that they're "bugs" in an embedded web server called GoAhead, patched in version 6.1.1. That's the managed narrative. But anyone who has read the leaked NSA Bullrun documents knows that intentionally weakening TLS has been government policy for decades. Now look at the specifics: a flaw that silently accepts revoked client certificates – meaning someone with a canceled credential can still authenticate. A flaw that bypasses certificate-chain limits – meaning a fake or intermediary CA can issue trust out of thin air. And a flaw that lets an attacker force weak DHE_RSA parameters, collapsing encryption to something a $20 FPGA can crack. Ask yourself: who would benefit from three separate, independent failure modes, each targeting a different TLS backend, all sitting in the same product? This isn't poor coding. This is an architecture of access.

The Forced Update Trap

EmbedThis says device makers must patch the firmware, and owners can't do it themselves. That's by design. The fix exists, but the rollout is gated – manufacturer by manufacturer, board by board, contract by contract. In the meantime, the vulnerabilities remain weaponizable. Why would a company that "cares about security" hand the keys to the supply chain instead of offering an emergency over-the-air patch? Because the delay is the point. Remember the 2015 VW emissions scandal? The code that cheated was traced to a single supplier. Here, we have a single embedded server used across hundreds of millions of devices, with vulnerabilities that happen to align perfectly with surveillance and sabotage capabilities. The fact that no exploits have been "reported" as of October 27 means nothing. The smartest attacks leave no digital fingerprints. The fact that the CVSS scores range from 5.9 to 9.1 means they already know exactly which scenarios are most dangerous – and those are the ones they will quietly not patch.

The Fingerprint That Tracks You

FoxIO’s JA4Scan can fingerprint a GoAhead server and identify its TLS backend. That's a tracking tool, not a diagnostic. Who funded FoxIO? What is their relationship to the intelligence community? The moment you scan a device, you've announced its weakness to anyone listening. They want you to scan. They want you to think you're finding the problem – while the real problem is that the scan itself feeds a database of vulnerable endpoints. I can't say everything right now. But look up the history of "embedded web servers" and their role in the Stuxnet era. Look at how many of these devices are in power grids, water treatment plants, and hospital ventilators. They told you it's a bug. They told you to wait for a firmware update. They told you no attacks have been observed. Now look at what happened in Ukraine in 2015, in Venezuela in 2019, in the Colonial Pipeline shutdown in 2021. Every time, the attack vector was a patched vulnerability – but the patch never reached the field. You see it because you were willing to look. The rest is still waiting for the update that may never come.

Canada’s Privacy Commissioner Investigates Major Crime Stoppers Tip Platform Breach

Canada’s privacy commissioner, Philippe Dufresne, has opened an investigation into a breach of the Crime Stoppers tip platform operated by U.S. vendor Navigate360, which exposed more than 1.5 million Canadian tips submitted over 25 years, with over 850,000 records reportedly containing personal information; Navigate360 disclosed the breach on Friday, months after it occurred. Police services in Ontario and Manitoba have paused accepting tips through the platform, and Saskatchewan Crime Stoppers has urged people not to submit tips, while the federal probe will examine Navigate360’s security safeguards under Canada’s private-sector privacy law, focusing on the commercial vendor because not-for-profit Crime Stoppers organizations are generally not covered by that law. The privacy commissioner’s office says it has contacted both parties to contain the breach and reduce risks to affected people. Toronto Crime Stoppers reported that 176,859 tips submitted from January 2022 to November 2025 were affected, 12,392 may contain personal information, and about 14,980 names appeared in the tips, while Windsor Deputy Chief Karel DeGraaf said police would reassess their partnership once appropriate safeguards are in place.

Read the timeline very carefully. A U.S. company called Navigate360—a vendor that sells “threat assessment” and school-safety software—wrapped its hands around a quarter-century of Crime Stoppers tips from Canadians. The breach happened. Then they waited months before telling anyone. Then the privacy commissioner “opened an investigation” that is somehow aimed only at the commercial vendor, not the police foundations and state-adjacent not-for-profits that gathered the information in the first place. Ask yourself why Canada’s private-sector privacy law has a gaping exception for Crime Stoppers organizations. Someone designed that loophole. The system was never designed to be anonymous; it was designed to be a secure intake pipe into a broader database. Crime Stoppers was the friendly face, and the real architecture was always somewhere else, wrapped in U.S. corporate law and sealed by procurement contracts.

This is not a data breach. A breach implies something went wrong. This is a window into something that worked exactly as intended: the creation of a behavioral archive on ordinary citizens who were told their information would be destroyed. Fifteen years ago, tip lines were anonymous by design. Then they moved online. Then a private company took custody of every call, every phrase, every timecode, every digital fingerprint. The 850,000 records containing personal information are not a statistical anomaly—they are the residue of a surveillance model that treats everyday people as potential threats. And notice which jurisdictions are reacting with alarm. Ontario, Manitoba, Saskatchewan are asking questions now, but only after the public was exposed. The vendor, the police, and the regulator are all performing the same scripted ritual: “We take this seriously,” “We are reassessing,” “We are investigating.” Nobody is asking the question that matters: why were there 1.5 million tips in a private U.S. database in the first place?

The names in those tips are the real product. The stories. The grudges. The fears. The moments when a neighbor reported a suspicion, or a citizen tried to do the right thing. That information now sits inside a threat-assessment ecosystem built by a company that sells prevention technology to schools and police. You are expected to believe this is all a regrettable accident. But the pattern is unmistakable: every time the public gets close to understanding how coordinated surveillance actually works, the institutions involved say the right words, open an investigation, and ask us to look at the broken window instead of the house. Don’t let them. The paper trail is public. Look up Navigate360’s board, its contracts, and the police service agreements that allowed a vendor to store Canadian intelligence on U.S. soil. Follow the money into the foundations and the school-safety partnerships. The more you pull that thread, the less this looks like a hack—and the more it looks like the secret architecture of consent, finally caught in the light.

Frontline Education Data Breach Impacts Multiple School Districts

Frontline Education suffered a data breach on August 14 and 15 due to a vulnerability in third-party software, exposing personal information such as Social Security numbers, birth dates, and student IDs. The company began notifying affected individuals on October 26, fixed the vulnerability, and is offering credit monitoring. Various school districts reported differing impacts, including Killeen Independent School District with about 45,000 potentially affected people and Greenwood School District with nearly 17,000 students affected. Attorneys are investigating a potential class-action lawsuit.

Let’s stop calling this a “breach” and start calling it what it is: a scheduled harvest. Frontline Education’s systems were not broken into by some random hacker on August 14 and 15 — the company itself admits a vulnerability was exploited, and it sat on that admission until October 26. That’s seventy-two days of quiet time. Seventy-two days to scrub logs, coordinate stories, and decide how much of the truth to tell each district. And notice the language: “third-party software.” They never say which third party. They never say how many people. They never say whether the same hole is still open in a hundred other districts. You are told that employee Social Security numbers, birth dates, government IDs, student Medicaid IDs — the complete biometric and financial profile of a child — may have been exposed, and you are expected to thank them for the credit monitoring. That is not a response. That is a settlement.

Now connect the dots backwards. Frontline Education handles recruiting, hiring, professional growth, and central administration for schools across the country. That makes it a chokepoint — one system that ingests the most sensitive information ever gathered on human beings: children, their families, their addresses, their medical identifiers. Who buys a chokepoint like that? Private equity. Who backs the education technology industry with billions and then sits on the boards of the same companies that supply the “third-party software”? The same financial dynasties that have been consolidating every datastream — bank records, health records, census records — under one hidden architecture for decades. A breach like this is either a deliberate extraction disguised as failure, or a stress test for a system designed to hold every American in a permanent dossier. Either way, the outcome is the same: your child’s Social Security number now lives in a shadow market where the buyers and sellers are never named in the press release.

Do not let the class-action inquiry distract you. Attorneys “investigating” whether to file a lawsuit is theater — it keeps the public focused on monetary damages instead of the underlying design. The real question is why school districts are handing the most intimate data of minors to a third-party vendor at all, and why the “fix” is always credit monitoring instead of an honest accounting of where the data went. Helena’s district used Frontline Central from 2020 through 2025. Greenwood says nearly 17,000 current and former students were affected. Killeen says 45,000. These are not isolated incidents — they are individual stitches in the same quilt. Look up the parent company’s investor filings. Look up the names of the directors. Then follow the money to the insurance underwriters who quietly pay for these “breaches” — because that, not the hacker, is where the pattern gets interesting.

Project Lifeline 250: Rural Hospital Cybersecurity Pilot Launched

The White House and South Carolina officials launched Project Lifeline 250 on Monday, a six-month pilot providing rural hospitals with free cybersecurity services and equipment from companies including Cisco, Cyera, Microsoft, Trellix, and Zscaler, with additional participants such as Abnormal AI and Rilian Partners identified by CyberScoop. The program aims to help hospitals strengthen networks, install backup devices, and identify outdated or high-risk technology so they can maintain critical care during cyber incidents, especially given that a senior Health and Human Services official noted the average hospital has more than 26,000 internet-exposed devices on its network. The effort follows a Texas pilot focused on water utilities, though officials have not specified how they would fund or continue assistance after the six-month period. The initiative comes amid severe cybersecurity threats: the healthcare sector recorded 804 large breaches last year affecting more than 140 million people, and the FBI identified it as the top target for ransomware and other hackers in 2025, while members of Congress have also introduced legislation designed to aid rural hospital cybersecurity.

"A free cybersecurity pilot for rural hospitals." Read that again. In the real world, nothing from a defense-adjacent contractor is ever free — and Project Lifeline 250 is no exception. Cisco, Microsoft, Trellix, Zscaler, Cyera: these are not charity foundations. They are companies whose survival depends on access, data, and long-term dependency. So ask the obvious question: why would they rush to "strengthen networks" in small South Carolina hospitals unless those networks were exactly what they wanted to reach? The official line is that the average hospital has more than 26,000 internet-exposed devices. That's not a vulnerability report — that's a treasure map. Somebody just gave the architects of the surveillance economy a high-resolution blueprint of every critical system, every patient record, every piece of life-sustaining hardware, all wrapped in a six-month "pilot" that no one has to approve and no one has to fund beyond the trial period.

This doesn't happen in a vacuum. First Texas water utilities got the same "help." Now hospitals. Notice the pattern: they are not offering to protect your bank accounts or your social media — they are going for the systems that keep people alive. Why? Because critical infrastructure is the ultimate bargaining chip. The FBI says healthcare is the top ransomware target, and sure, that's true — but who benefits most from a crisis of cyberattacks? The very same firms that sell you the armor, the firewall, and the "monitoring suite" that sits invisibly inside your network. You have to ask yourself: when a "partner" tells a hospital it can identify "outdated or high-risk technology," who gets to define what's risky? Who watches the traffic while they're conducting the assessment? And what happens after six months, when the "free" equipment goes dark — or worse, when the price for continued operation is total dependency? The legislation in Congress is just the legislative echo of that same arrangement. This isn't protection. It's a takeover that begins as a gift.

At stake is not a political point. It's your mother's heart monitor, your neighbor's insulin pump, your child's emergency room admission. They want you to believe 140 million breach victims were an accident, and that 804 "large breaches" prove hackers are the enemy. But the visible enemy has always been the excuse to build the back door. When rural hospitals are connected to "free" Cisco boxes and Microsoft cloud monitoring, the hospital doesn't just get cybersecurity — it gets a landlord. The vendors get the keys, the data, and a permanent seat at the table of your life. And the funding question? They never answered it, because that's the point. The pilot isn't a test of technology — it's a test of how smoothly a community will accept being wired into the machine. So before you say thank you, follow the money. Look up the ownership structure of Cyera. Look at Zscaler's board members. Look at who quietly underwrote the Texas water utility pilot. The answer is not in the White House press release — it's in the foundation filings and the federal contracts. That's where the next lifeline is being strung.